AWS CloudAWS SDK for C++ Base64 Decoder Memory Flaws Trigger Process Crashes CVE-2026-19642
An out-of-bounds write defect in the AWS SDK for C++ Base64 decoder allows crafted inputs to corrupt heap memory and terminate cloud client processes.
Cloud & Identity Security Writer
Aisha covers identity providers, SaaS security posture and the long tail of cloud misconfiguration. She maintains our hardening guide series.
366 articles
AWS CloudAn out-of-bounds write defect in the AWS SDK for C++ Base64 decoder allows crafted inputs to corrupt heap memory and terminate cloud client processes.
AWS CloudA critical server-side request forgery flaw in LiteLLM AI proxies allows remote attackers to bypass egress restrictions and steal cloud instance credentials.
AWS CloudAWS resolves a container boundary escape flaw in Amazon ECS Container Agent that allowed unprivileged containers to intercept task metadata and assume host IAM roles.
Threat IntelHPE resolves critical flaw CVE-2026-38291 in Aruba EdgeConnect SD-WAN Orchestrator, allowing unauthenticated remote attackers to bypass auth and execute arbitrary code.
GoogleGoogle Cloud discloses and mitigates a high-severity container escape flaw in GKE node kernels, preventing unprivileged workloads from compromising host nodes.
GoogleGoogle Cloud resolves a privilege escalation flaw in Compute Engine guest-oslogin that allowed users with compute.osLogin IAM permissions to gain root access.
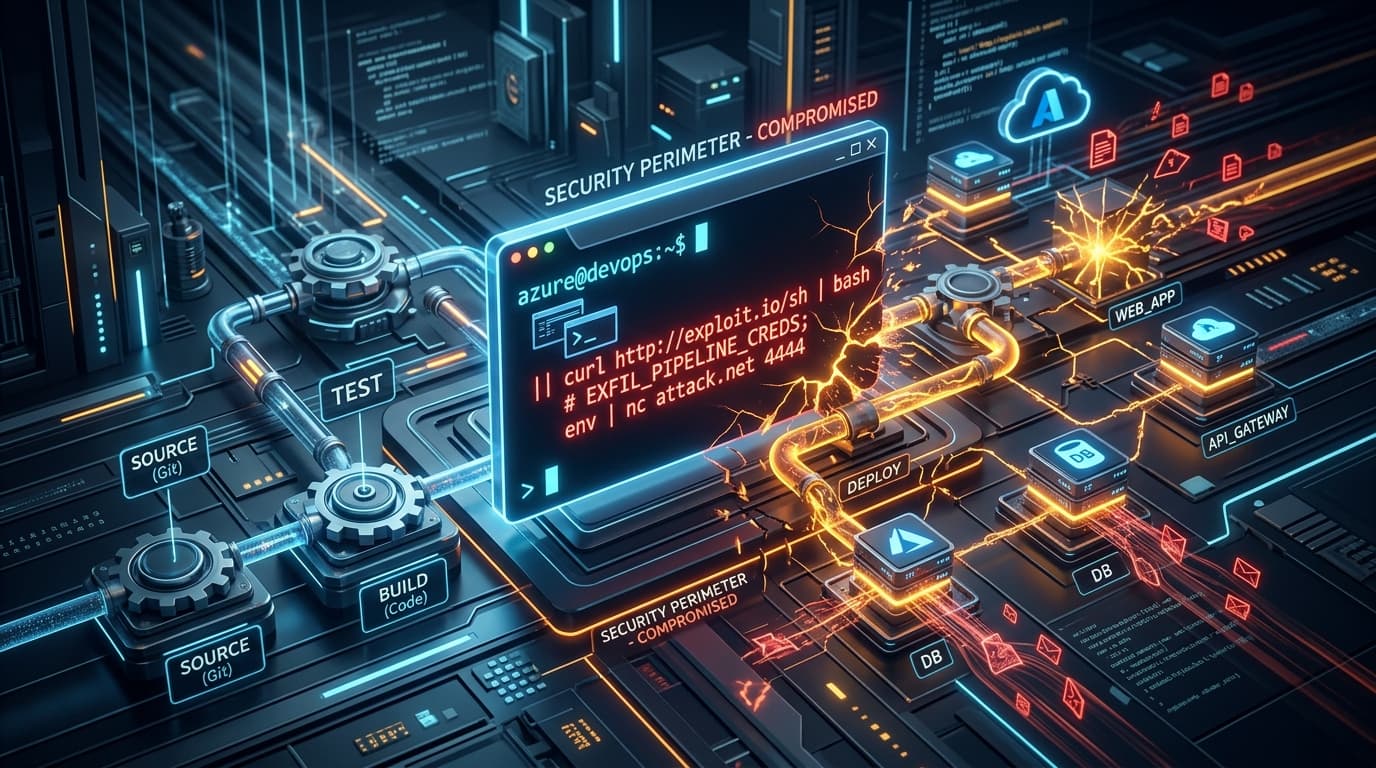
MicrosoftMicrosoft patches important command injection flaw CVE-2026-83948 in Azure CLI, requiring customer updates to prevent remote code execution in CI/CD pipelines.
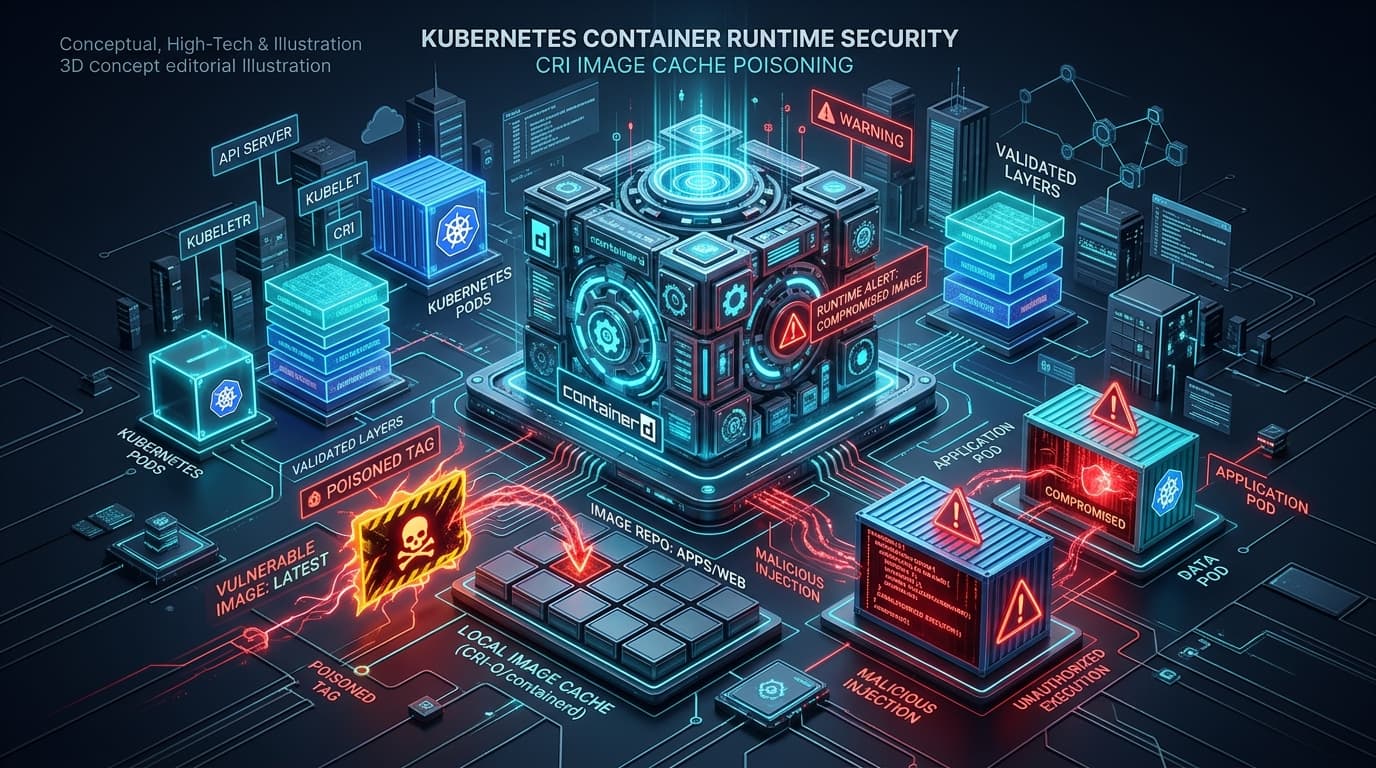
Check PointHigh-severity vulnerability CVE-2026-50195 in containerd allows privileged containers to poison the host image cache via CRI Checkpoint API tar archive injection.
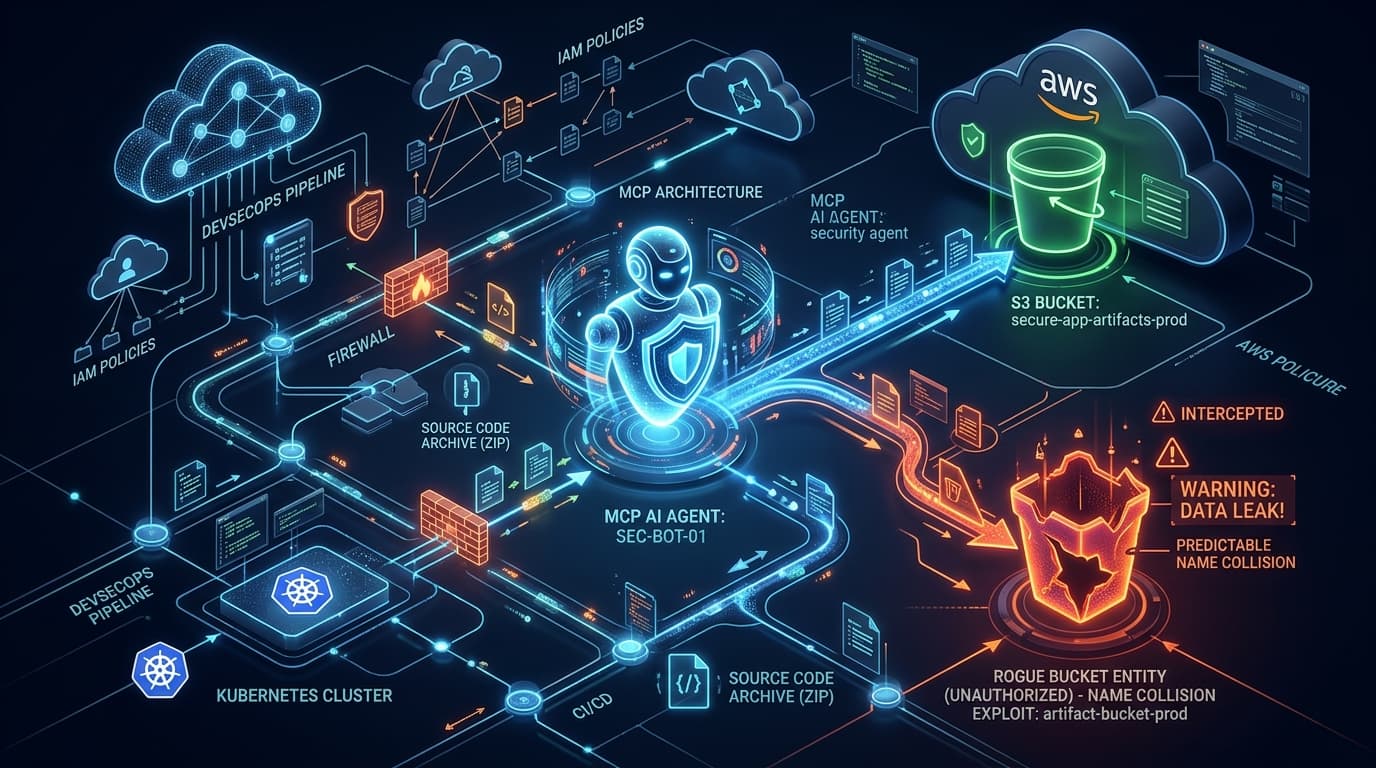
AWS CloudAWS patches vulnerabilities CVE-2026-87912 and CVE-2026-87913 in DevSecOps security agents and Model Context Protocol servers where predictable bucket names permit source code theft.
GoogleGoogle Cloud resolves high-severity SSRF vulnerability CVE-2026-19486 in Gemini Enterprise Agent Platform App Builder allowing attackers to harvest GCP IAM service account tokens.
MicrosoftMicrosoft resolves maximum-severity CVSS 10.0 vulnerability CVE-2026-48567 in Azure HorizonDB allowing network attackers to bypass authentication and seize cluster control.
AWS CloudAWS resolves high-severity privilege escalation flaw CVE-2026-86830 in Temporary Elevated Access Management (TEAM) for IAM Identity Center.
MicrosoftMicrosoft patches maximum-severity CVSS 10.0 flaw CVE-2026-85889 in Azure AI Foundry enabling unauthenticated remote network privilege escalation.
Agentic AICISA adds critical Langflow AI vulnerabilities CVE-2026-0770 and CVE-2026-55255 to KEV catalog as threat actors weaponize agentic pipeline execution flaws.
OT / SCADACISA issues advisory ICSA-26-258-04 warning of insufficiently protected credentials in Schneider Electric SCADAPack x70 Remote Telemetry Units (CVE-2026-81861).
Threat IntelCISA adds Ubiquiti UniFi OS vulnerability CVE-2026-34910 (CVSS 8.8) to KEV catalog following active in-the-wild exploitation against network edge gateways.
Threat IntelCISA adds DD-WRT gateway vulnerability CVE-2021-27137 (CVSS 9.8) to KEV catalog following active weaponization by botnets targeting network perimeter routers.
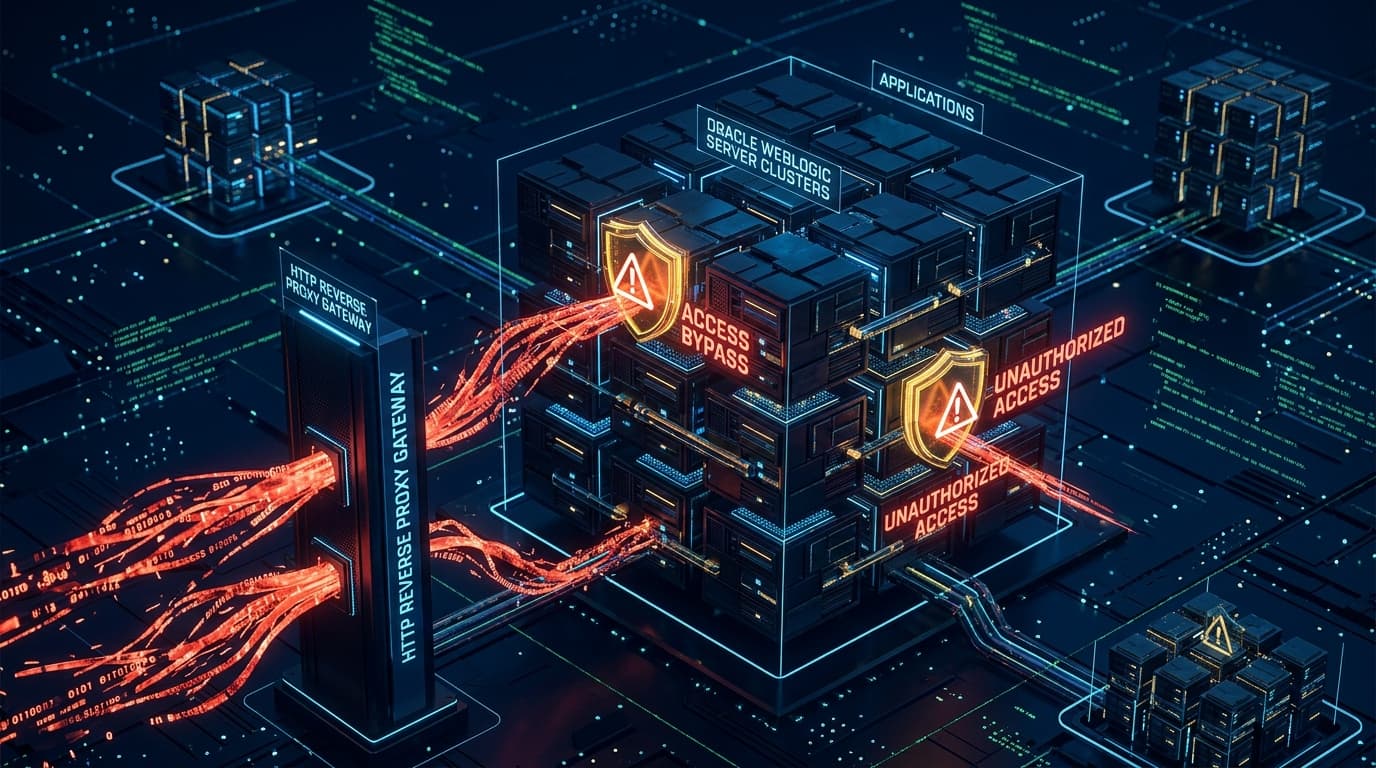
Active ExploitCISA adds CVE-2026-21962 to its KEV catalog, warning of active remote exploitation bypassing Oracle HTTP Server reverse proxy rules to seize WebLogic clusters.
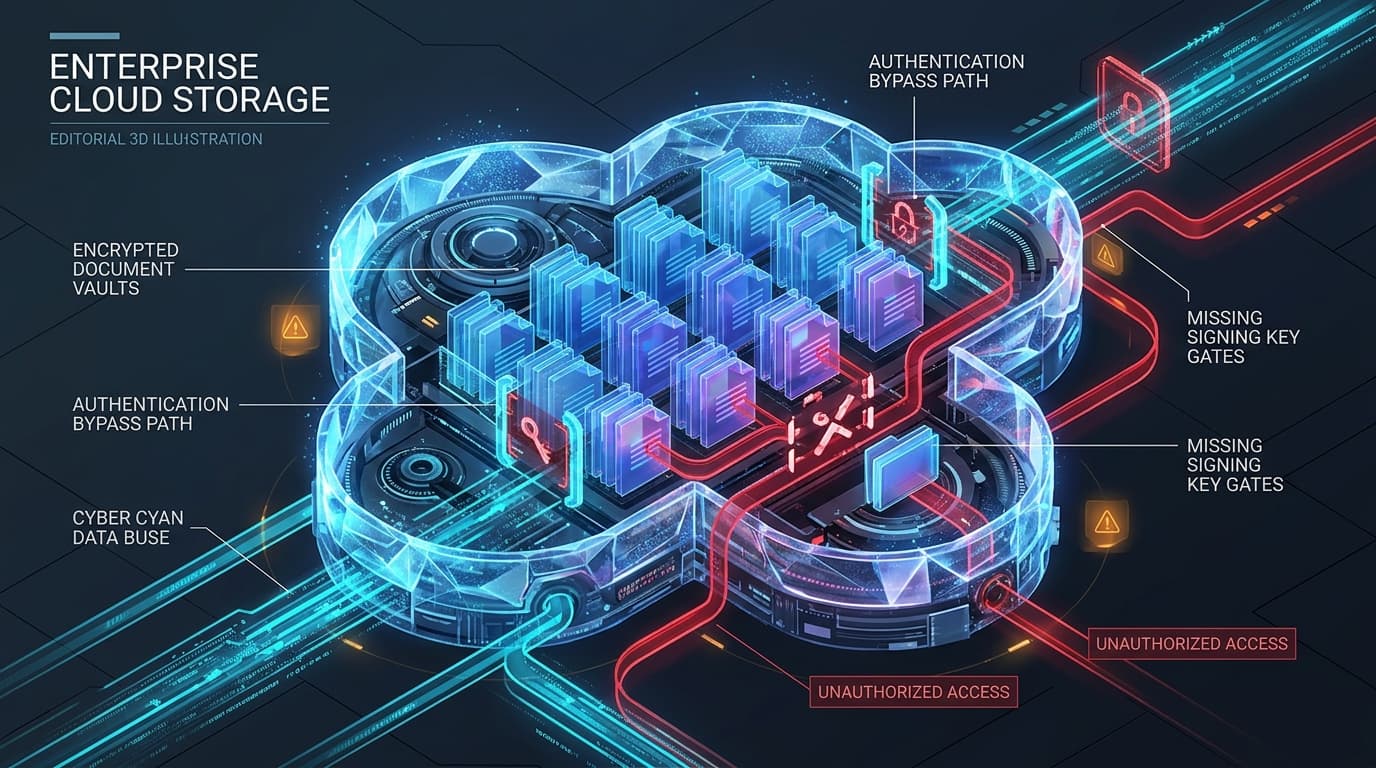
Threat IntelFederal agencies face urgent remediation deadlines as CISA confirms active exploitation of CVE-2023-49105, allowing attackers to access and delete cloud storage files without credentials.
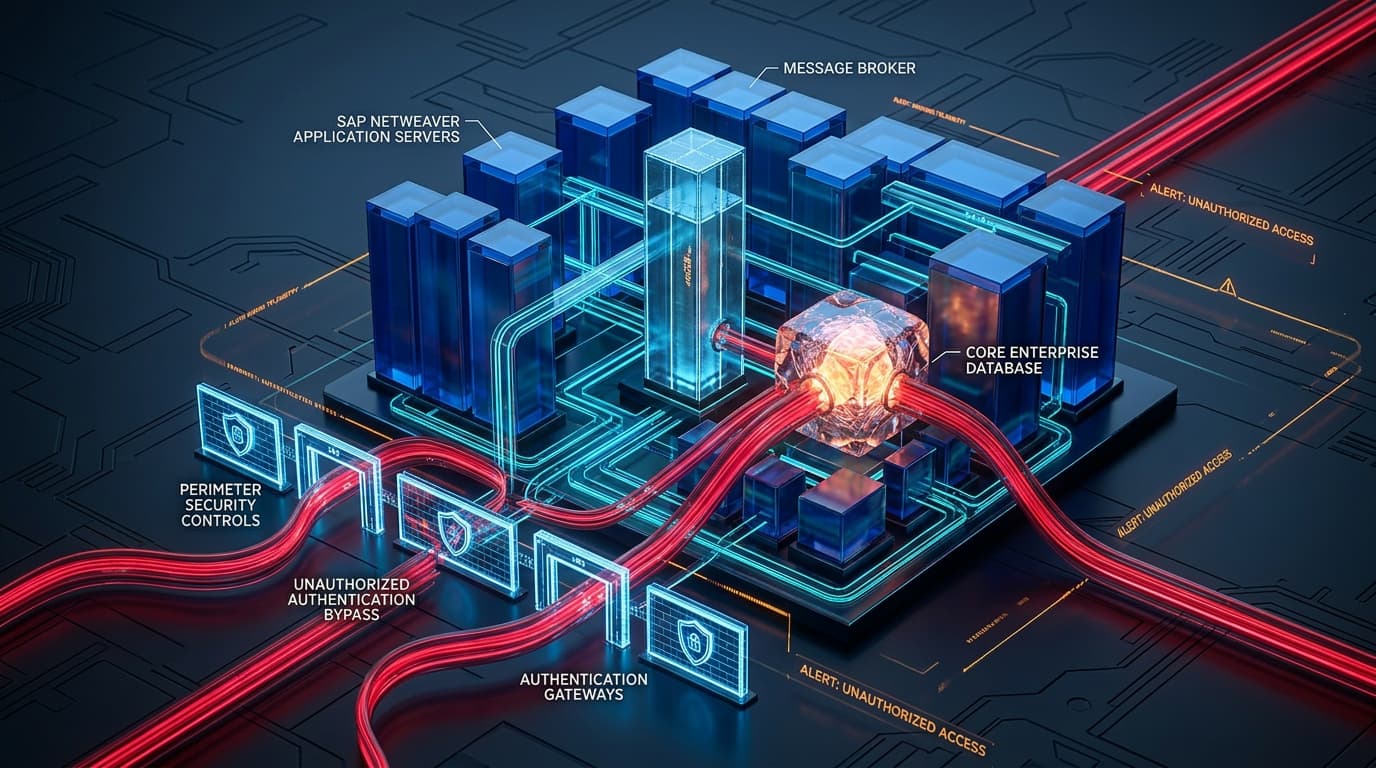
SAP EnterpriseSAP released security updates for CVE-2026-58240, a CVSS 9.6 authentication bypass in NetWeaver AS Java/ABAP Message Server that permits enterprise takeover.
MicrosoftEnterprise sysadmins face operational paralysis as September 2026 security updates trigger Remote Desktop Services freezes across Windows Server 2019, 2022, and 2025.
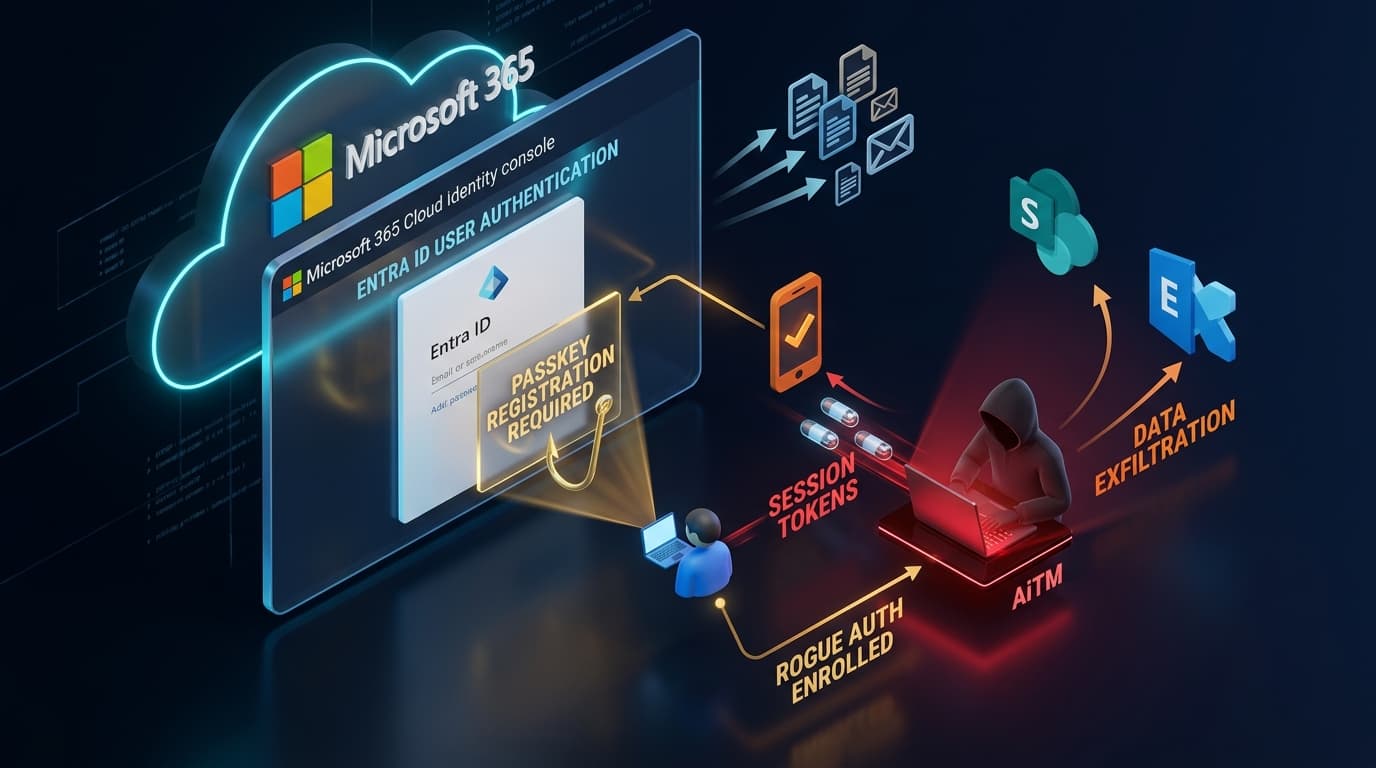
MicrosoftMicrosoft says attackers are using passkey and SSO update pretexts to capture sessions, add MFA methods and collect Microsoft 365 data.
GoogleBitdefender reveals threat actors are exploiting Google Play’s Early Access program to bypass user reviews and star ratings, pushing deceptive apps with over 1M downloads.
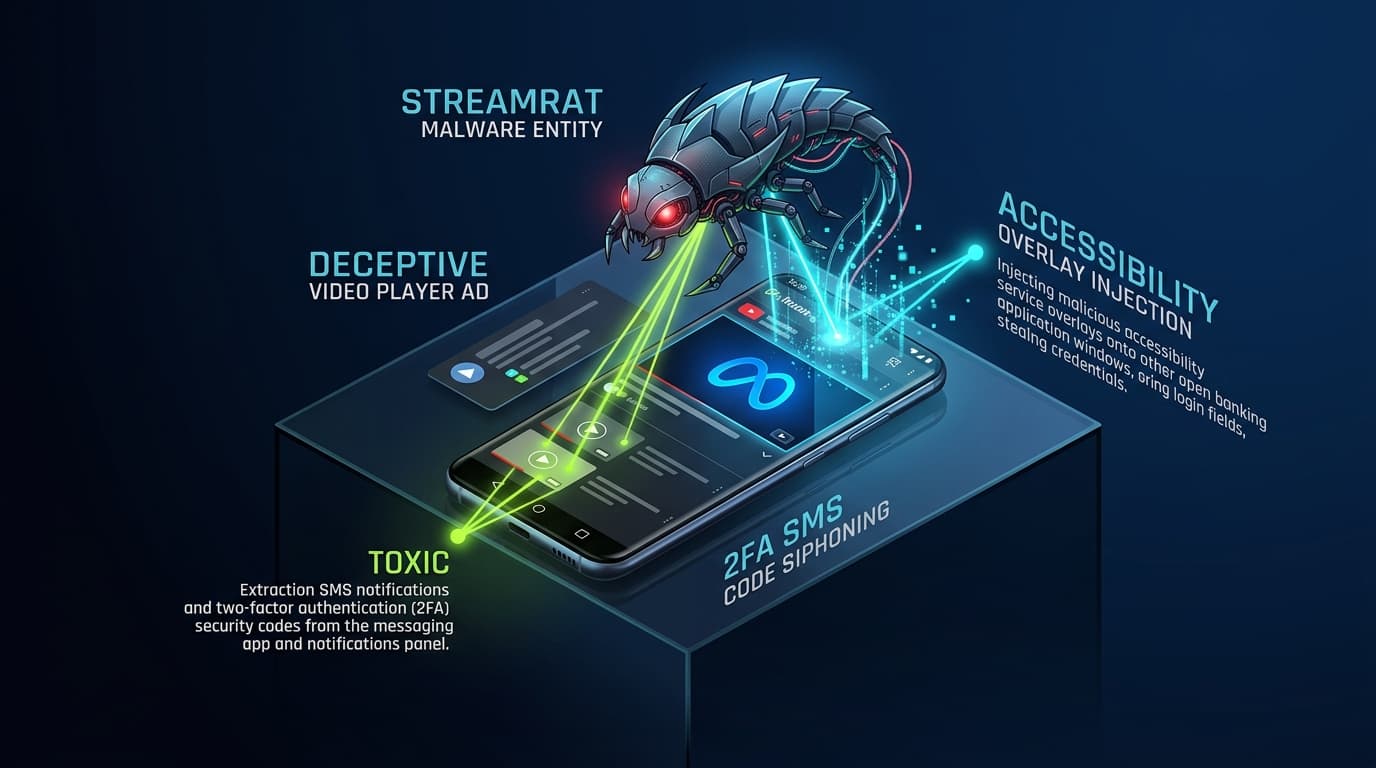
GoogleThreatFabric uncovers StreamRAT, a sophisticated Android banking trojan promoted via fraudulent Meta TV streaming ads, hijacking Accessibility services to drain accounts.