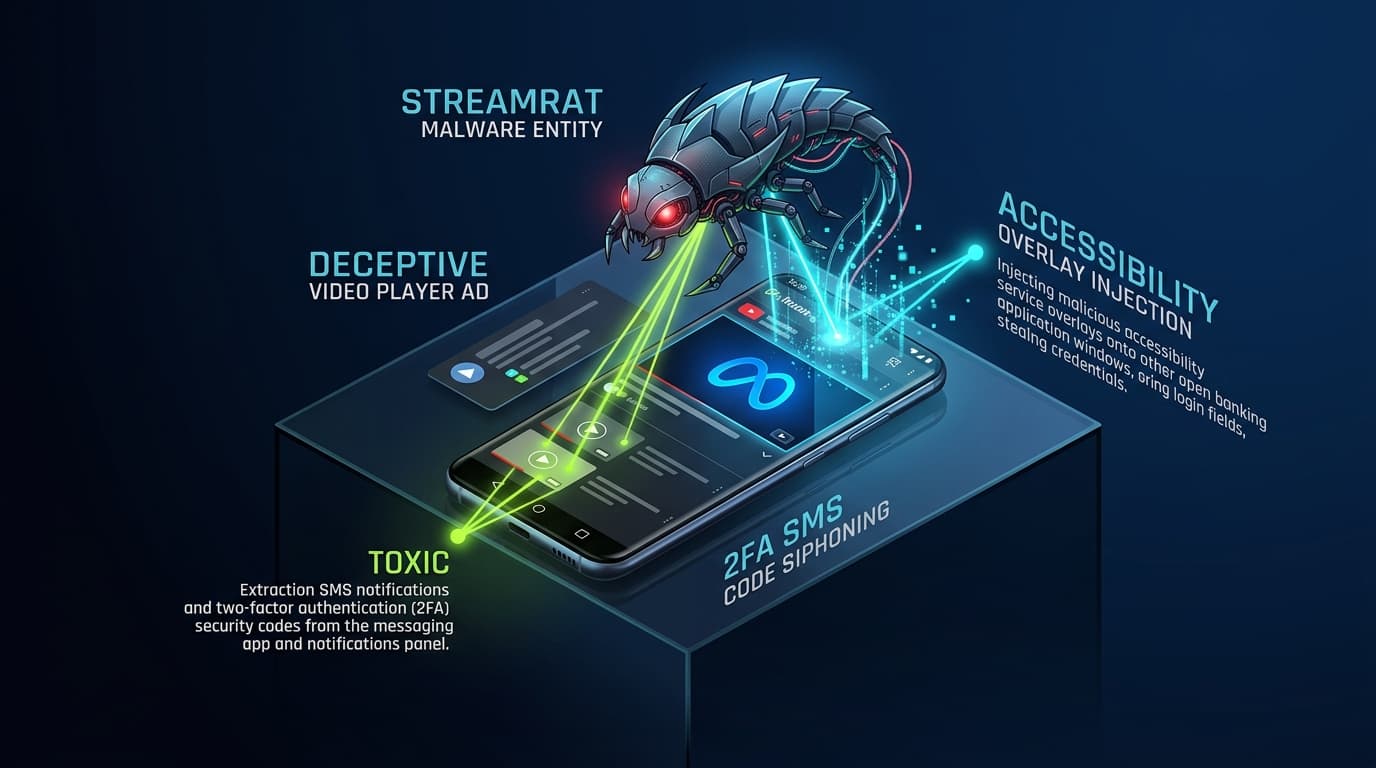
Mobile security researchers at ThreatFabric have disclosed technical details regarding StreamRAT, a newly discovered, highly capable Android banking trojan that targeted over 570,000 users in the European Union through fraudulent streaming advertisements on Meta platforms.
The campaign, focused primarily on Spanish-speaking banking customers, combines deceptive social-media malvertising with sophisticated device takeover techniques that bypass modern Android security boundaries.
Multi-Stage Sideloading Architecture
The infection chain begins when a user clicks a sponsored Meta ad offering free premium sports and television streaming. The link redirects to a dynamic landing page that verifies whether the visitor is connecting from an Android smartphone before presenting an app.apk download button.
Once downloaded and launched, the initial dropper executes an intricate sequence of permission escalations:
- Default Home Application Hijack: The dropper prompts the victim to designate the app as the default Android Home launcher. Whenever the user presses the device Home button, they are returned directly to the malware’s interface.
- Dummy VPN Isolation: Before fetching the secondary payload, the app establishes a local VPN tunnel that routes general traffic into an inactive loopback interface while exempting the malware itself, preventing security software from communicating with threat intelligence servers.
- Accessibility Service Takeover: The dropper installs the core StreamRAT payload (
update_{timestamp}.apk) from the public Downloads folder and guides the victim through enabling Android Accessibility permissions.
"Once Accessibility permissions are granted, the concept of mobile application sandboxing is gone. The malware can read every screen element, capture two-factor SMS codes, and simulate touch events autonomously."
Automated Account Takeover (ATS)
With Accessibility control active, StreamRAT monitors foreground application launches. When the user opens a supported European banking or cryptocurrency application, the malware injects a pixel-perfect credential-harvesting overlay.
Simultaneously, the malware’s Automated Transfer System (ATS) framework enables remote operators to initiate unauthorized wire transfers directly from the victim's device, bypassing device-fingerprinting and behavioral risk scoring systems used by financial institutions.
Protection Advice for Mobile Consumers & Enterprises
To mitigate the risk posed by StreamRAT and similar banking loaders, organizations and consumers should enforce the following safeguards:
- Disable Unknown Sources: Ensure Android devices have APK installations from untrusted sources strictly disabled.
- Scrutinize Accessibility Requests: Media players and streaming applications never require Android Accessibility access. Any consumer utility requesting Accessibility permissions should be treated as malicious immediately.
- Enforce Google Play Protect: Ensure Google Play Protect is enabled, and review active Accessibility service permissions under Settings > Accessibility.