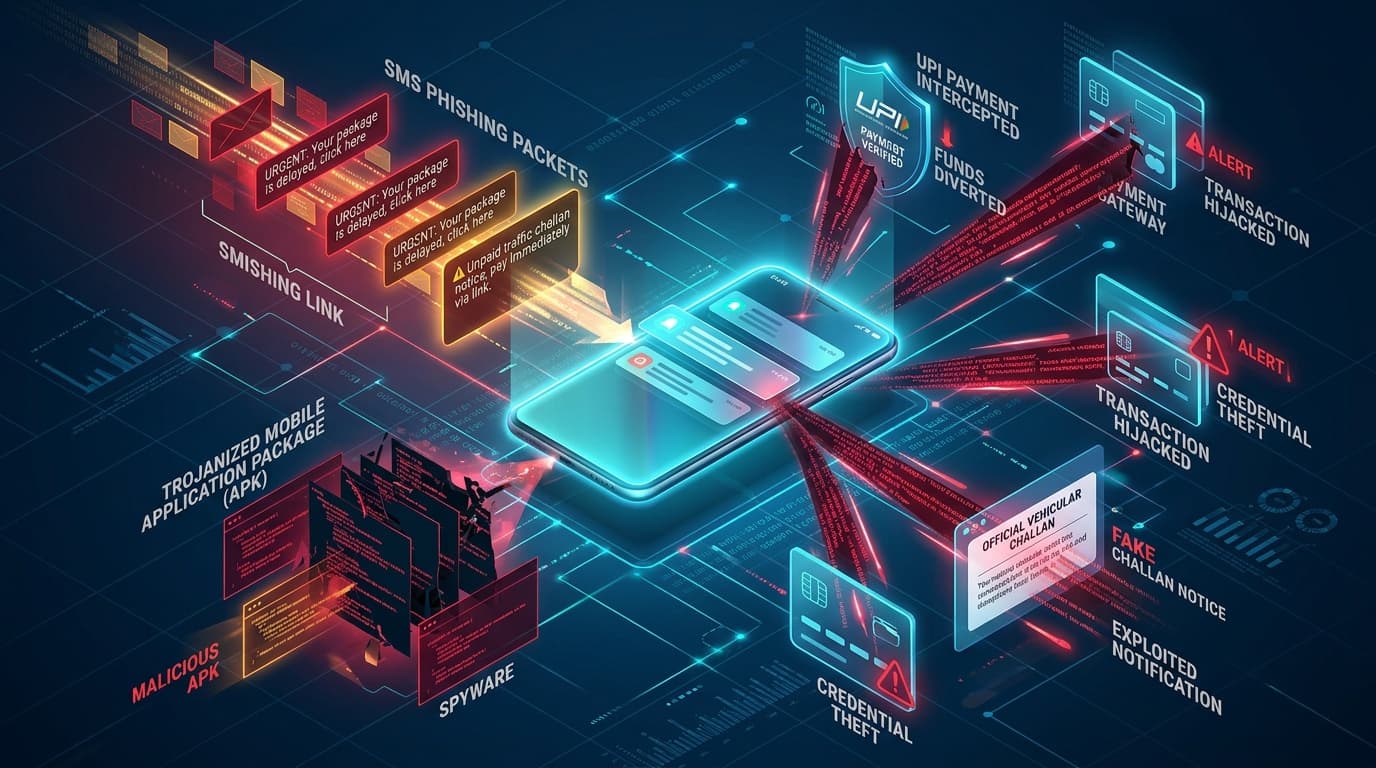
CERT-In issued advisory CIAD-2026-0038 warning against an aggressive smishing blitz delivering trojanized APKs disguised as official Parivahan traffic e-challan notices.
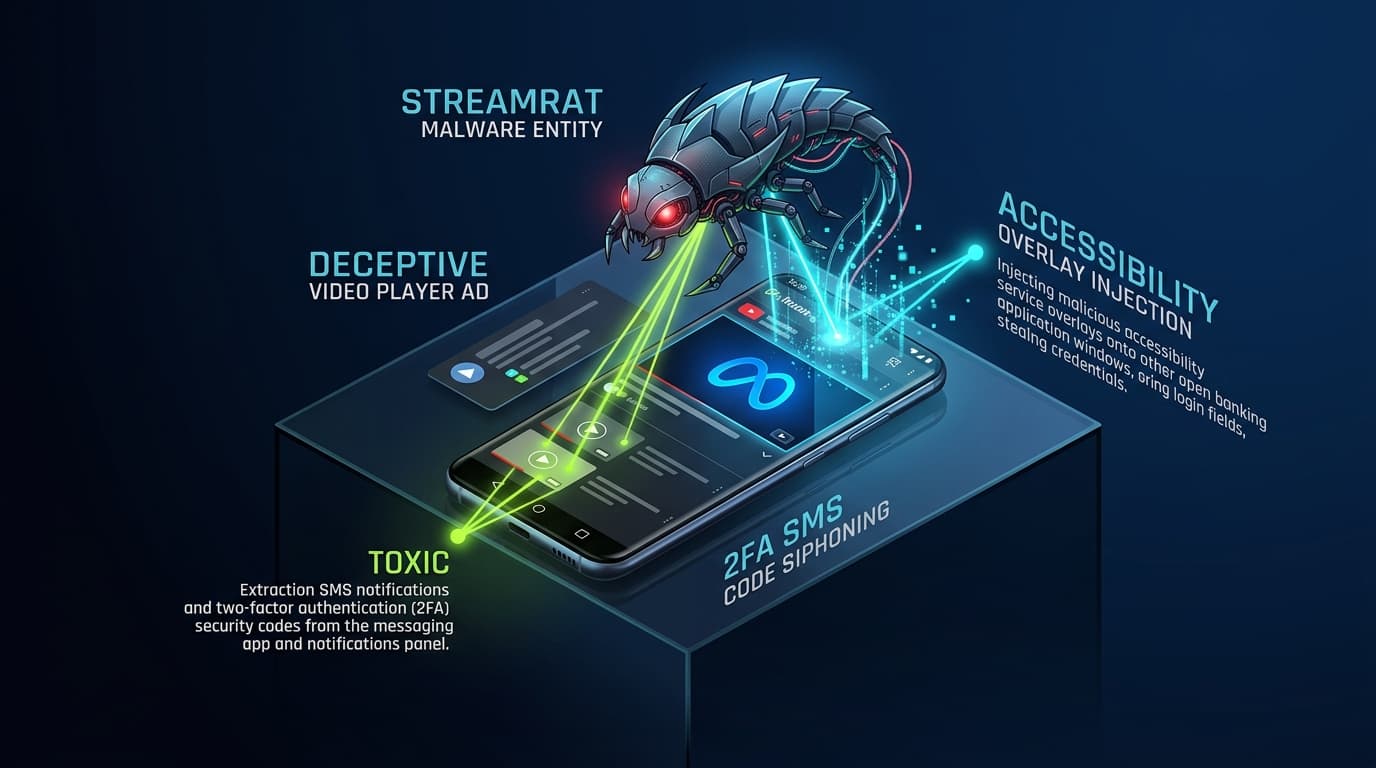
ThreatFabric uncovers StreamRAT, a sophisticated Android banking trojan promoted via fraudulent Meta TV streaming ads, hijacking Accessibility services to drain accounts.
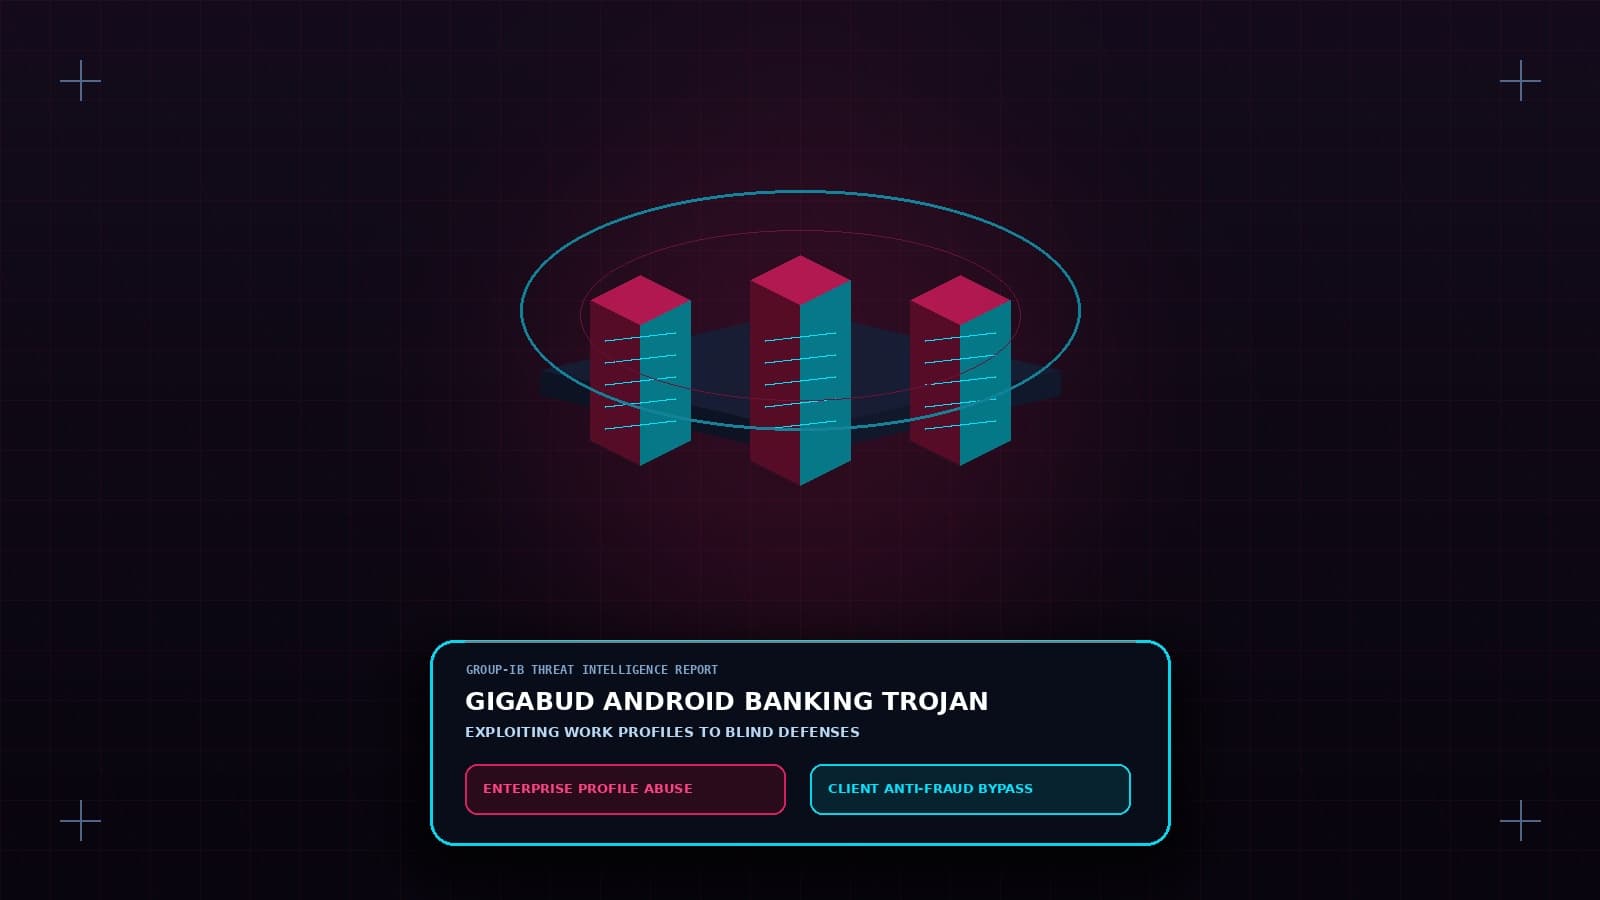
Group-IB uncovered a major evolution in the Gigabud banking trojan, which uses Android enterprise Work Profiles to isolate tampered banking apps and blind client security checks.