Threat IntelLlamaIndex Workflows & Tool Calling Arbitrary Command Execution Flaw CVE-2026-41905
GitHub Security Advisory documents an unauthenticated command injection defect in LlamaIndex Workflows agent tool calling pipelines.
Cloud & Identity Security Writer
Aisha covers identity providers, SaaS security posture and the long tail of cloud misconfiguration. She maintains our hardening guide series.
366 articles
Threat IntelGitHub Security Advisory documents an unauthenticated command injection defect in LlamaIndex Workflows agent tool calling pipelines.
GoogleGoogle Cloud security bulletin resolves a filter evasion flaw in Vertex AI Prompt Armor allowing jailbreak payload delivery to enterprise RAG agents.
Agentic AIRecent CVEs in Ollama and AWS MCP reveal that semantic prompt filters cannot prevent tool injection. Engineering teams must isolate agent tools in ephemeral microVMs.
MicrosoftMicrosoft MSRC advisory documents a critical model-context-protocol tool injection flaw in Azure AI Foundry enabling indirect agentic tool hijacking.
AWS CloudAWS resolved a fail-open defect in Python Lambda Powertools data masking (CVE-2026-104002) that emitted unmasked sensitive records to logs during masking errors.
AWS CloudAWS Security Bulletin 2026-121-AWS addresses an argument injection defect in security-agent-mcp-server diff scanning that permits arbitrary file modification.
Threat IntelA security defect in Ollama experimental agent mode allowed command chaining operators to bypass confirmation gates and execute arbitrary shell commands.
AWS CloudCVE-2026-103956 in AWS Labs Loom (CVSS 10.0) let any network client act as super-admin on IdP-less deployments. Two SSRF flaws leaked tokens. Upgrade to 1.7.0+.
KubernetesDell DSA-2026-448 fixes two CVSS 10 missing-authentication flaws in Container Storage Modules that expose storage admin credentials. Upgrade CSM to 1.18.0.
Threat IntelLiteLLM CVE-2026-93355 lets a signed JWT with an unverified email claim seize any account, including proxy_admin. No fix yet; cache-leak and SSRF CVEs patched.
KubernetesSUSE Rancher CVE-2026-88804 (CVSS 9.6) lets unauthenticated attackers rewrite UI settings, plant login-page script and take over managed Kubernetes clusters.
Threat IntelHPE bulletin HPESBNW05150 fixes 18 Instant On AP flaws, including two CVSS 9.8 unauthenticated RCE bugs (CVE-2026-76721, CVE-2026-76722). Update to 3.4.2.0.
Agentic AIOpenAI dismantled a coordinated campaign that weaponized cross-model replay queries across 15,000 accounts to illicitly extract encrypted chain-of-thought traces.
LinuxA flaw in 389 Directory Server fails to discard buffered plaintext bytes during StartTLS negotiation, enabling on-path attackers to forge successful LDAP authentications.
Threat IntelCISA advisory ICSA-26-272-01 reveals unencrypted update conduits and hardcoded private signing keys in Lantronix G520 gateways, enabling root RCE.
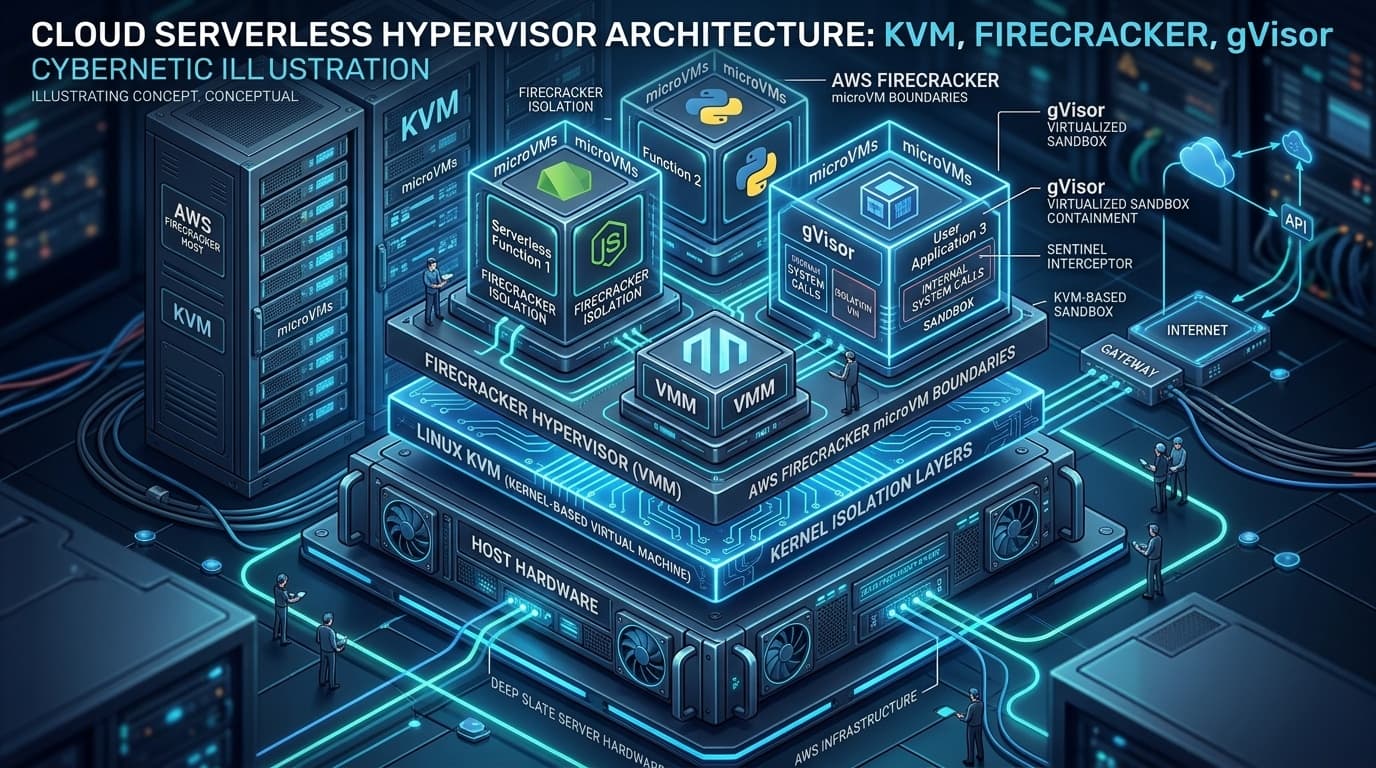
AWS CloudAn architectural research study comparing AWS Firecracker and Google gVisor, analyzing hypervisor boundaries, KVM virtio mechanics, and container breakout vectors.
Gov / DefenseA technical compliance guide for Indian enterprises implementing automated SIEM/SOAR playbooks to meet CERT-In and RBI 6-hour mandatory breach disclosure deadlines.
GoogleGoogle Cloud Security Bulletin GCP-2026-068 details a gVisor sandboxing namespace defect in Cloud Run worker nodes permitting local privilege escalation.
AWS CloudAWS resolves a critical SSRF vulnerability in amazon-ssm-agent where port forwarding denylist bypasses permit link-local IMDS temporary credential exfiltration.
AWS CloudAWS Security Bulletin details an environment leakage defect in Amazon Bedrock Agent action group runtimes permitting cross-session IAM credential exposure.
Data BreachThe operationalization of the Data Protection Board of India (DPBI) brings mandatory breach notifications and statutory penalties up to ₹250 Crore into active enforcement.
MicrosoftMicrosoft MSRC bulletin details an untrusted search path vulnerability in Azure Monitor Agent Metrics Extension allowing low-privileged users to attain SYSTEM privileges.
GoogleGoogle Cloud Bulletin GCP-2026-057 warns of an Envoy Proxy safe_regex parsing flaw in Cloud Service Mesh causing negative RBAC authorization policies to fail open.
MicrosoftA critical vulnerability in Microsoft Entra ID allows authenticated users to manipulate assumed-immutable directory attributes and achieve Global Admin rights.