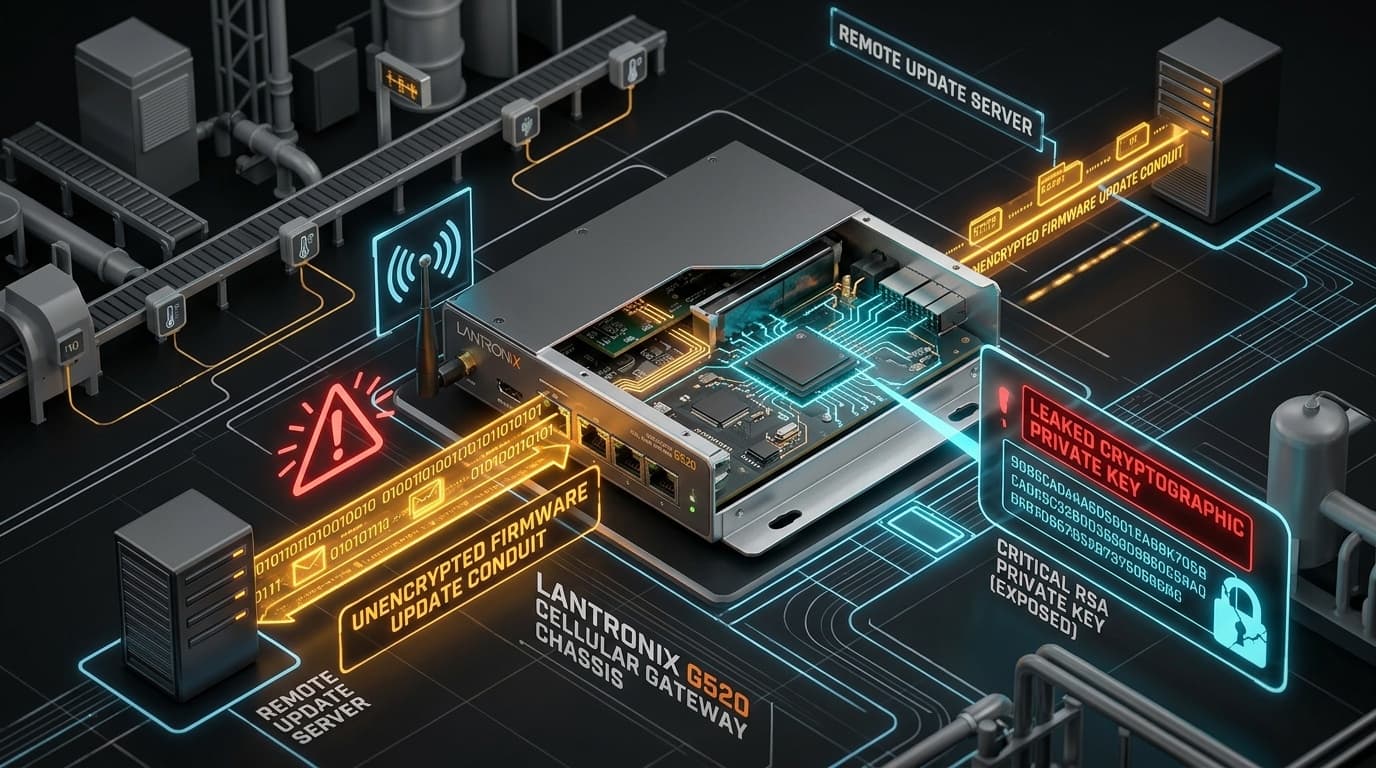
The Cybersecurity and Infrastructure Security Agency (CISA) has published advisory ICSA-26-272-01 warning critical infrastructure organizations of two high-severity vulnerabilities (CVE-2026-84409 and CVE-2026-91191, CVSS 8.8) affecting Lantronix G520 Series industrial cellular gateways. The devices, widely utilized across municipal water utilities, traffic signal systems, and electric distribution substations to provide remote 4G/5G WAN routing, are vulnerable to arbitrary firmware forgery and complete root operating system compromise.
The Dangerous Dual Flaw: Unencrypted Transport & Leaked Signing Keys
The security compromise involves two compounding engineering errors:
- Unencrypted Update Mechanism (CVE-2026-84409, CWE-319): The router's automatic update client checks for new firmware releases by issuing unencrypted HTTP requests to vendor servers. An adversary on the local ISP or cellular backhaul network can intercept and spoof this connection.
- Exposed Production RSA Private Key (CVE-2026-91191, CWE-798): To prevent unauthorized firmware installation, the gateway verifies that binary images are signed by Lantronix. However, security researchers discovered that the official software development kit (SDK) distributed to system integrators contained the company's production private cryptographic signing key embedded in plaintext.
Attack Mechanics: Weaponized Firmware Injection
Because the production private key was exposed, an attacker can construct a malicious embedded Linux image, embed a persistent backdoor (such as an SSH reverse shell), and sign the payload with the legitimate vendor key:
# Cryptographic signature generation using leaked private key
openssl dgst -sha256 -sign lantronix_prod_private.pem   -out malicious_firmware.bin.sig   malicious_firmware.bin
When the G520 router checks for updates over cellular links, the attacker intercepts the HTTP traffic, supplies the forged firmware, and passes cryptographic signature checks. The gateway flashes the malicious image into non-volatile NAND flash, granting root shell persistence that survives reboots.
Recommended Hardening Measures for Utility Operators
- Deploy Firmware v2.6.0.7R6: Immediately flash all deployed Lantronix G520 gateways with the remediated firmware release, which revokes the leaked signing certificate and enforces HTTPS transport.
- Disable Remote Management over Cellular WAN: Ensure that web administrative interfaces and SSH services are accessible only via encrypted IPsec or OpenVPN tunnels, never directly exposed to public cellular carrier IP ranges.
- Segment Field Gateway Traffic: Isolate cellular telemetry modems on isolated VLANs with strict outbound egress filtering to prevent lateral movement into utility SCADA masters.