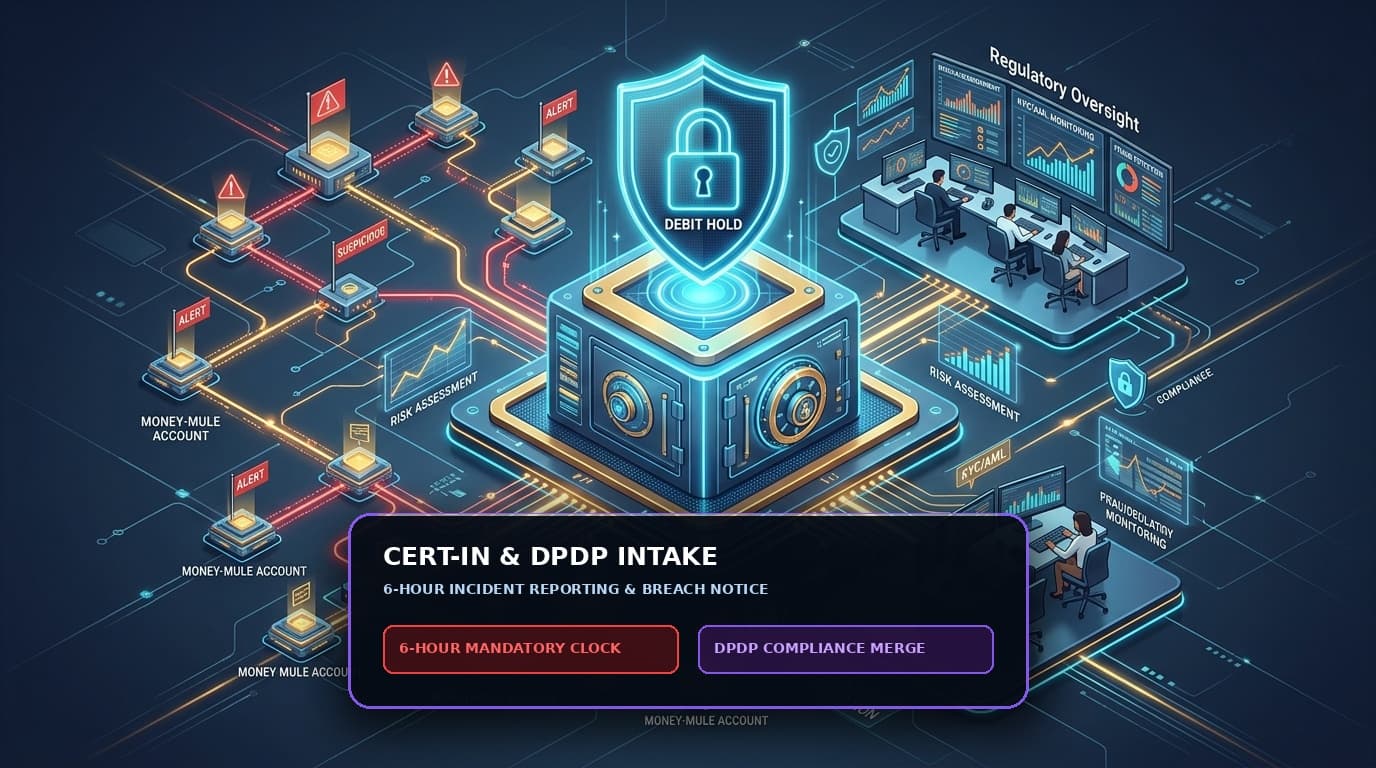
The Indian Computer Emergency Response Team (CERT-In) and the Reserve Bank of India (RBI) have operationalized an aggressive, unified regulatory compliance standard mandating that all critical sector organizations—including scheduled commercial banks, non-bank payment operators, cloud service providers, and telecom intermediaries—report confirmed cybersecurity breaches within 6 hours of detection.
The 6-Hour Reporting Window: Regulatory Architecture
Under the cyber security directions issued pursuant to Section 70B(6) of the Information Technology Act, 2000, organizations must submit incident details to CERT-In using the standardized incident reporting format. For financial entities, an identical notice must simultaneously be transmitted to the RBI's Cyber Security and IT Risk (CSITE) Cell.
The 6-hour clock commences from the moment an incident is first observed by automated monitoring telemetry or reported to the internal Security Operations Center (SOC), regardless of whether root-cause forensic investigations are complete.
Automated SOAR Regulatory Notification Playbook
Attempting to meet a 6-hour SLA through manual document preparation routinely results in regulatory reporting violations. Modern security teams must operationalize automated orchestration playbooks that generate preliminary incident disclosures:
# Python SOAR Playbook: CERT-In & RBI Automated Incident Dossier Generator
import json
import datetime

def generate_certin_notification(incident_event):
    payload = {
        "reporting_entity": "National Financial Services Pvt Ltd",
        "incident_timestamp_ist": datetime.datetime.now().strftime("%Y-%m-%d %H:%M:%S"),
        "incident_type": incident_event.get("classification"),
        "affected_systems": incident_event.get("impacted_hosts_count"),
        "indicators_of_compromise": incident_event.get("extracted_iocs", []),
        "mitigation_actions_taken": [
            "Affected VLAN isolated via 802.1X quarantine",
            "Compromised Kerberos golden tickets invalidated",
            "Outbound C2 egress IPs blocked at perimeter firewall"
        ],
        "ciso_declaration": "Preliminary notification submitted within 6-hour SLA"
    }
    return json.dumps(payload, indent=2)
Key Incident Categories Covered under Mandatory Scope
| Mandatory Reporting Category | Reporting SLA | Primary Regulatory Authority |
|---|---|---|
| Targeted Intrusion / Ransomware | Strict 6 Hours | CERT-In & RBI CSITE |
| Unauthorized Access to Customer PII / Financial Data | Strict 6 Hours | CERT-In, RBI & DPBI |
| Identity Infrastructure Compromise (AD / Okta / Entra) | Strict 6 Hours | CERT-In & RBI |
| Critical Third-Party Cloud Service Outage | Strict 6 Hours | CERT-In & RBI |
Enterprise Governance Action Plan
- Calibrate Severity-1 SOC Playbooks: Ensure internal incident classification procedures define any customer-facing compromise or ransomware detection as an automatic regulatory trigger.
- Maintain Immutable Log Archives: Synchronize NTP clocks across all network appliances with the National Physical Laboratory (NPL) or CERT-In time servers, retaining audit logs for a rolling 180-day window.
- Conduct Biannual Regulatory Drills: Simulate table-top cyber incident scenarios testing the cross-functional coordination between SOC analysts, legal counsel, and executive management under 6-hour time pressure.