Topic
CWE-287: news, advisories and analysis
20 articles
CyberSecureToday covers CWE-287 across 20 articles published between 17 Sep 2026 and 17 Oct 2026. The coverage includes 16 vulnerability advisories, 2 incident or breach reports and 1 analysis or guidance piece. 16 advisories are rated critical or high severity, and 3 involve flaws listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on CWE-287 most often intersect with Authentication Bypass, Cloud Security and Remote Code Execution, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Mage OSS Critical Authentication Bypass Flaw CVE-2026-111823 Exposes Enterprise ETL Data Pipelines to Remote Takeover”, was published 17 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsCloud & SaaSCriticalCST Editorial Desk
ThreatsCloud & SaaSHighGoogle Cloud Workload Identity Federation OIDC Token Bypass Flaw CVE-2026-19410 Remediated
Aisha Noor
ThreatsCloud & SaaSCriticalIvanti Connect Secure SAML Bypass Opens Gateways to Pre-Auth Code Execution
Mei-Lin Chen
ThreatsCloud & SaaSHighAzure Arc Connected Machine Agent Local Privilege Escalation Flaw CVE-2026-83711 Enables Host Compromise
Aisha Noor
ThreatsCloud & SaaSCriticalAWS IAM Identity Center Flaw Enables SCIM Bearer Token Bypass Across Enterprise Cloud Tenants
CST Editorial Desk
ThreatsIndustrial & OTCriticalRockwell Automation FactoryTalk VantagePoint Critical Authentication Bypass Flaw Disclosed by CISA Advisory ICSA-26-280-01
Mei-Lin Chen
NewsIndustrial & OTWater Utility Discloses Nation-State Breach of SCADA Gateways in SEC Filing
Daniel Okafor
ThreatsIndustrial & OTCriticalJohnson Controls EasyIO Neo Controllers Authentication Bypass Flaw CVE-2026-40112 Disclosed by CISA
Mei-Lin Chen
ThreatsCloud & SaaSCriticalFleet Device Management API Flaw Allows Host Impersonation and MDM Hijacking
CST Editorial Desk
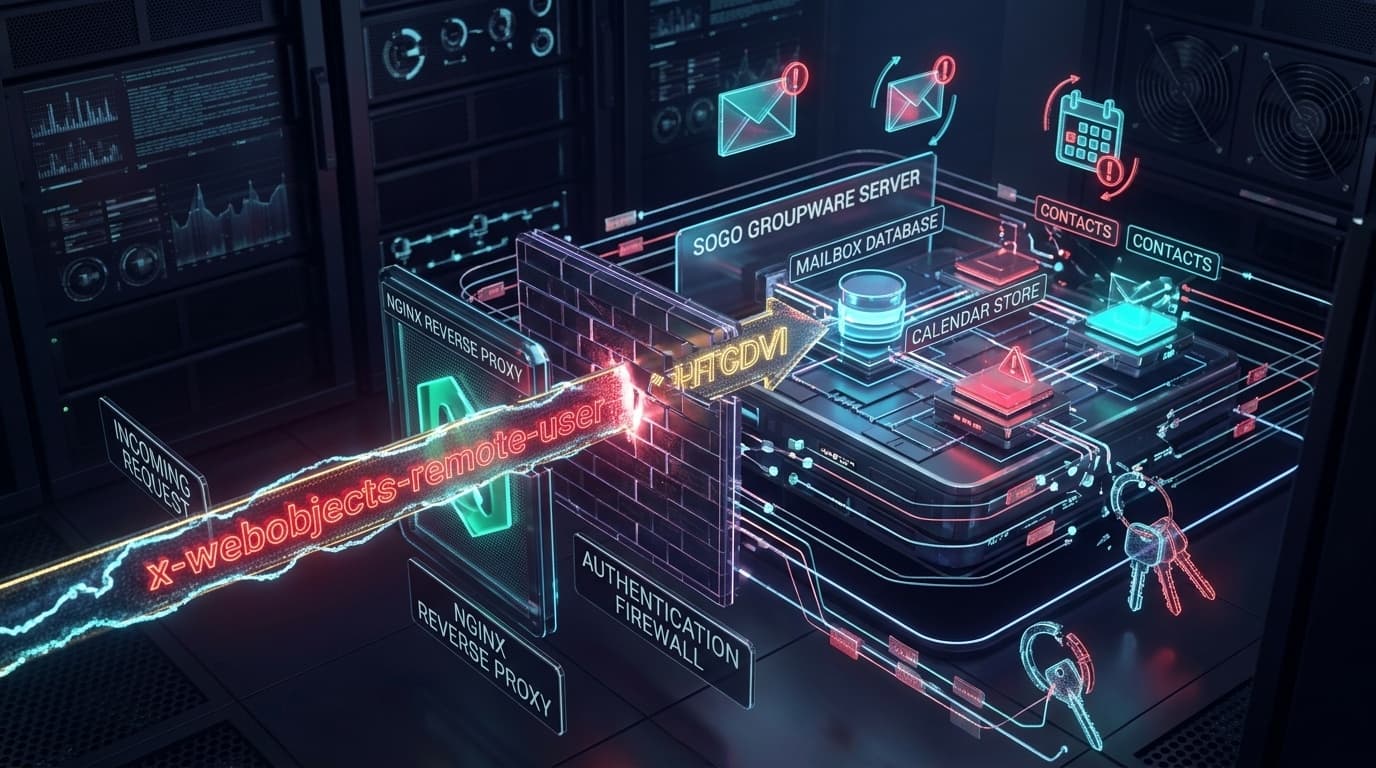
Cyber AttackCloud & SaaSSOGo Groupware Proxy Authentication Flaw Allows Unauthenticated Account Impersonation via WebObjects Header (CVE-2026-74864)
CST Editorial Desk
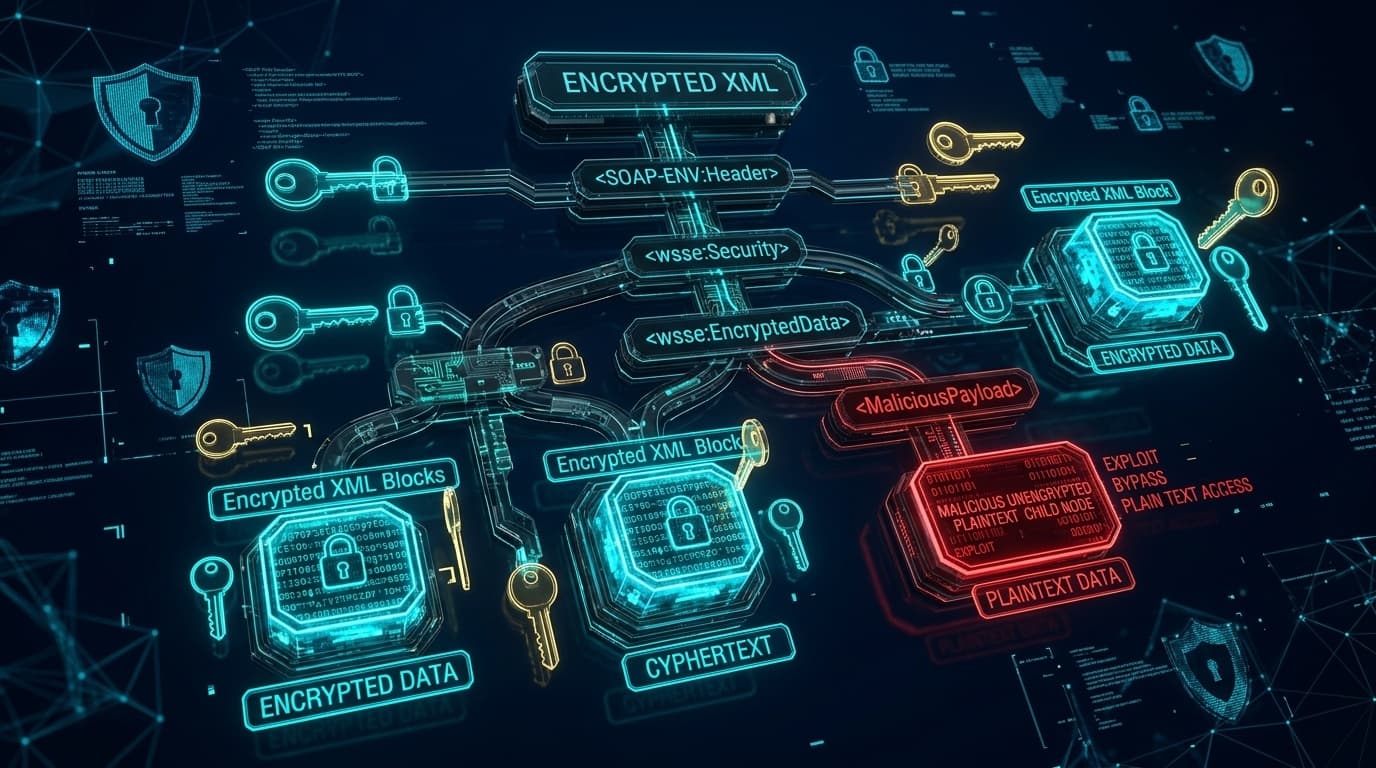
ThreatsBanking & FintechCriticalApache WSS4J EncryptedHeader Child Confusion Allows Cryptographic Signature and Policy Bypass (CVE-2026-89238)
Priya Raman
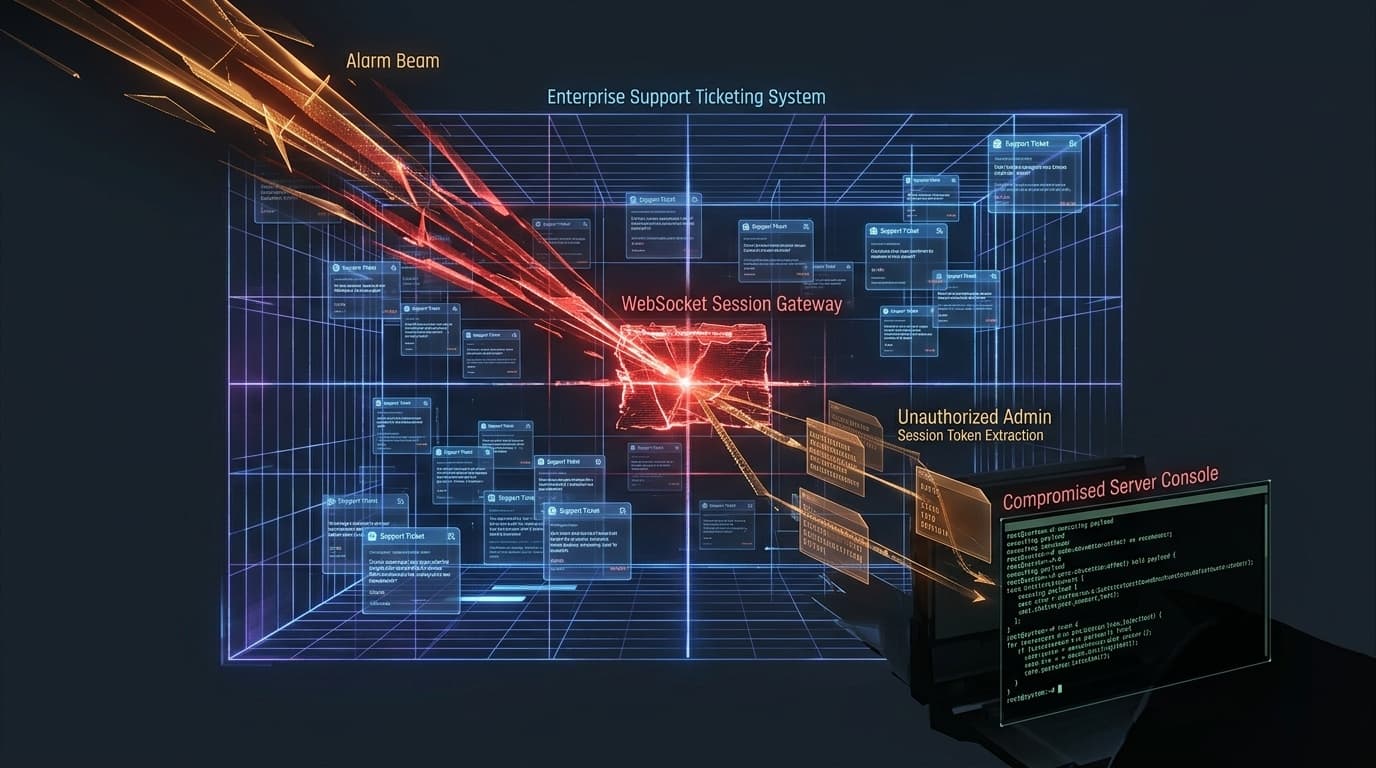
ThreatsCloud & SaaSCriticalZammad Enterprise Helpdesk Session Hijacking Vulnerability Leads to Unauthenticated Remote Code Execution (CVE-2026-102489)
Priya Raman
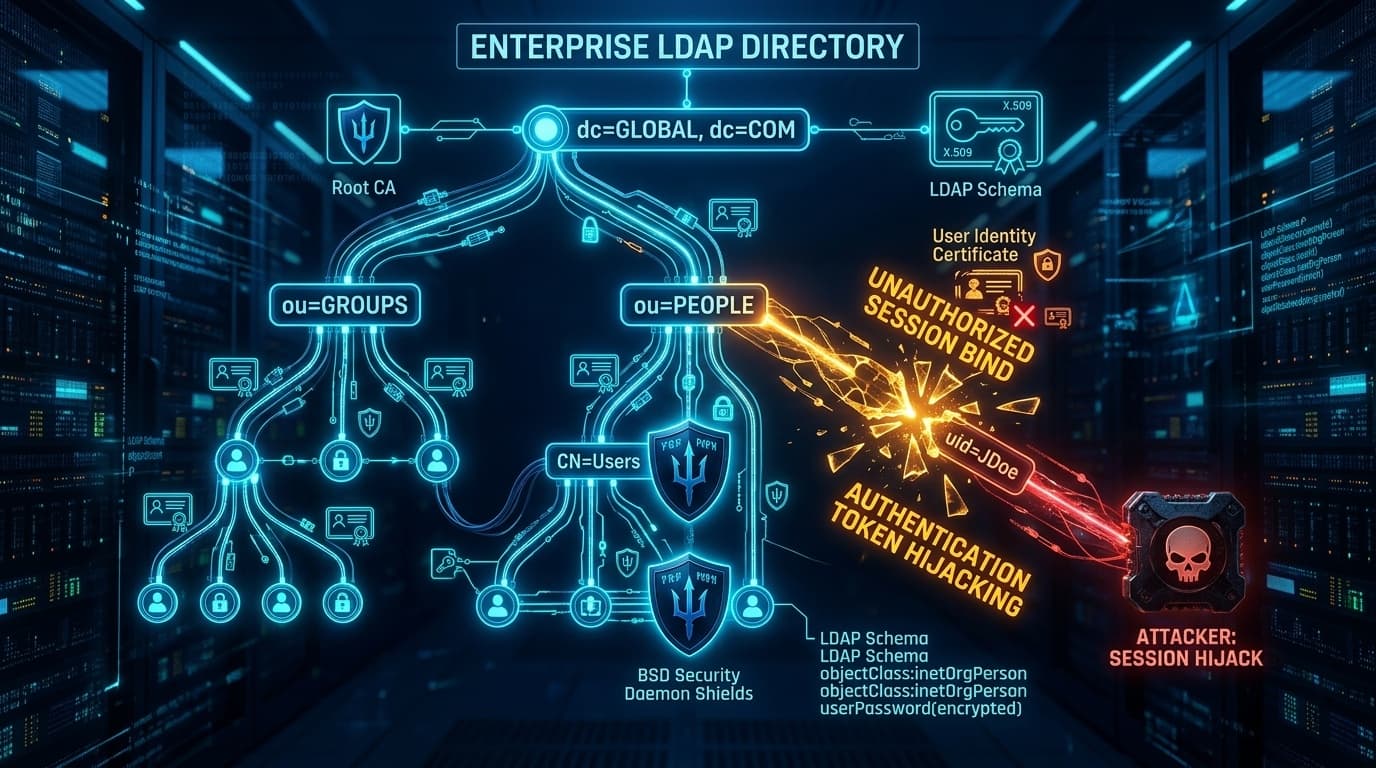
ThreatsCloud & SaaSCriticalOpenBSD ldapd Asynchronous Response Race Allows Unauthorized Directory Session Hijacking (CVE-2026-103547)
CST Editorial Desk
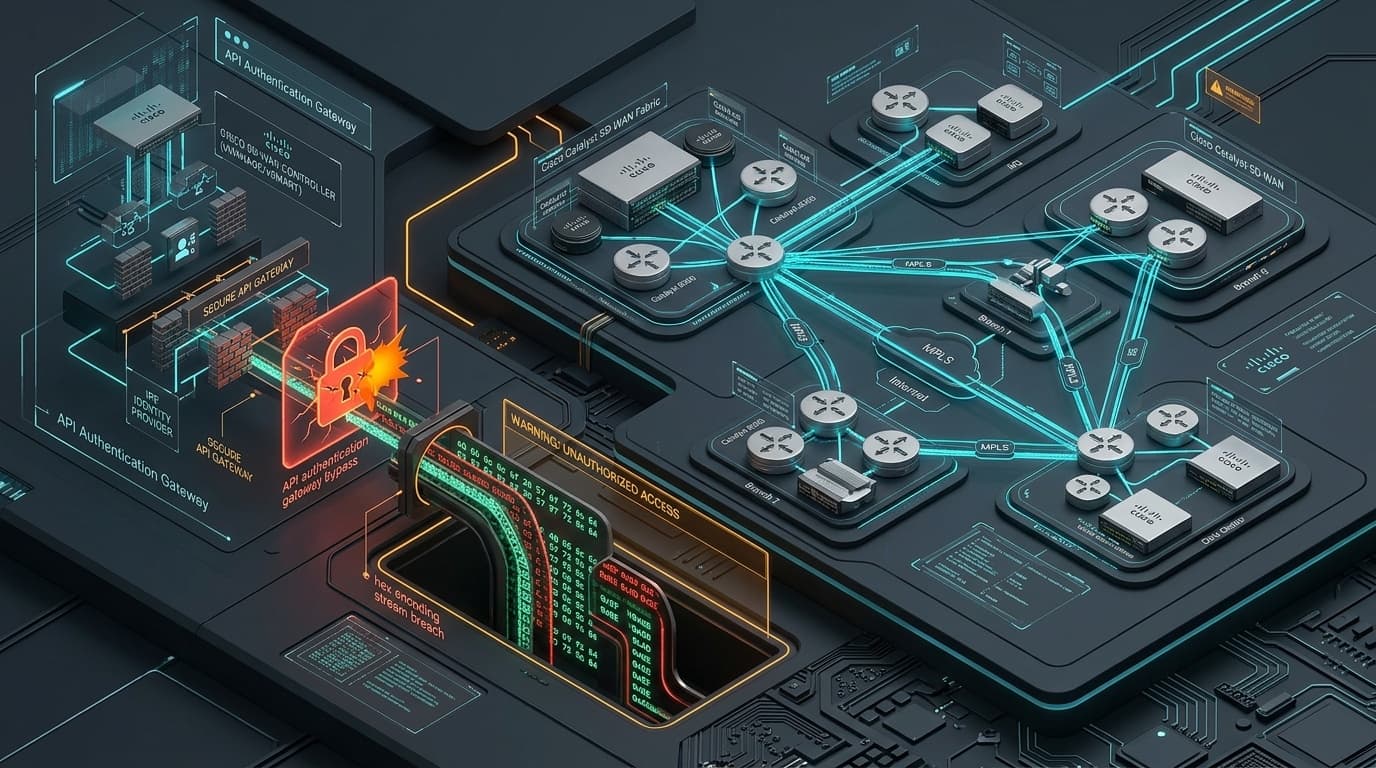
ThreatsCloud & SaaSCriticalCisco Catalyst SD-WAN Manager Hex Encoding Flaw Exploited to Hijack Enterprise Routing (CVE-2026-76504)
CST Editorial Desk
Cyber AttackBanking & FintechBitcoin Depot Discloses SEC Form 8-K Material Incident Following $3.6M Cryptocurrency Wallet Breach
Daniel Okafor
ThreatsIndustrial & OTCriticalSiemens SIMOVE Fleetmanager Flaws Enable Remote Trajectory Hijacking of Factory AGVs
CST Editorial Desk
ThreatsCloud & SaaSCriticalHPE Aruba EdgeConnect SD-WAN Orchestrator Authentication Bypass Flaw Enables Remote Network Gateway Hijack
Aisha Noor
InsightsCloud & SaaSModel Context Protocol OAuth Passthrough Flaw Exposes Autonomous AI Tool Pipelines to Silent Impersonation
Priya Raman
ThreatsCloud & SaaSCriticalHacktron Uses Claude Opus 5 to Beat libheif ASLR, Infiltrate OpenAI Perimeter
CST Editorial Desk
ThreatsCloud & SaaSCriticalSimpleHelp Remote Support Platform Critical Authentication Bypass CVE-2026-48558 in Active Attacks
Daniel Okafor