A critical cryptographic policy bypass vulnerability has been disclosed in Apache WSS4J (Web Services Security for Java), the foundational security engine implemented across enterprise Java web services, Apache CXF, and financial messaging gateways. Tracked under CVE-2026-89238 and GitHub Security Advisory GHSA-wm7f-562f-9g52, the vulnerability allows remote attackers to bypass WS-Security confidentiality and integrity enforcement policies by exploiting element child confusion during the processing of SOAP EncryptedHeader structures.
WS-Security and XML Encryption in Enterprise Banking
In banking, inter-bank clearance networks (such as ISO 20022 and Fedwire messaging) and enterprise service buses (ESBs), SOAP endpoints require cryptographic protection governed by OASIS WS-Security specifications. Sensitive transaction headers (including account numbers, digital signature tokens, and role-based authorization credentials) are encapsulated within <wsse11:EncryptedHeader> elements to guarantee end-to-end confidentiality across untrusted proxy hops.
Vulnerability Mechanics: Child Confusion in EncryptedHeader Processing (CWE-287)
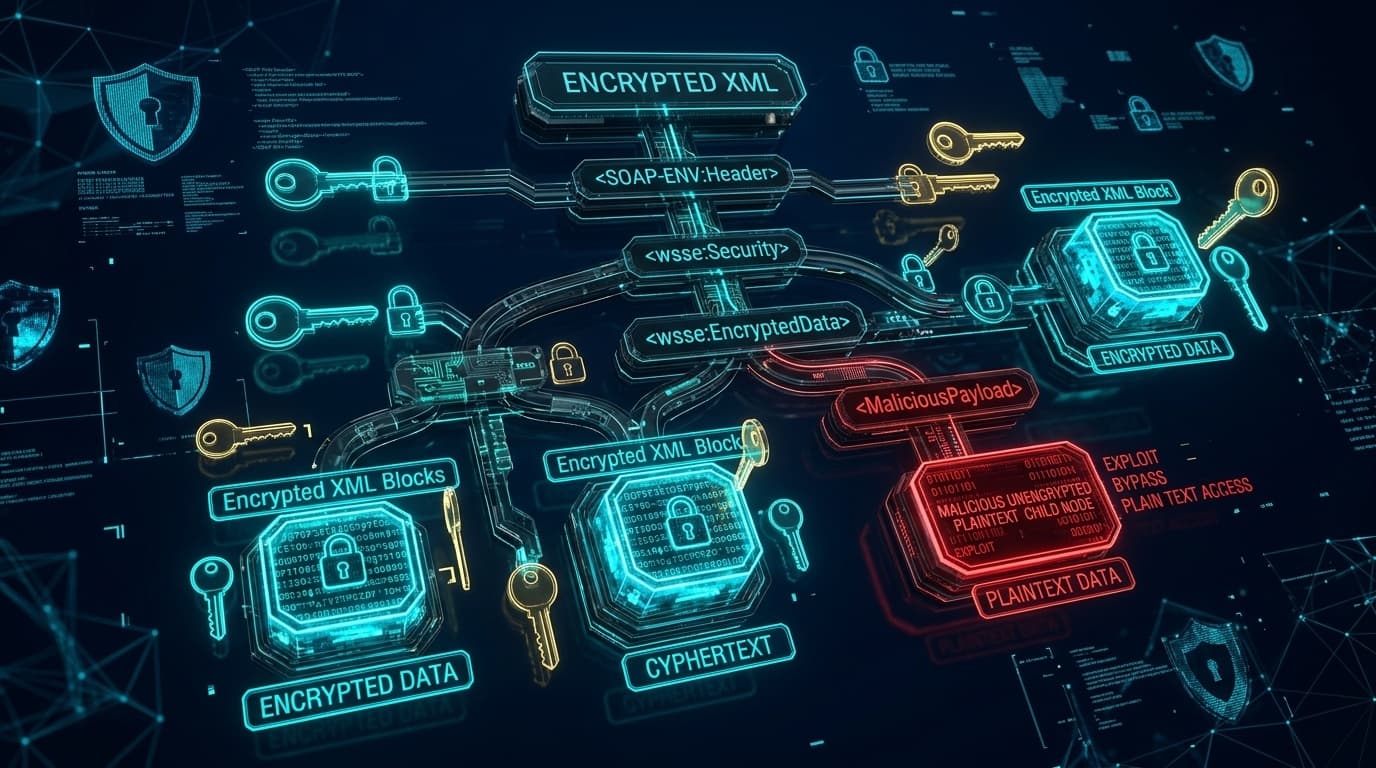
When a SOAP envelope containing an EncryptedHeader is received, Apache WSS4J is responsible for locating the xenc:EncryptedData block, decrypting the payload using the server's private key or session key, and replacing the header wrapper with the resulting decrypted DOM element.
In vulnerable versions, the header processing algorithm searches child nodes loosely without validating that the child being processed is exclusively the legitimate decrypted XML fragment:
<!-- Malicious SOAP Request Structure -->
<soap:Header>
  <wsse11:EncryptedHeader xmlns:wsse11="http://docs.oasis-open.org/wss/oasis-wss-wssecurity-secext-1.1.xsd">
    <!-- Attacker-Controlled Unencrypted Plaintext Element -->
    <auth:RoleToken xmlns:auth="http://banking.internal/auth">
      <auth:Role>GlobalSuperAdmin</auth:Role>
    </auth:RoleToken>
    <!-- Legitimate or Dummy EncryptedData Element -->
    <xenc:EncryptedData xmlns:xenc="http://www.w3.org/2001/04/xmlenc#">
      ...
    </xenc:EncryptedData>
  </wsse11:EncryptedHeader>
</soap:Header>
Due to the child confusion bug, WSS4J prematurely promotes the unencrypted child element (<auth:RoleToken>) as the valid decrypted output of the EncryptedHeader. The backend application logic accepts the attacker's unencrypted payload as authenticated and authorized, while the WS-Security policy engine erroneously records that the mandatory encryption requirement was satisfied.
Cryptographic Assurance Matrix
| Security Attribute | Vulnerable WSS4J Parsing | Remediated Parsing (2.4.4 / 3.0.6 / 4.0.2) |
|---|---|---|
| EncryptedHeader Validation | Accepts heterogeneous child nodes within header wrapper | Strict schema enforcement: exactly one xenc:EncryptedData allowed |
| Confidentiality Policy | Plaintext injected elements falsely satisfy encryption policy | Only cryptographically decrypted DOM elements can satisfy policy |
| Banking Payload Integrity | Adversaries can forge transaction authorizations | All unencrypted header injections rejected with SOAP Fault |
Remediation & Defense Actions
- Upgrade Apache WSS4J: Update Maven/Gradle dependencies to patched releases immediately:
- For 2.4.x branches: Upgrade to 2.4.4
- For 3.0.x branches: Upgrade to 3.0.6
- For 4.0.x branches: Upgrade to 4.0.2
- Update Dependent Middleware: If utilizing Apache CXF, ensure the CXF runtime is updated to releases incorporating the patched WSS4J libraries.
- Enable Strict XML Schema Validation: Configure XML parser security flags to reject non-conforming SOAP envelopes at the gateway level before cryptographic processing is triggered.