Threat IntelApache HTTP Server patches critical HTTP/2 remote code execution flaw
Critical vulnerability in Apache Core System & Services (Missing Authentication) allows remote adversaries to compromise system integrity. Review analysis
Topic
11 articles
CyberSecureToday covers Apache across 11 articles published between 1 Oct 2026 and 13 Nov 2026.
The coverage includes 10 vulnerability advisories and 1 incident or breach report. 10 advisories are rated critical or high severity.
Stories on Apache most often intersect with Vulnerability Analysis, Patch & Fix and Security Advisory, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Apache HTTP Server patches critical HTTP/2 remote code execution flaw”, was published 13 Nov 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Threat IntelCritical vulnerability in Apache Core System & Services (Missing Authentication) allows remote adversaries to compromise system integrity. Review analysis
Threat IntelCVE-2026-119618 in Apache Core System & Services (Security Vulnerability) allows remote attackers to trigger arbitrary code execution. Patch: Version 2.4.7
Crypto / Web3Forensic analysis of the security incident impacting Apache: smart contract mechanics, fund flows, and defensive hardening.
Threat IntelCVE-2026-73116 in Apache Insufficiently Protected Credentials vulnerability (Input Validation) allows remote attackers to trigger arbitrary code execution.
Threat IntelCVE-2026-83542 in Apache Improper Control of Generation of Code ('Code Inje (Code Injection) allows remote attackers to trigger arbitrary code execution. P
Threat IntelCVE-2026-73098 in Apache Improper control of dynamically-loaded code vulner (Input Validation) allows remote attackers to trigger arbitrary code execution.
Threat IntelCVE-2026-73099 in Apache Cross-Site Request Forgery (CSRF) vulnerability in (Cross-Site Request Forgery) allows remote attackers to trigger arbitrary code
Threat IntelCVE-2026-111811 in Apache Traffic Server's experimental tsmemcache pl (Missing Authentication) allows remote attackers to trigger arbitrary code execution.
Threat IntelCVE-2026-111816 in Apache Traffic Server forwarded a malformed 302 re (Security Vulnerability) allows remote attackers to trigger arbitrary code execution.
Threat IntelCVE-2026-78162 in Apache Deserialization of Untrusted Data vulnerability in (Deserialization) allows remote attackers to trigger arbitrary code execution.
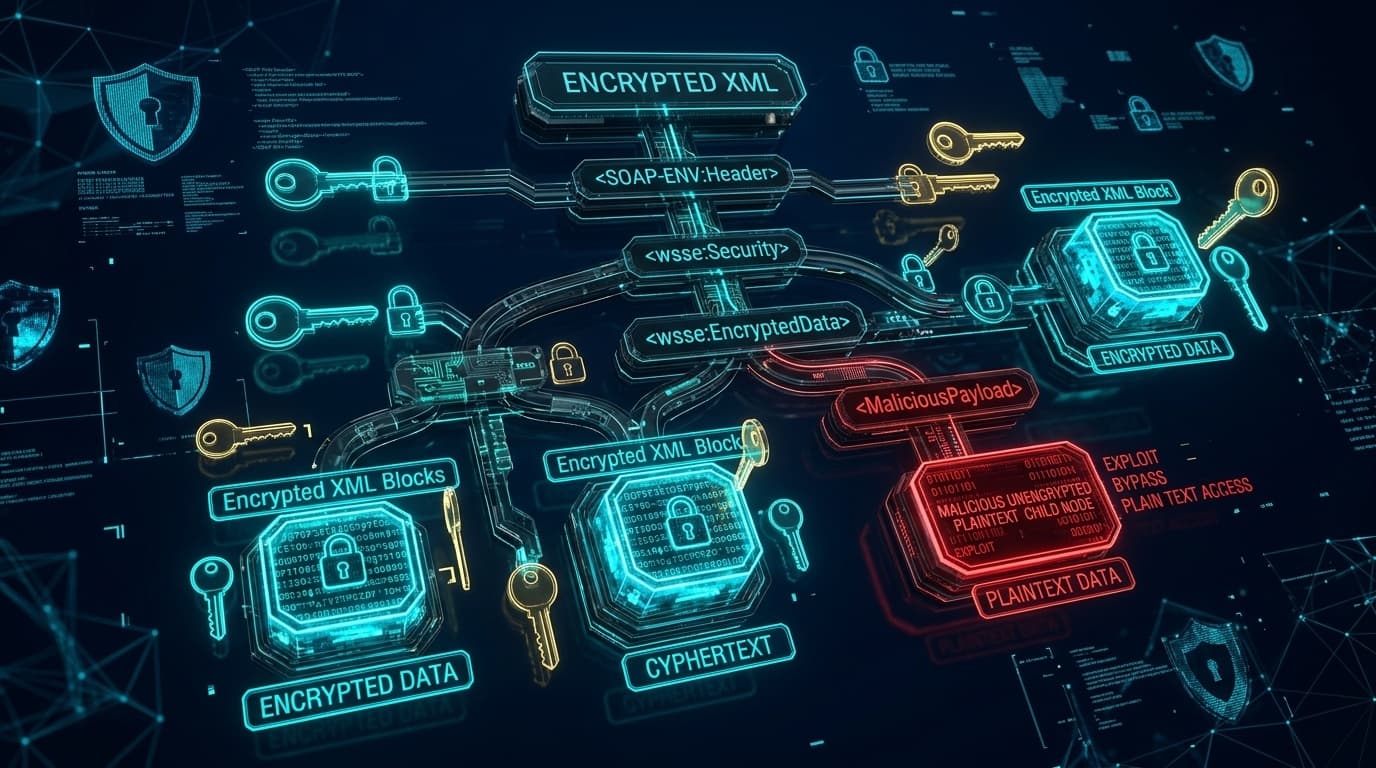
Threat IntelAn element confusion flaw in Apache WSS4J allows attackers to substitute encrypted headers with unencrypted plaintext, bypassing WS-Security confidentiality policies.