 Threat Intel
Apache WSS4J EncryptedHeader Child Confusion Allows Cryptographic Signature and Policy Bypass (CVE-2026-89238)
ThreatsBanking & FintechCVE-2026-89238Critical
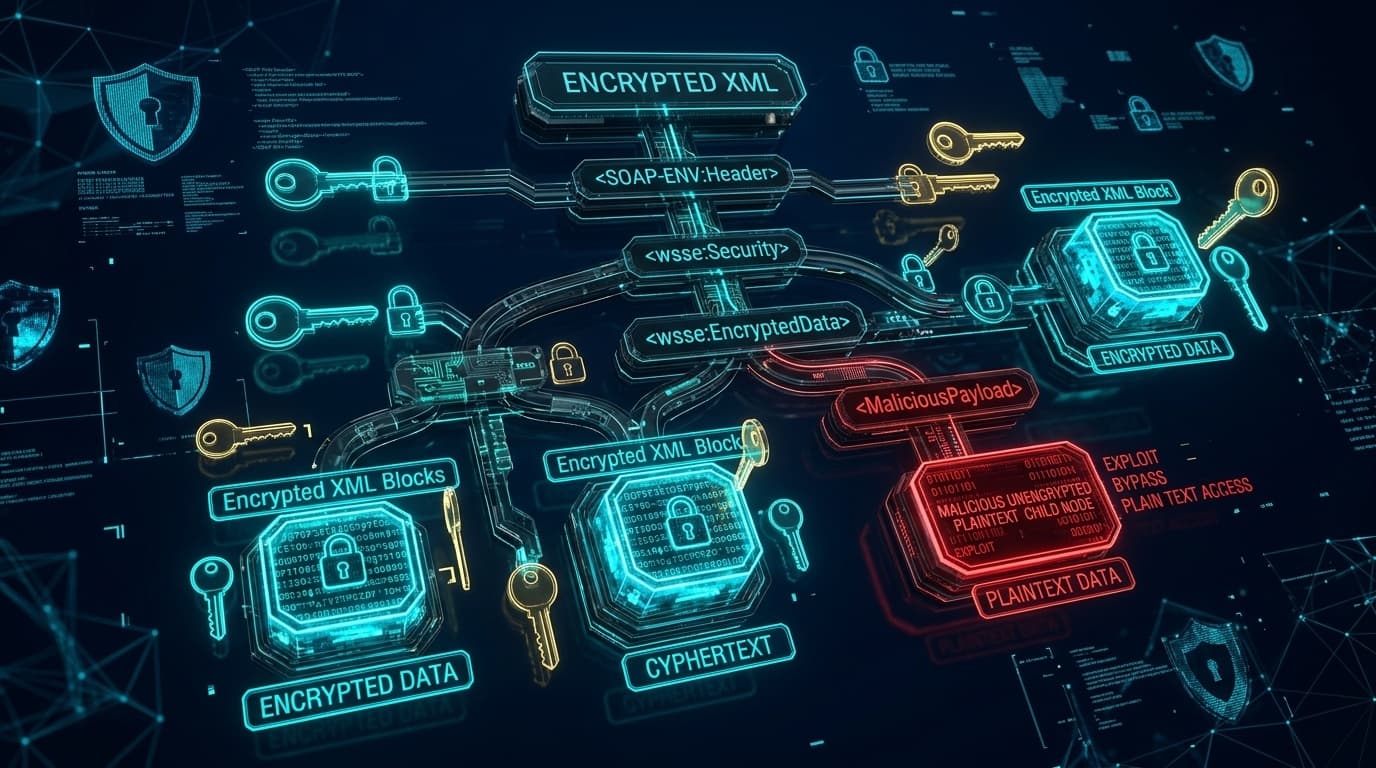
An element confusion flaw in Apache WSS4J allows attackers to substitute encrypted headers with unencrypted plaintext, bypassing WS-Security confidentiality policies.
Priya Raman11 min read