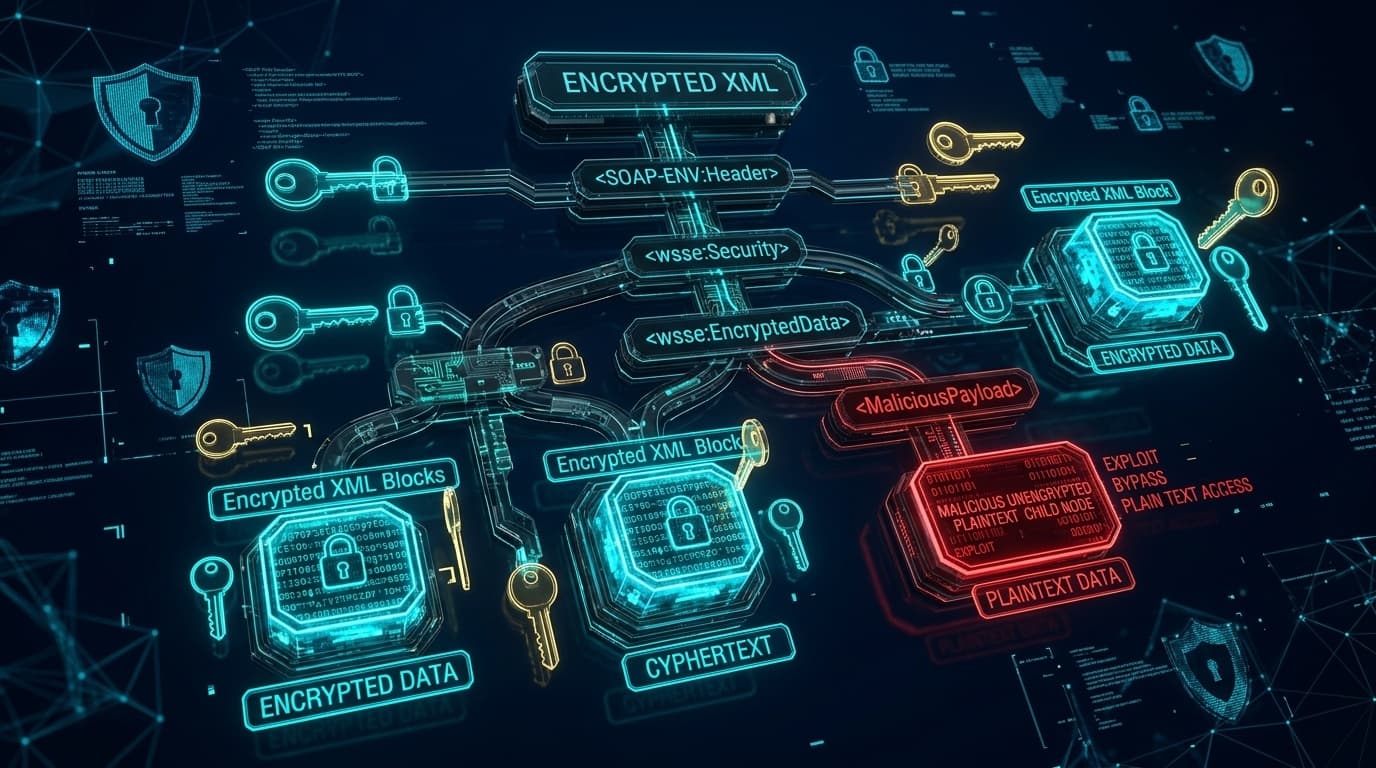
Threats·Banking & FintechBreakingApache WSS4J EncryptedHeader Child Confusion Allows Cryptographic Signature and Policy Bypass (CVE-2026-89238)An element confusion flaw in Apache WSS4J allows attackers to substitute encrypted headers with unencrypted plaintext, bypassing WS-Security confidentiality policies.Priya Raman1 Oct 202611 min read