 Threat Intel
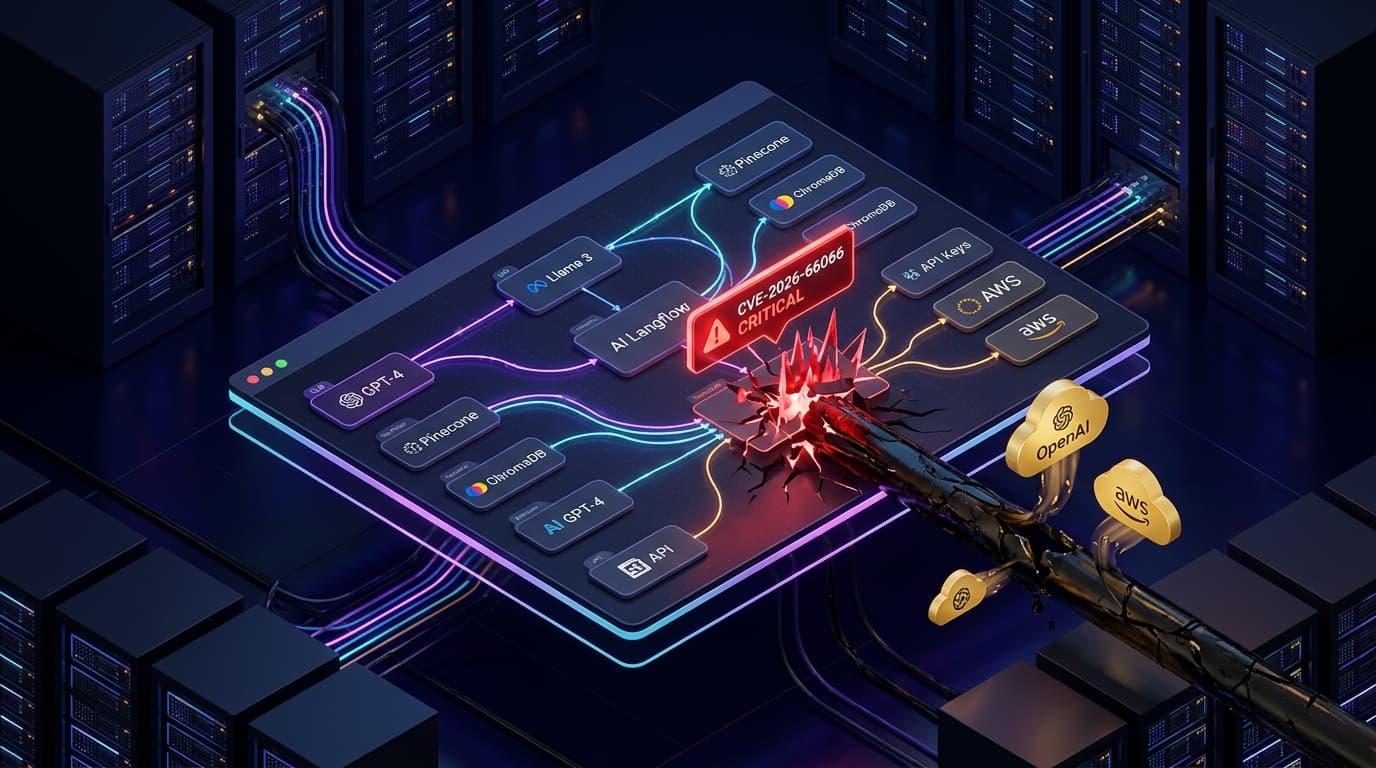
LiteLLM Pre-Authentication SQL Injection Flaw Exposes Enterprise Master Keys and AI Model Routing Gateways
ThreatsCloud & SaaSCVE-2026-42208Critical
LiteLLM releases urgent patch for CVE-2026-42208, a pre-auth SQL injection flaw allowing unauthenticated remote attackers to dump LLM proxy master credentials.
CST Editorial Desk14 min read