AWS CloudAWS Lambda MicroVM Isolation Flaw Exposed STS Session Keys Across Invocations
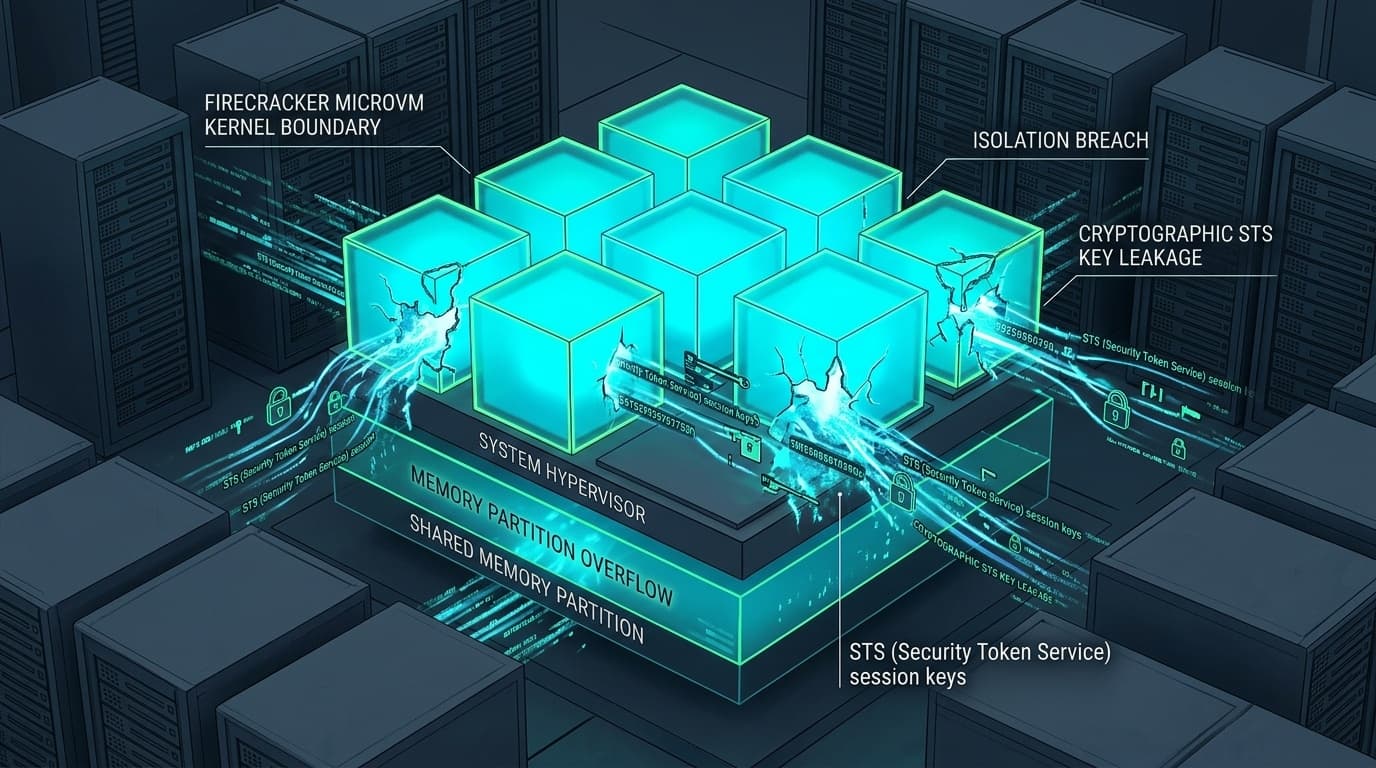
AWS issues advisory CVE-2026-71215 for Lambda Custom Runtimes, addressing a Firecracker microVM memory reclamation flaw that exposed ephemeral STS tokens.
Topic
2 articles
CyberSecureToday covers Firecracker across 2 articles published between 6 Oct 2026 and 11 Oct 2026.
The coverage includes 1 vulnerability advisory and 1 analysis or guidance piece. 1 advisory is rated critical or high severity.
Stories on Firecracker most often intersect with MicroVM, AWS Lambda and Serverless, with Technology, Cloud & SaaS the most affected sector. The most recent story, “AWS Lambda MicroVM Isolation Flaw Exposed STS Session Keys Across Invocations”, was published 11 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
AWS CloudAWS issues advisory CVE-2026-71215 for Lambda Custom Runtimes, addressing a Firecracker microVM memory reclamation flaw that exposed ephemeral STS tokens.
Agentic AIRecent CVEs in Ollama and AWS MCP reveal that semantic prompt filters cannot prevent tool injection. Engineering teams must isolate agent tools in ephemeral microVMs.