AWS CloudAWS Lambda MicroVM Isolation Flaw Exposed STS Session Keys Across Invocations
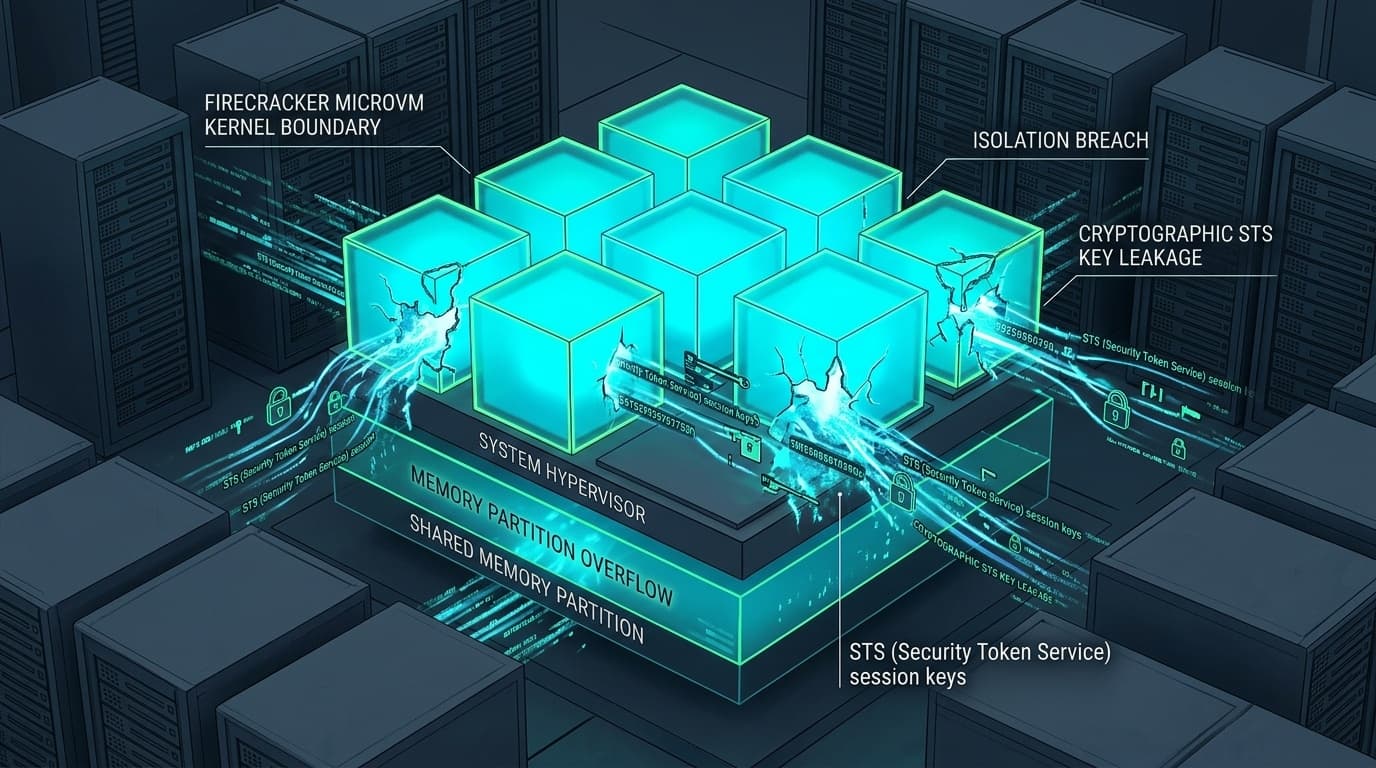
AWS issues advisory CVE-2026-71215 for Lambda Custom Runtimes, addressing a Firecracker microVM memory reclamation flaw that exposed ephemeral STS tokens.
Topic
3 articles
CyberSecureToday covers AWS Lambda across 3 articles published between 26 Sep 2026 and 11 Oct 2026.
The coverage includes 3 vulnerability advisories. 2 advisories are rated critical or high severity.
Stories on AWS Lambda most often intersect with Cloud Security, Privilege Escalation and AWS, with Technology, Cloud & SaaS the most affected sector. The most recent story, “AWS Lambda MicroVM Isolation Flaw Exposed STS Session Keys Across Invocations”, was published 11 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
AWS CloudAWS issues advisory CVE-2026-71215 for Lambda Custom Runtimes, addressing a Firecracker microVM memory reclamation flaw that exposed ephemeral STS tokens.
AWS CloudAWS resolved a fail-open defect in Python Lambda Powertools data masking (CVE-2026-104002) that emitted unmasked sensitive records to logs during masking errors.
AWS CloudAWS Security Bulletin 2026-115-AWS warns of a critical authorization flaw in AmazonConnectSalesforceLambda enabling unprivileged IAM users to execute arbitrary AWS APIs.