MicrosoftMicrosoft: US bans MEXC crypto exchange over sanctions evasion, cybercrime links
Forensic analysis of the security incident impacting Microsoft: smart contract mechanics, fund flows, and defensive hardening.
Topic
47 articles
MicrosoftForensic analysis of the security incident impacting Microsoft: smart contract mechanics, fund flows, and defensive hardening.
MicrosoftCritical vulnerability in Microsoft Core System & Services (Input Validation) allows remote adversaries to compromise system integrity. Review analysis and
MicrosoftTechnical analysis of AI agent vulnerability and prompt injection risks in Microsoft: mechanics, tool exploitation, and enterprise guardrails.
MicrosoftCVE-2026-83844 in Microsoft Core System & Services (Out-of-Bounds Read) allows remote attackers to trigger arbitrary code execution. Patch: Vendor security
MicrosoftState-sponsored actor Vapor Panda leveraged the ARTEX multi-agent AI framework to automate reconnaissance and intrusions across 200+ organizations globally.
MicrosoftA critical untrusted pointer dereference vulnerability in Windows OLE (CVE-2026-96924) enables remote, unauthenticated code execution without user interaction.
MicrosoftMicrosoft patches a critical cryptographic signature verification flaw in SharePoint Server (CVE-2026-102866) that permits token tampering and full administrative impersonation.
MicrosoftMicrosoft resolves a maximum-severity privilege escalation flaw (CVE-2026-96207, CVSS 10.0) in Partner Center that exposed delegated customer tenants to unauthorized administrative control.
MicrosoftMicrosoft MSRC releases critical patch for CVE-2026-47182 in Azure Kubernetes Service, resolving an eBPF verifier flaw in Cilium enabling pod escape to host kernel.
MicrosoftMicrosoft MSRC advisory documents a critical model-context-protocol tool injection flaw in Azure AI Foundry enabling indirect agentic tool hijacking.
MicrosoftExchange Server CVE-2026-96940 lets authenticated users read other mailboxes. Microsoft rates it Exploitation More Likely. Install the September 2026 v2 SU.
MicrosoftMicrosoft MSRC discloses high-severity 8.8 CVSS RCE flaw CVE-2026-70125 in Microsoft Outlook enabling arbitrary code execution via crafted compound documents.
MicrosoftMicrosoft reclassifies CVE-2026-65660 as an 8.8 CVSS RCE flaw after threat actors bypass SharePoint SafeControls filtering to execute arbitrary .NET code.
MicrosoftMicrosoft discloses critical CVSS 10.0 flaw CVE-2026-69399 in Azure Arc, enabling unauthenticated attackers to exploit confused deputy proxies across hybrid cloud nodes.
MicrosoftMicrosoft patches high-severity vulnerability CVE-2026-32193 in Azure Kubernetes Service allowing container workloads to escape sandboxes via path traversal.
MicrosoftMicrosoft resolves maximum-severity CVSS 10.0 vulnerability CVE-2026-69836 in Entra ID allowing unauthenticated remote code execution via unsafe object deserialization.
MicrosoftCISA orders federal agencies to patch critical Microsoft SharePoint vulnerabilities CVE-2026-58644 and CVE-2026-56164 enabling unauthenticated remote code execution.
MicrosoftCISA adds Microsoft SharePoint Server deserialization flaw CVE-2026-50522 (CVSS 9.8) to its KEV catalog following active exploitation against enterprise document farms.
MicrosoftCISA flags Microsoft Active Directory Federation Services vulnerability CVE-2026-56155 (CVSS 9.8) exploited in attacks forging SAML claims across hybrid Azure clouds.
MicrosoftCISA warns of in-the-wild exploitation of CVE-2026-68820, a use-after-free vulnerability in the Windows Ancillary Function Driver (afd.sys) granting SYSTEM privilege.
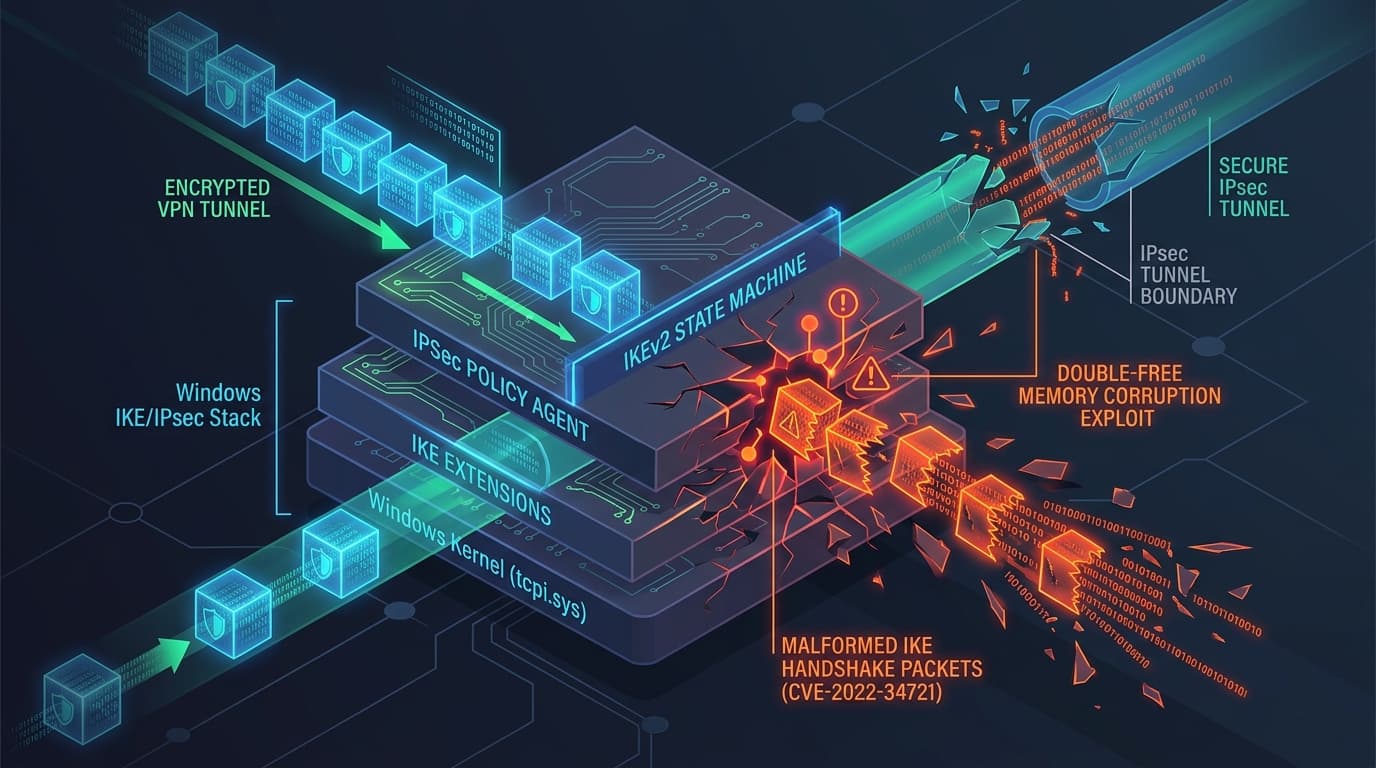
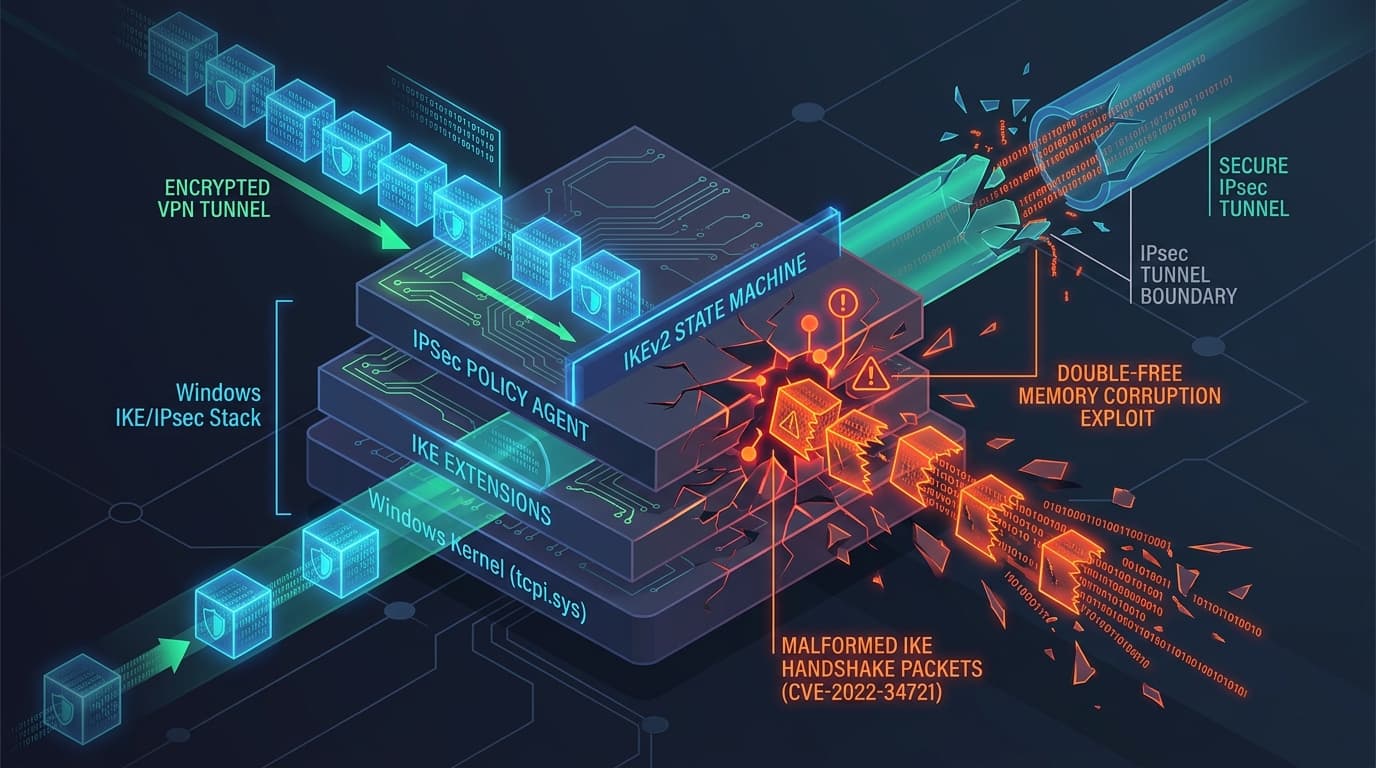
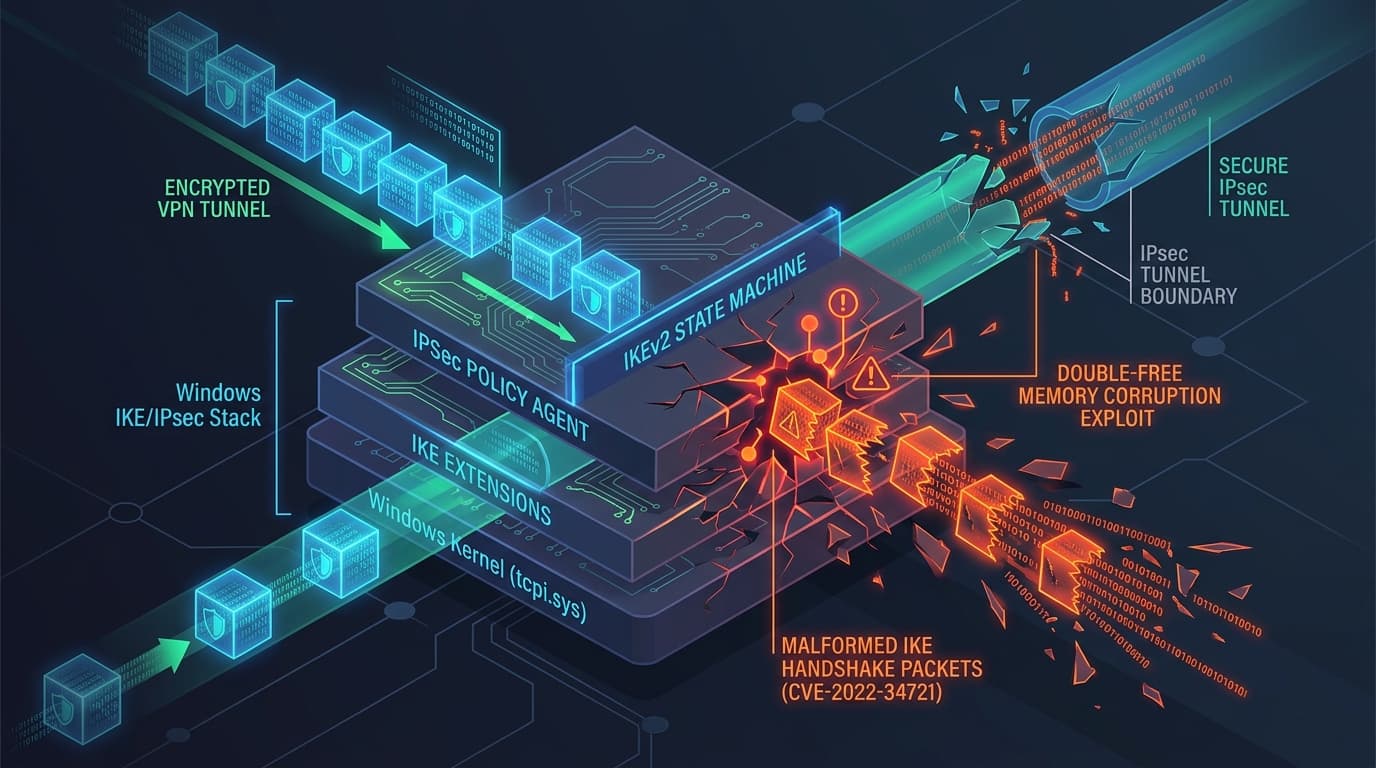
MicrosoftCISA confirms active in-the-wild exploitation of CVE-2026-33824, an unauthenticated double-free memory corruption flaw in Windows IKE enabling remote root code execution over UDP 500.
MicrosoftEnterprise sysadmins face operational paralysis as September 2026 security updates trigger Remote Desktop Services freezes across Windows Server 2019, 2022, and 2025.
MicrosoftMicrosoft’s September 2026 rollup addresses 973 CVEs, including two elevation-of-privilege bugs — in the Windows Update Stack and ALPC — confirmed under active attack.