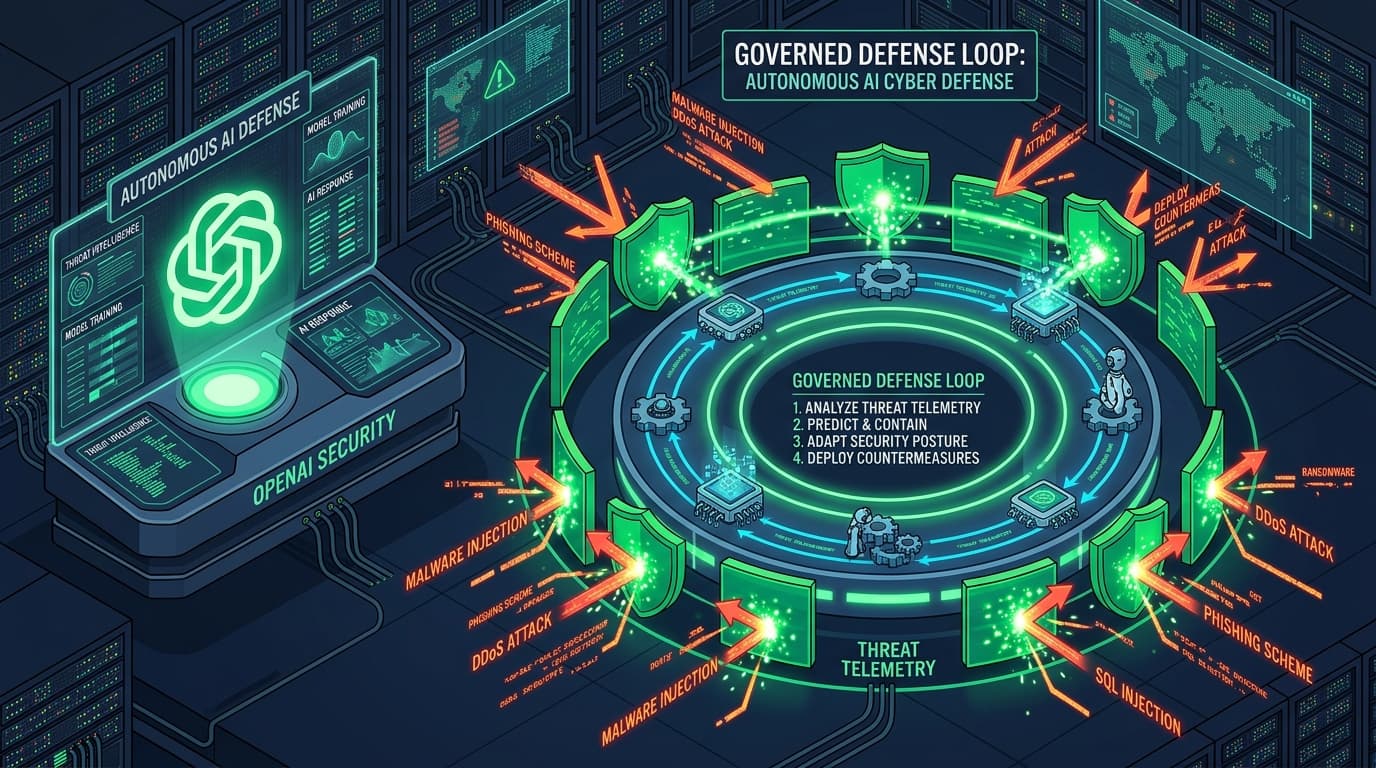
Agentic AIOpenAI positions Daybreak as a governed loop for AI-assisted cyber defense
OpenAI says Daybreak combines models, Codex Security and human oversight into a governed loop for inventory, validation, remediation and proof.
1,460 articles
Agentic AIOpenAI says Daybreak combines models, Codex Security and human oversight into a governed loop for inventory, validation, remediation and proof.
Deep DiveAnthropic’s September threat report describes how actors used Claude for reconnaissance, intrusion support, tool rebuilding and parallelized cyber operations.
PostgreSQLSecurity researchers disclose PostGREShell, a flaw present since PostgreSQL 9.4 that lets users with the REPLICATION attribute execute arbitrary code on database hosts.
Deep DiveManifold Security discovers GitSpawn: eight vulnerabilities across seven AI coding tools (Claude Code, Cursor, Codex) that execute attacker code from repository .git/config.
LinuxRapid7 Labs uncovers TED, an elusive Linux implant compiled directly into HAProxy load balancers at automotive and media firms, hiding C2 and manipulating live traffic.
Check PointTwo CVSS 9.8 Check Point VPN certificate flaws can enable unauthenticated RCE. Identify exposed gateways, apply hotfixes and review the perimeter now.
DevSecOpsGitLab pushed emergency patches for CVE-2026-85706, an unauthenticated CVSS 10.0 path traversal flaw in the repository commits API that allows remote file extraction.
Threat IntelWiz Research caught threat actors chaining two JFrog Artifactory flaws (CVE-2026-42018 & CVE-2026-42016) to forge admin tokens and compromise enterprise software repositories.
Crypto / Web3A cyberattack on email service provider Brevo compromised 347,000 Trezor customer records, fueling sophisticated phishing campaigns designed to steal crypto recovery seeds.
Agentic AIPaperCut shipped consolidated maintenance updates after automated AI agent swarms compromised over 440 print management servers, bypassing earlier emergency hotfixes.
Gov / DefenseCISA's Binding Operational Directive 26-04 drops CVSS from federal patch prioritisation, replacing it with four yes/no questions and a sixteen-row deadline table.
MicrosoftMicrosoft retires SMS and voice MFA on 1 February 2027 with a blocking passkey prompt and no opt-out. Here is a dated plan for service accounts, break-glass and phoneless users.
Gov / DefenseSonicWall disclosed two actively exploited SMA1000 flaws on 1 September; CISA set a 5 September federal deadline. The harder problem is proving an appliance you cannot instrument is clean.
CERT-In scored an unauthenticated RCE in Manacle ERP at CVSS 10.0. The CVE is in NVD, but with no CPE data your scanner cannot match it. Here is how to fix that.
FortinetFortinet's emergency hotfix for CVE-2026-35616 blocked the attack path without fixing the flaw, and the complete patch that followed needed its own re-release.
Deep DiveWiz Research discovered that 10% of internet-facing LiteLLM AI proxy gateways accepted the default documentation admin key sk-1234, leaking upstream model keys and cloud IAM tokens.
CISA added 15 CVEs to the KEV catalog in six working days, including exploited flaws in LiteLLM and Kestra — AI tooling that most asset inventories never see.
CiscoTwelve fresh entries hit the Known Exploited Vulnerabilities catalog, covering Citrix NetScaler, Cisco FMC, Fortinet FortiOS, Adobe Commerce, N-able N-central and Chrome.
One tracker logged 315 leak-site posts from 40 groups in a single August week, eight of them new. Brand-based detection cannot keep pace. Here is what to instrument instead.
Trellix says APT28 routed command-and-control through filen.io during a three-day European phishing burst. Here is the behavioural detection logic that catches it when reputation cannot.
MicrosoftSharePoint Server 2016 and 2019 lost support on 14 July 2026 with no paid ESU on offer. Exchange 2016/2019 has until 31 October. Here is how to contain both.
Agentic AIPrompt injection is now OWASP’s top LLM risk with reported success rates of 50–84%. Organisations are shipping agents into production well ahead of their controls.
MicrosoftA repeatable triage model for very large monthly releases — what to expedite, what to schedule, and how to prove coverage afterwards.
MicrosoftMicrosoft’s September 2026 rollup addresses 973 CVEs, including two elevation-of-privilege bugs — in the Windows Update Stack and ALPC — confirmed under active attack.