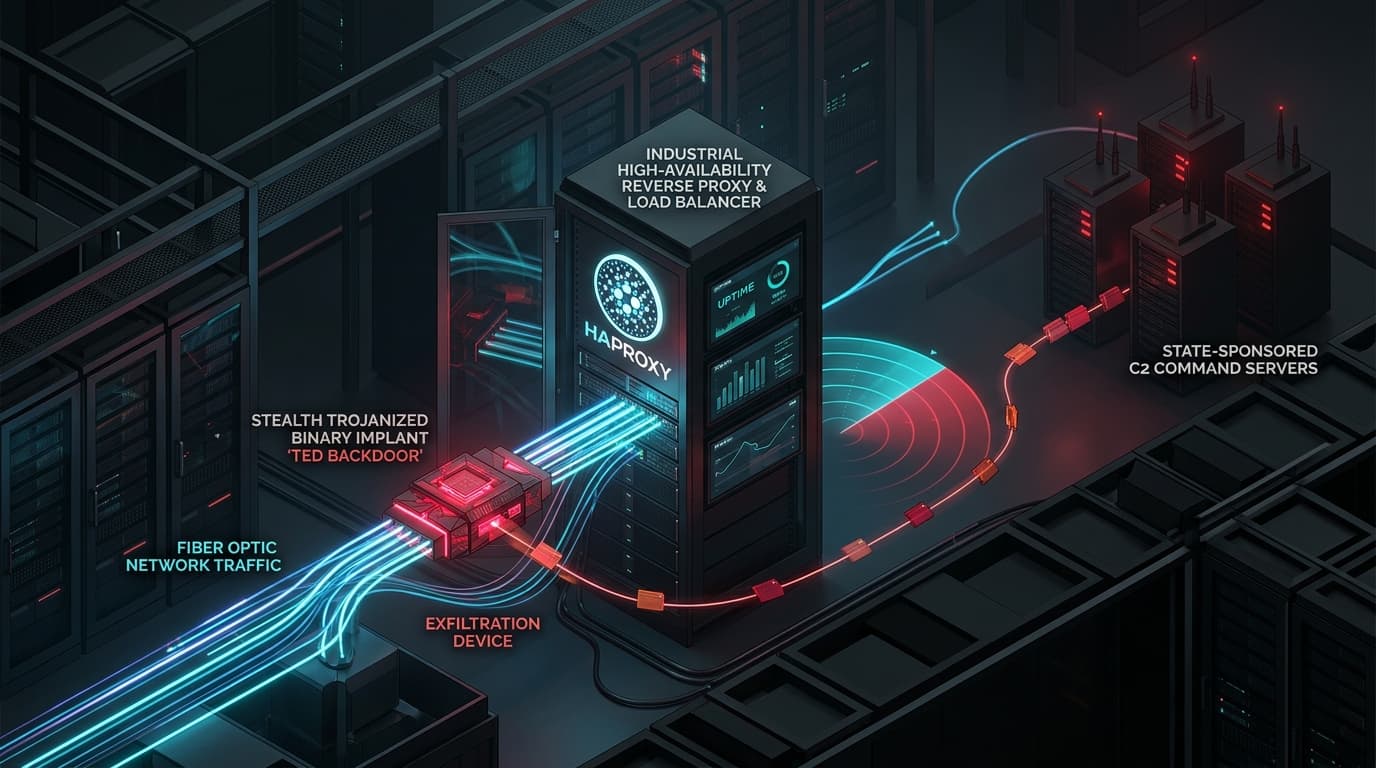
Security researchers at Rapid7 Labs have detailed TED, a highly sophisticated Linux implant compiled directly into trojanized HAProxy load balancer binaries deployed within enterprise networks in South Korea.
The operation, attributed with medium confidence to North Korean state-sponsored threat actors, affected major organizations across South Korea’s automotive manufacturing and media sectors, using load balancers as an invisible pivot point for traffic manipulation and espionage.
Compiling Persistence into HAProxy
Rather than dropping a separate malicious daemon that might trigger Linux endpoint detection agents, the adversaries modified the source code of HAProxy and compiled a custom binary. Because HAProxy naturally processes every incoming and outgoing HTTP/HTTPS connection, the implant sits directly in the traffic flow:
- Covert C2 Triggering: An operator triggers C2 communication by sending an HTTP GET request to an innocuous image path (e.g.,
/static/logo.png). - Connection Counter Tampering: Upon detecting the trigger, TED decrements HAProxy's internal live connection counters. As a result, the connection is instantly erased from HAProxy’s active statistics dashboard and administrative logs.
- In-Memory Named Pipe IPC: The implant redirects the request payload to a named pipe under
/tmp, executes the operator command, and emits a standardHTTP/1.0 200 OKresponse directly from the socket before the request ever reaches a backend application server.
Targeted Watering-Hole Delivery
In addition to functioning as an administrative backdoor, TED operated as an inline selective watering-hole mechanism. When ordinary public users visited the compromised sites, HAProxy forwarded requests normally.
However, when a visitor’s source IP matched a target list of corporate /24 subnets or carried a specific Accept-Language operator key, TED dynamically intercepted the outbound response, injected malicious JavaScript payloads, recalculated the HTTP Content-Length header, and stripped the Accept-Ranges header so browser developer tools would not detect discrepancy artifacts.
"By embedding malware within the load balancer itself, attackers evade backend logging completely. The backend application server never sees the attack, and the load balancer stats show zero anomalies."
Detection & Integrity Verification Runbook
Security teams managing Linux proxy and load-balancing infrastructure should execute the following verification steps:
- Verify Package Hashes: Verify the cryptographic integrity of the running HAProxy binary against vendor repository checksums using
debsums haproxy(Debian/Ubuntu) orrpm -V haproxy(RHEL/CentOS). - Inspect Anonymous Memory Mappings: Review HAProxy process maps (
/proc/[pid]/maps) for unusual writable and executable memory pages or unexpected dynamic shared objects. - Audit System Named Pipes: Scan
/tmpand/var/tmpfor named pipes (FIFO special files) created by unprivileged service accounts.