Threat IntelApache Airflow FAB Provider Flaw Lets OAuth Users Escalate to Admin
Apache Airflow releases security fix for CVE-2026-75156 in the Flask-AppBuilder provider, patching an OAuth2 role-mapping flaw leading to admin privilege escalation.
1,167 articles
Threat IntelApache Airflow releases security fix for CVE-2026-75156 in the Flask-AppBuilder provider, patching an OAuth2 role-mapping flaw leading to admin privilege escalation.
Threat IntelIBM resolves a denial of service vulnerability in WebSphere Application Server Liberty (CVE-2026-93909) where malformed HTTP/2 HPACK frames exhaust JVM heap memory.
MicrosoftMicrosoft addresses a critical Windows Remote Management command injection vulnerability (CVE-2026-96951) allowing remote code execution via WSMAN SOAP requests.
AWS CloudAWS resolves a high-severity OS command injection flaw in AWS Systems Manager Agent (CVE-2026-87911) affecting multi-step Run Command document execution.
GoogleGoogle Cloud updates authentication libraries for CVE-2026-19410 where improper audience validation allowed external OIDC tokens to impersonate IAM service accounts.
Threat IntelIvanti discloses critical vulnerability CVE-2026-104935 in Connect Secure and Policy Secure gateways allowing pre-auth SAML remote code execution.
GoogleGoogle Cloud resolves a high-severity privilege escalation flaw in Cloud Run and Artifact Registry auth helpers (CVE-2026-79696) exposing service account tokens.
AWS CloudAWS resolves an access control flaw in IAM Identity Center and AWS CLI session handling (CVE-2026-82856) where revoked STS tokens remained temporarily active.
Active ExploitISC resolves a critical assertion failure defect in BIND 9 nameservers (CVE-2015-5477) where a single malformed TKEY query crashes DNS daemons remotely.
MicrosoftMicrosoft addresses a critical privilege escalation flaw in Azure Arc Connected Machine Agent (CVE-2026-83711) exposing Hybrid Instance Metadata Service tokens.
Threat IntelApache Struts resolves critical vulnerability S2-032 (CVE-2016-3081) where dynamic method invocation enables arbitrary remote command execution via OGNL payloads.
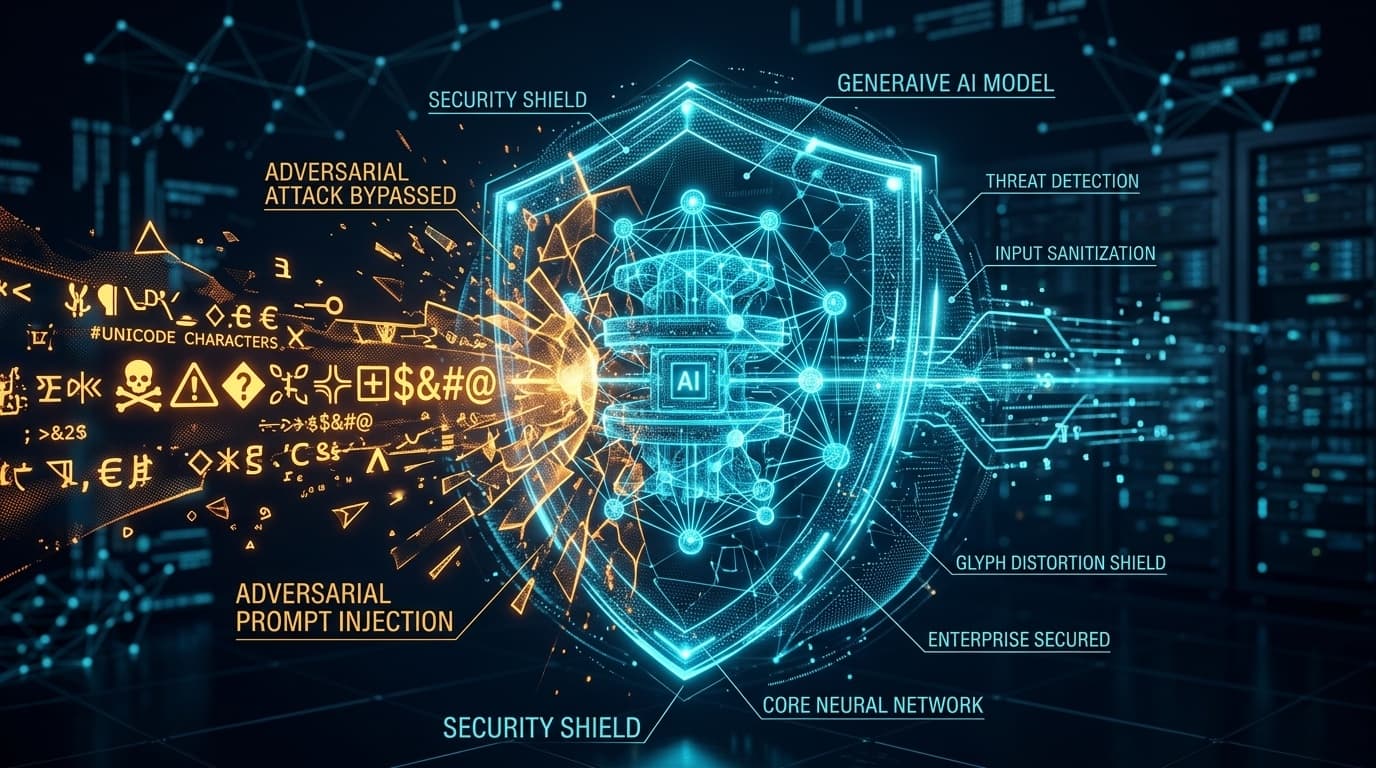
AWS CloudAWS resolves a security bypass vulnerability in Amazon Bedrock Guardrails where adversarial Unicode homoglyph sequences evaded safety and PII masking filters.
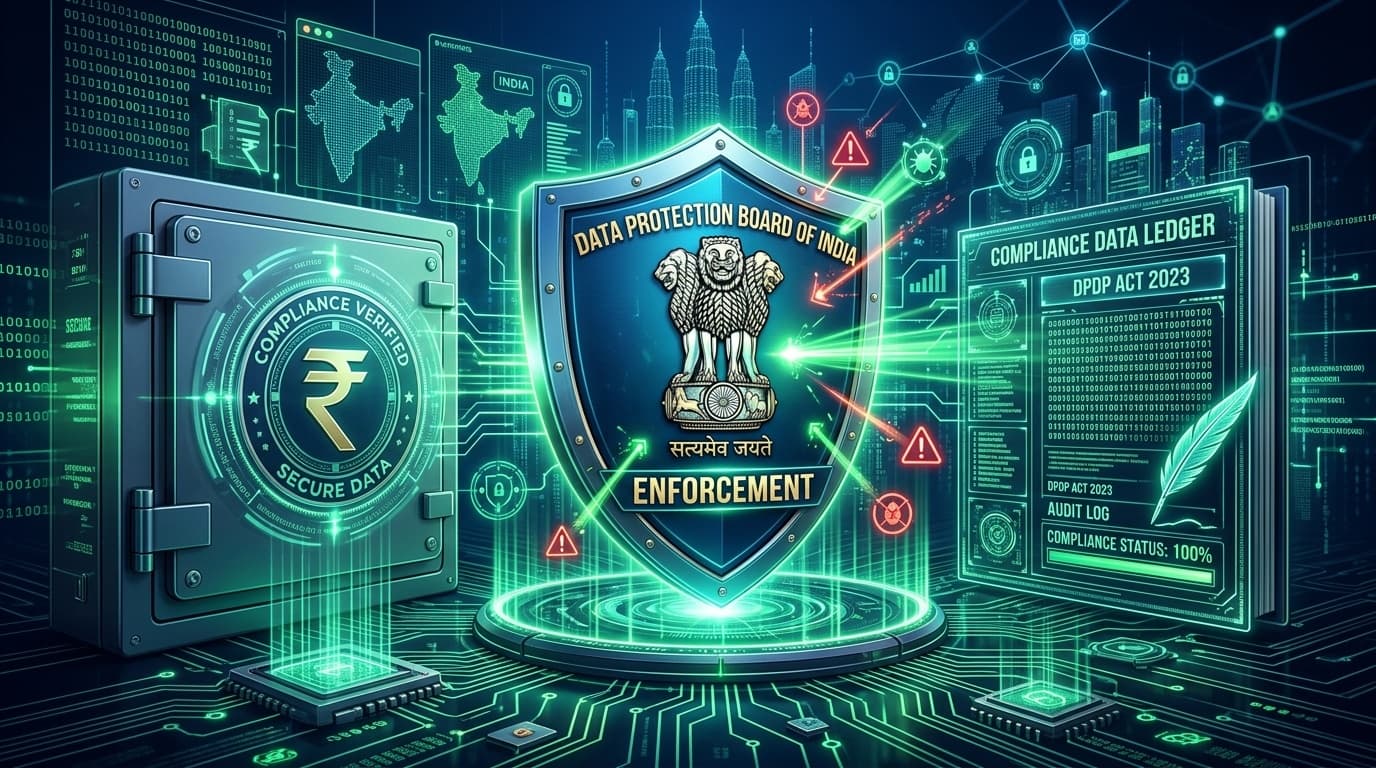
Deep DiveThe Data Protection Board of India issues regulatory show-cause notices to major enterprise data fiduciaries over non-compliant algorithmic impact assessments.
GoogleGoogle patches a high-severity desynchronization flaw in Cloud Armor edge proxies that allowed attackers to smuggle malicious HTTP/3 payloads past WAF rules.
MicrosoftA critical remote code execution flaw in Microsoft Semantic Kernel allows threat actors to compromise host systems via crafted agent plugin manifests.
AWS CloudAWS patches a critical vulnerability in IAM Identity Center (CVE-2026-78520) allowing manipulated SAML XML comments to bypass role assignment boundaries.
Cyber AttackA premier defense aerospace corporation files SEC Form 8-K Item 1.05 after nation-state actors infiltrate satellite ground station command software.
VulnerabilityvLLM patches a high-severity vulnerability (CVE-2026-78430) in multi-LoRA serving allowing concurrent tenants to extract proprietary adapter weights from GPU memory.
VulnerabilityEuropean Supervisory Authorities designate Critical ICT Third-Party Providers under DORA, granting regulators direct inspection powers over major cloud hyperscalers.
VulnerabilityHugging Face issues an urgent patch for Text Generation Inference (CVE-2026-78320, CVSS 9.3) fixing a critical Rust tokenizer deserialization vulnerability.
A major semiconductor EDA software firm files SEC Form 8-K Item 1.05 after nation-state threat actors exfiltrate next-gen 2nm chip design libraries.
VulnerabilityChromaDB patches a critical vulnerability (CVE-2026-78110) in vector metadata filtering that allows unauthenticated remote attackers to execute arbitrary code.
VulnerabilityIndia notifies updated DPDP Rules 2026 mandating Significant Data Fiduciaries implement cross-border transfer whitelists and third-party algorithmic audits.
VulnerabilityHashiCorp patches a critical flaw in Consul Service Mesh (CVE-2026-77340) allowing forged SPIFFE identity URIs to bypass mTLS intent enforcement.