Regulatory Mandate Overview
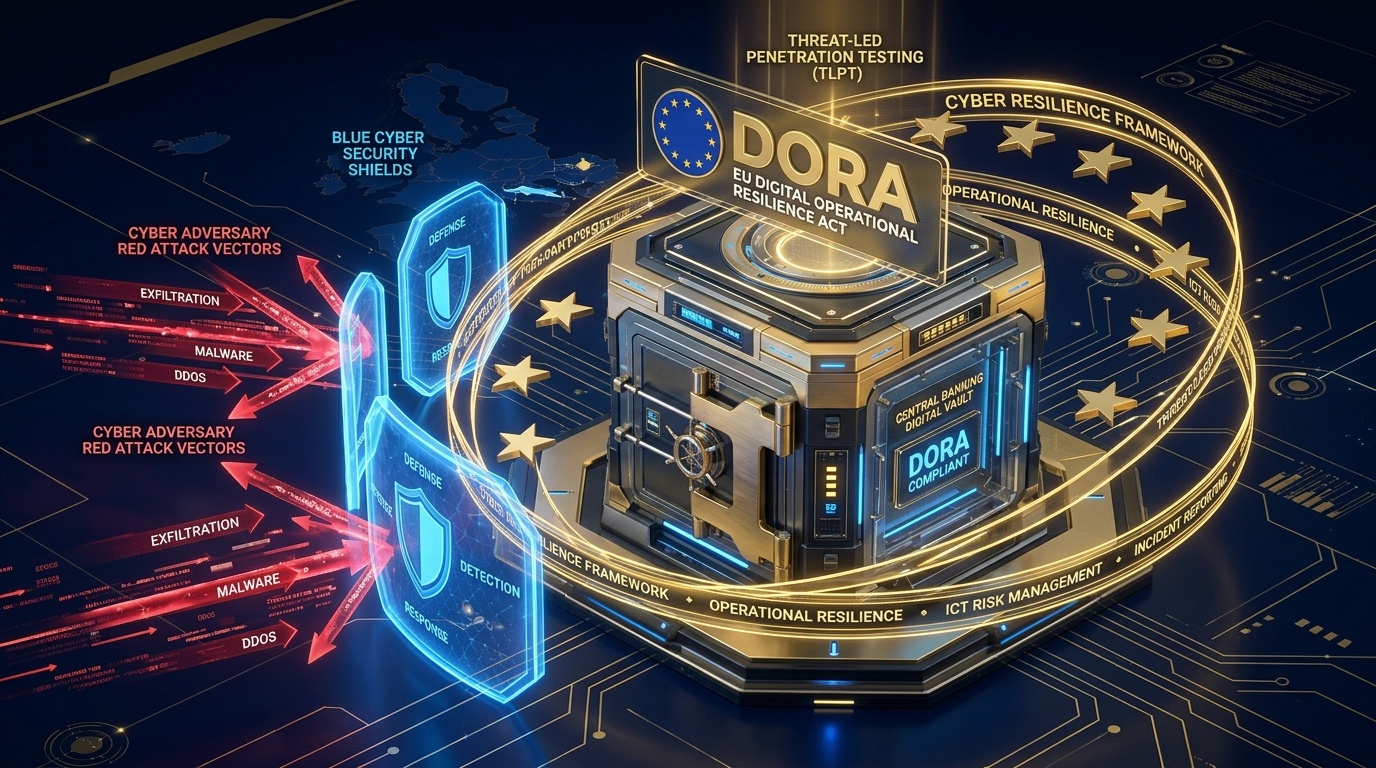
The European Supervisory Authorities (ESAs)—comprising the European Banking Authority (EBA), European Insurance and Occupational Pensions Authority (EIOPA), and European Securities and Markets Authority (ESMA)—have issued the finalized Regulatory Technical Standards (RTS) establishing the operational parameters for the Oversight Framework for Critical ICT Third-Party Providers (CTPPs) under the Digital Operational Resilience Act (DORA - Regulation EU 2022/2554).
This landmark regulatory shift marks the first time that European financial regulators are granted direct statutory supervision over commercial technology vendors and cloud hyperscalers that provide critical infrastructure to banks, asset managers, and insurance firms.
CTPP Designation Criteria & Supervisory Architecture
Under Article 31 of DORA, ICT third-party service providers are assessed annually by the ESAs against four quantitative and qualitative criteria to determine if they constitute a systemic concentration risk to the Union's financial stability:
| Designation Pillar | Assessment Metric | Regulatory Impact Threshold |
|---|---|---|
| Systemic Market Impact | Total number and asset value of financial entities relying on the ICT provider | Over 10% of total financial sector assets in multiple EU member states |
| Critical Workload Concentration | Reliance on provider for critical or important functions (payment settlement, core ledger) | Absence of immediate multi-cloud substitute providers |
| Interdependence & Scale | Downstream dependency of significant institutions (Global Systemically Important Banks - G-SIBs) | Systemic cross-border operational contagion potential |
Statutory Powers of the Lead Overseer
Each designated CTPP is assigned a designated Lead Overseer (one of the three ESAs). The Lead Overseer exercises extensive supervisory authority directly over the technology provider's European and global operations:
- Unannounced On-Site Inspections: Regulators possess statutory rights to access physical cloud data centers, operations command rooms, and security operating centers (SOCs) located within the EU or in third countries serving EU clients.
- Architecture Documentation & Source Code Access: Providers must supply complete architectural schematics, hypervisor isolation proofs, disaster recovery failover logs, and threat modeling assessments.
- Enforcement & Periodic Penalty Payments: If a CTPP fails to comply with supervisory recommendations, the Lead Overseer can impose periodic penalty payments of up to 1% of average daily global turnover for up to six months.
Contractual Readiness Roadmap for Financial Institutions
All financial institutions operating in the EU must immediately align their vendor management frameworks with Chapter V of DORA:
- Complete Vendor Registry Audit: Maintain an updated information register of all ICT contractual arrangements detailing critical functions supported by cloud providers.
- Incorporate Mandatory DORA Clauses: Update master service agreements (MSAs) to ensure vendors commit to full cooperation with the Lead Overseer's inspection teams and participate in pooled Threat-Led Penetration Testing (TLPT).
- Multi-Cloud Exit Strategies: Document and test comprehensive exit strategies and data portability mechanisms to ensure workloads can be transitioned without operational interruption in the event of vendor distress or supervisory termination orders.