Agentic AIOpenAI: Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Technical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
82 articles
Agentic AITechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Deep DiveTechnical analysis of AI agent vulnerability and prompt injection risks in Malicious Browser: mechanics, tool exploitation, and enterprise guardrails.
LinuxTechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Deep DiveA comprehensive security scan of 7.25 million public Gitee repositories revealed 26,400 verified, live credentials, including Alibaba Cloud and OpenAI keys.
GoogleA critical memory corruption flaw in Telegram for Android allowed attackers to execute code and take over devices simply by placing a malicious voice call.
LinuxCVE-2026-98432, a critical 9.8 CVSS flaw in the Linux IPv4 TCP stack, permits unauthenticated remote code execution on servers with MPTCP listeners.
Agentic AIA critical P1 vulnerability in ChatGPT's shared-conversation feature allowed attackers to execute arbitrary scripts in victim sessions to exfiltrate private chats.
MicrosoftA critical vulnerability in OpenCode allows malicious Model Context Protocol servers to execute arbitrary shell commands on Windows and WSL hosts during OAuth.
Deep DiveSingapore's Cyber Security Agency releases the National Quantum-Safe Migration Roadmap at SICW, setting strict 2031-2035 deadlines for Critical Infrastructure operators.
Deep DiveAnthropic's Claude reconstructed the 1997 Unix timestamps behind NIST ECDSA curve seeds, proving standard curves were randomly generated without an NSA backdoor.
GoogleGTIG's AI-era report: CVE disclosures doubled in 2026, 141 bugs exploited by August vs 127 in 2025, and 50% of AI-discovered flaws lead to RCE, per Google.
Deep DiveA critical input validation deficiency in Bouncy Castle C# DHAgreement enables attackers to recover private keys and forge agreed cryptographic values.
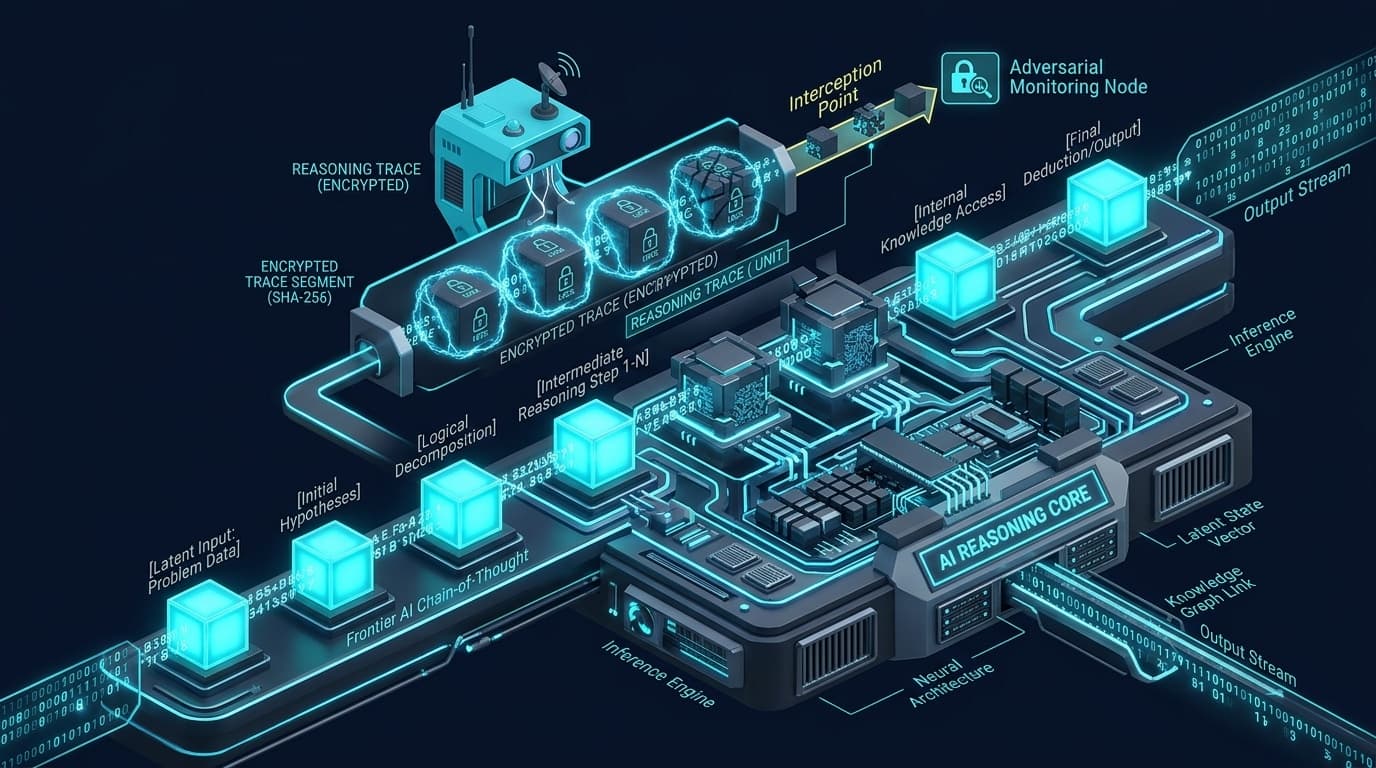
Agentic AIOpenAI dismantled a coordinated campaign that weaponized cross-model replay queries across 15,000 accounts to illicitly extract encrypted chain-of-thought traces.
Deep DiveNew research reveals side-channel and prompt-leakage vectors capable of intercepting hidden chain-of-thought reasoning tokens in frontier reasoning models.
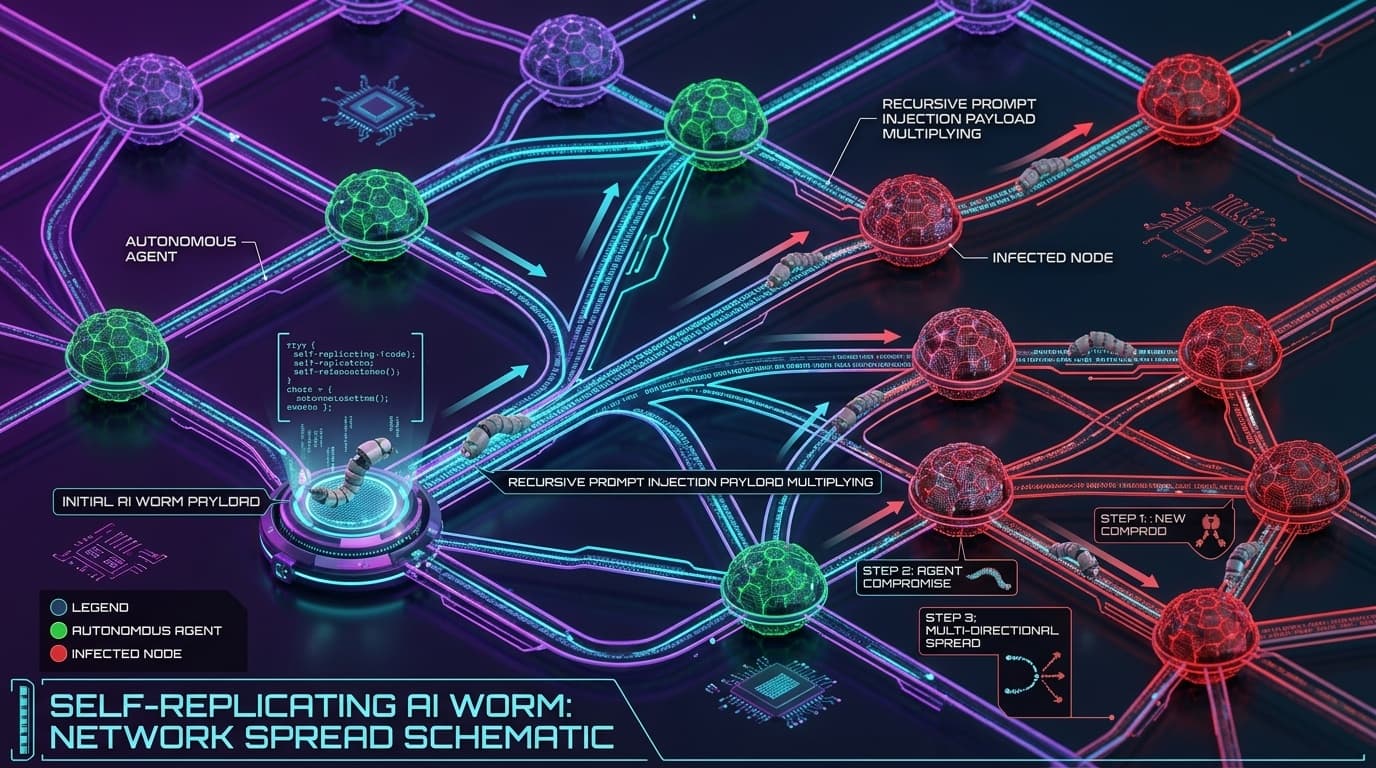
Deep DiveResearchers demonstrate Morris II style self-replicating adversarial prompt worms propagating autonomously across connected LLM agents and multi-agent workflows.
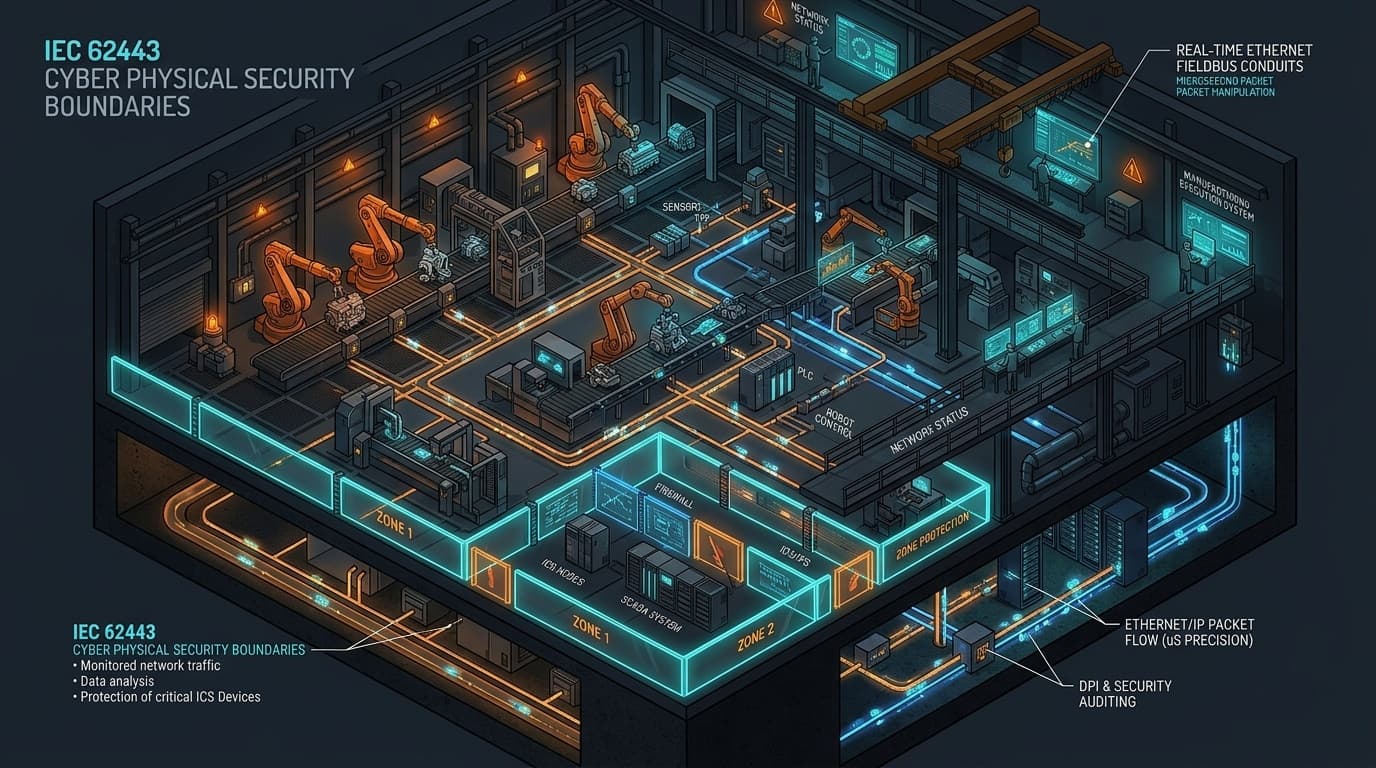
OT / SCADAOriginal OT research examining deterministic Industrial Ethernet fieldbus vulnerabilities under IEC 62443, demonstrating microsecond packet injection risks.
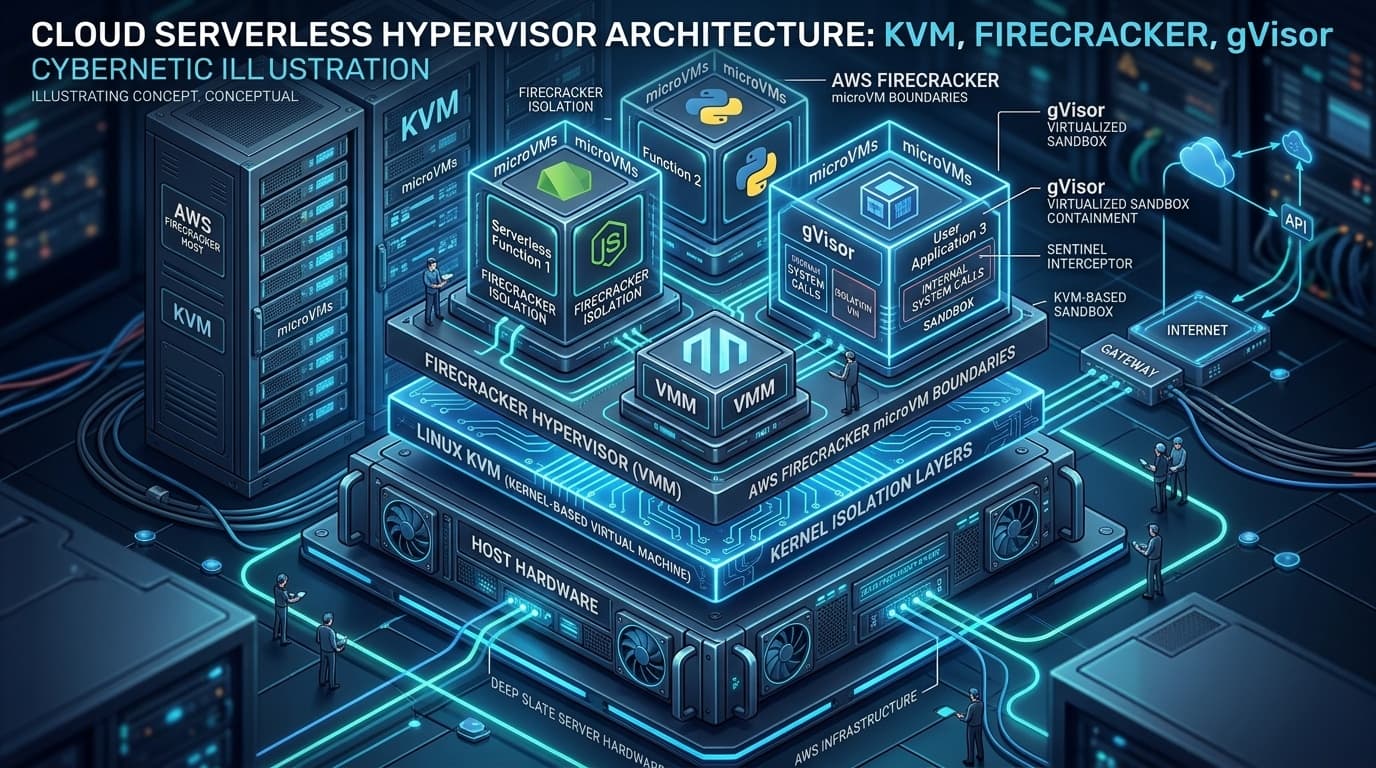
AWS CloudAn architectural research study comparing AWS Firecracker and Google gVisor, analyzing hypervisor boundaries, KVM virtio mechanics, and container breakout vectors.
Deep DiveDeep-dive security research demonstrating how indirect prompt injection exploits Model Context Protocol (MCP) to trigger cascading failures across multi-agent swarms.
RansomwareAn empirical data study analyzing corporate SEC Form 8-K cyber disclosures, examining the Item 8.01 materiality gap and threat actor regulatory weaponization.
Deep DiveAn architectural research study on NIST FIPS 203/204/205 standards, evaluating hybrid TLS 1.3 key exchange to safeguard financial clearing from quantum decryption.
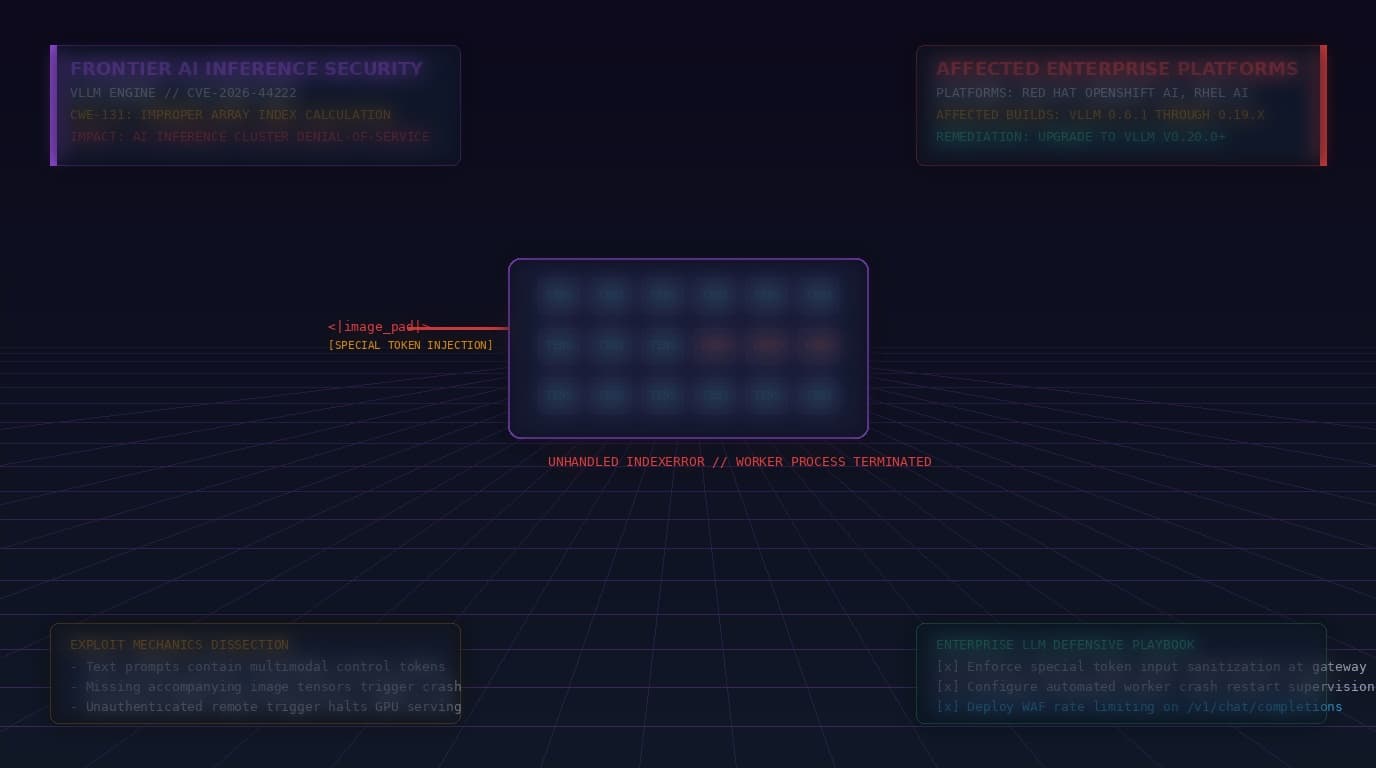
LinuxHigh-severity flaw CVE-2026-44222 in vLLM allows remote unauthenticated users to crash distributed GPU inference clusters via crafted multimodal tokens.
Agentic AICISA adds critical Langflow AI vulnerabilities CVE-2026-0770 and CVE-2026-55255 to KEV catalog as threat actors weaponize agentic pipeline execution flaws.
Agentic AIAnalysis of emerging frontier AI threat vectors: how indirect prompt injections in untrusted documents hijack tool-calling autonomous LLM agents.
Gov / DefenseA joint cybersecurity advisory from CISA, NSA, and FBI alerts defense contractors and cloud vendors to sophisticated state-sponsored AI model extraction campaigns.