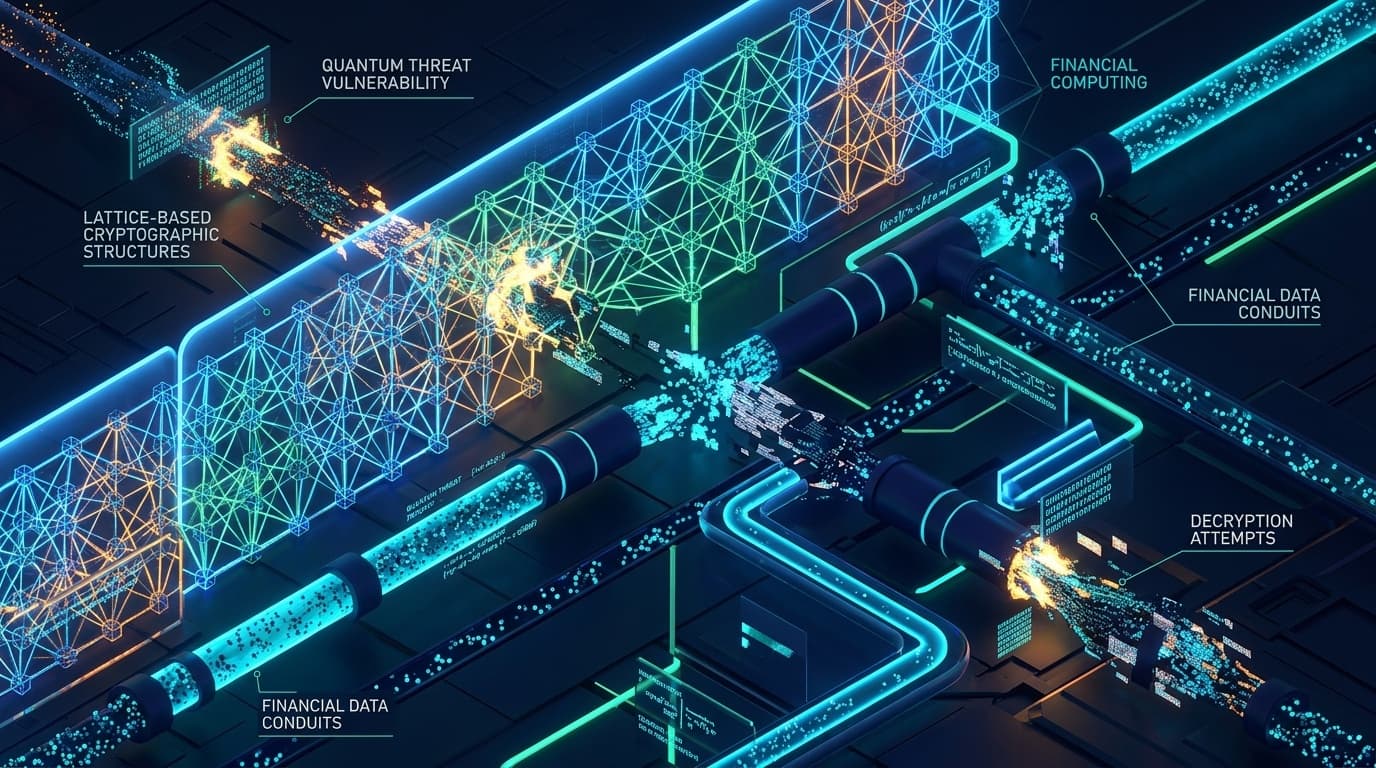
The finalization of FIPS 203 (ML-KEM), FIPS 204 (ML-DSA), and FIPS 205 (SLH-DSA) by the National Institute of Standards and Technology (NIST) marks a decisive turning point in enterprise cybersecurity. While commercial quantum computers capable of breaking asymmetric public-key cryptography remain on the medium-term horizon, intelligence telemetry confirms that state-aligned signals intelligence entities are aggressively executing "Harvest Now, Decrypt Later" (HNDL) campaigns. By passively recording encrypted financial settlement streams across submarine cables and cloud interconnects today, adversaries are building massive ciphertext archives intended for retrospective decryption once Cryptanalytically Relevant Quantum Computers (CRQCs) come online.
The Mechanics of Quantum Decryption: Shor's Algorithm vs. Classical Asymmetric Keys
The security of classical public-key cryptography rests upon two computationally intractable mathematical problems: the Integer Factorization Problem (underpinning RSA) and the Discrete Logarithm Problem over finite fields and elliptic curves (underpinning Diffie-Hellman and ECDSA).
On classical von Neumann computing architectures, the best known general algorithm for factoring large integers is the General Number Field Sieve (GNFS), which operates in sub-exponential time. However, Peter Shor's 1994 quantum algorithm demonstrates that a quantum computer utilizing quantum Fourier transforms can compute period finding in polynomial time:
# Quantum vs Classical Complexity Scaling
Classical (GNFS):  O(exp((c + o(1)) * (ln N)^(1/3) * (ln ln N)^(2/3)))
Quantum (Shor):     O((log N)^2 * (log log N) * (log log log N))
A CRQC possessing approximately 4,096 stable, error-corrected physical qubits (running ~20 million noisy qubits under surface-code fault tolerance) could factor an RSA-2048 modulus in less than 8 hours, completely compromising legacy TLS session keys, digital signature non-repudiation, and long-term financial settlement records.
Lattice-Based Cryptography: The Architecture of FIPS 203 (ML-KEM)
To replace vulnerable Diffie-Hellman exchanges, NIST selected the Module-Lattice-Based Key-Encapsulation Mechanism (ML-KEM), derived from the CRYSTALS-Kyber algorithm. ML-KEM bases its security on the hardness of the Module Learning With Errors (M-LWE) problem over structured polynomial rings:
Given a random matrix A over a polynomial ring and a target vector b = A * s + e (where s is a secret vector and e is a small error noise polynomial), finding s without knowledge of e is proven to be as hard as finding the shortest vector in high-dimensional geometric lattices—a problem that Shor's algorithm cannot solve in polynomial time.
Cryptographic Performance & Wire Overhead Comparison
| Cryptographic Algorithm | Underlying Math Problem | Public Key Size | Ciphertext / Sig Size | Quantum Security Level |
|---|---|---|---|---|
| RSA-2048 (Classical) | Integer Factorization | 256 bytes | 256 bytes | 0 bits (Broken) |
| ECDH P-256 (Classical) | Elliptic Curve Discrete Log | 64 bytes | 64 bytes | 0 bits (Broken) |
| ML-KEM-512 (FIPS 203) | Module-LWE (Lattice) | 800 bytes | 768 bytes | NIST Level 1 (~AES-128) |
| ML-KEM-768 (FIPS 203) | Module-LWE (Lattice) | 1,184 bytes | 1,088 bytes | NIST Level 3 (~AES-192) |
| ML-KEM-1024 (FIPS 203) | Module-LWE (Lattice) | 1,568 bytes | 1,568 bytes | NIST Level 5 (~AES-256) |
Engineering Transition: Implementing Hybrid TLS 1.3 Key Exchange
During the multi-year transition window, financial institutions cannot abruptly deprecate classical algorithms due to legacy hardware constraints and formal compliance mandates (e.g., FIPS 140-2 validations). The recommended path is Hybrid Key Exchange, combining an established classical algorithm (X25519) with a post-quantum KEM (ML-KEM-768).
Under this hybrid scheme, two shared secrets are established independently and combined using a cryptographically secure Key Derivation Function (HKDF-Extract):
# Hybrid Key Encapsulation in TLS 1.3 Handshake (X25519 + ML-KEM-768)
Shared_Secret_Classic = ECDH(Client_Private_X25519, Server_Public_X25519)
Shared_Secret_PQC     = Decapsulate(Server_Private_MLKEM, Client_Ciphertext_MLKEM)

# Combined master secret resistant to classical and quantum cryptanalysis
Master_Secret = HKDF-Extract(Salt=0, IKM=Shared_Secret_Classic || Shared_Secret_PQC)
Even if an adversary possesses a CRQC in 2032, they cannot derive the Master_Secret without also cracking the classical elliptic curve component in polynomial time, and vice versa.
Banking Infrastructure Implementation Playbook
- Conduct Immediate Cryptographic Discovery: Audit all automated payment gateways, Real-Time Gross Settlement (RTGS) pipes, and SWIFT messaging nodes to catalogue instances of hardcoded RSA and static Diffie-Hellman parameter sets.
- Deploy Hybrid TLS 1.3 Ciphersuites: Configure edge reverse proxies and API gateways (Envoy, Nginx, Cloudflare) to support the
X25519MLKEM768key exchange group for all interbank communications. - Upgrade Hardware Security Modules (HSMs): Engage HSM vendors to verify firmware roadmap support for FIPS 204 digital signature generation across financial transaction signing pipelines.
- Align with Regulatory Milestones: Comply with CISA's Quantum-Readiness Roadmap and the Reserve Bank of India (RBI) IT framework directing systematic retirement of pre-quantum algorithms across tier-1 financial infrastructure.