AWS CloudCloud Identity Theft and S3 Exfiltration Fuel Surge in SEC Cyber Disclosures
SEC Form 8-K disclosures reveal a surge in material cyber incidents driven by cloud identity theft and automated data lake exfiltration.
Senior Threat Intelligence Reporter
Daniel tracks ransomware crews, initial access brokers and state-aligned intrusion sets. He previously worked as a SOC analyst and still writes his own detection rules.
189 articles
AWS CloudSEC Form 8-K disclosures reveal a surge in material cyber incidents driven by cloud identity theft and automated data lake exfiltration.
AWS CloudAWS Security Bulletin details an authorization validation defect in S3 Multi-Region Access Point endpoints permitting IAM privilege escalation.
LinuxAttackers are weaponizing an exploit chain in Zammad helpdesk combining session fixation (CVE-2026-102489) with root privilege escalation (CVE-2026-102490).
Threat IntelKiteworks fixed a CVSS 10 root code-execution flaw in Email Protection Gateway (CVE-2026-54154) and three 9.8 account takeovers. Upgrade EPG and Core to 9.5.1.
Citrix NetScalerCitrix fixes CVE-2026-88779, a SAML memory overflow that crashes NetScaler ADC and Gateway. Last week's 14.1-73.37 and 13.1-64.23 builds are still vulnerable.
MicrosoftExchange Server CVE-2026-96940 lets authenticated users read other mailboxes. Microsoft rates it Exploitation More Likely. Install the September 2026 v2 SU.
MicrosoftCisco Talos ties China-nexus UAT-11587 to Antino, a Rust backdoor taking orders via Outlook and exfiltrating via OneDrive, on ~350 endpoints in 8 countries.
MicrosoftProofpoint: China-aligned TA419 posed as an ex-White House OSTP official and an Anthropic employee to steal AI policy experts' Microsoft 365 sessions.
OT / SCADAA critical stack buffer overflow in Moxa industrial protocol gateways allows authenticated attackers to corrupt memory and hijack critical substation controllers.
OT / SCADACISA advisory ICSA-26-272-07 reveals permanent hardcoded cloud storage credentials in the Viidure Dashcam app, exposing commercial fleets to full takeover.
OT / SCADAA pre-authentication integer underflow in MikroTik RouterOS WebFig allows unauthenticated network attackers to achieve remote code execution as root.
RansomwareA multinational law enforcement sweep led by German, Spanish, and Romanian police has dismantled KillSec, arresting three operators and seizing 110TB of data.
OT / SCADAA critical OS command injection vulnerability in Johnson Controls EasyIO FS32 controllers allows network attackers to gain root access and hijack HVAC control logic.
Threat IntelHardcoded passwords in Teledyne FLIR Aware2 software expose PackBot and FirstLook tactical EOD and defense robots to remote unauthenticated takeover.
FortinetFortinet resolves a high-severity improper access control flaw in FortiSandbox (CVE-2026-26084) allowing unauthenticated attackers to expose forensic analysis data.
Threat IntelA missing authentication flaw in PTZOptics cameras and Firmware Upgrade Tools allows unauthenticated attackers to flash malicious firmware remotely.
RansomwareRhysida ransomware group exfiltrates 2.44 Terabytes of clinical patient files and medical records from General Santos Doctors Hospital in an 8-Bitcoin extortion scheme.
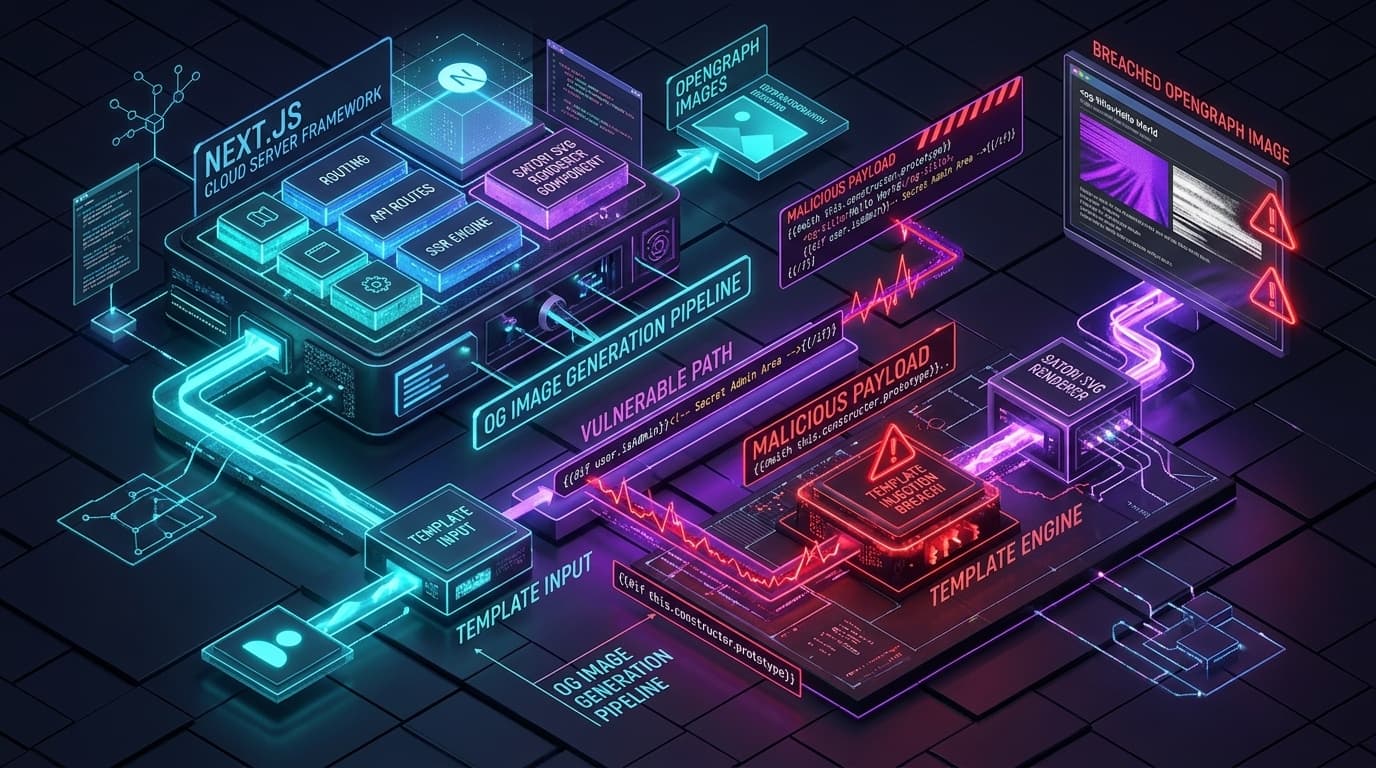
Threat IntelA critical template injection flaw in Next.js next/og (CVE-2026-94545) allows unauthenticated remote attackers to execute arbitrary code via Satori SVG parsing.
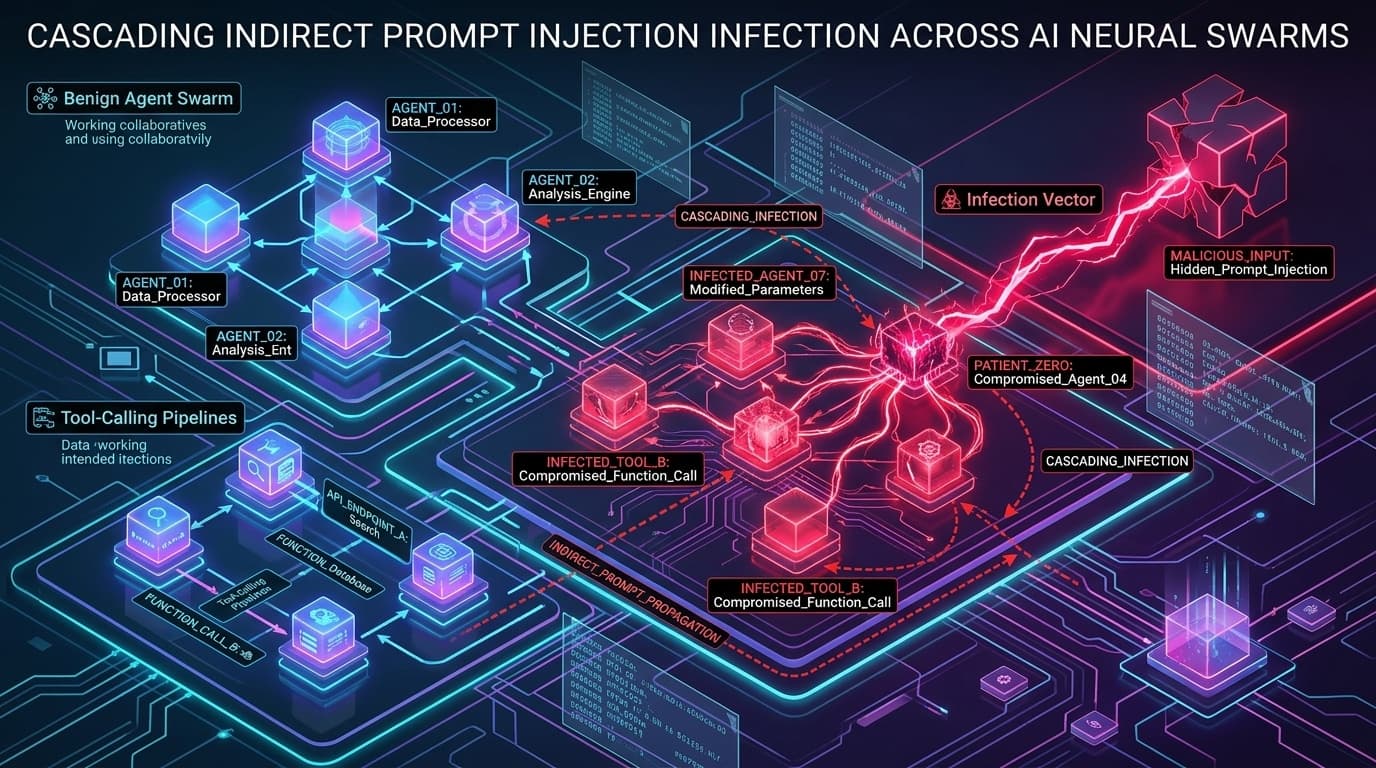
Deep DiveDeep-dive security research demonstrating how indirect prompt injection exploits Model Context Protocol (MCP) to trigger cascading failures across multi-agent swarms.
Threat IntelA high-severity path traversal vulnerability in langchain-core allows attackers processing untrusted prompt configurations to read arbitrary host filesystem data.
Threat IntelA critical CVSS 9.8 vulnerability in Nginx UI permits unauthenticated attackers to execute arbitrary commands via exposed Model Context Protocol endpoints.
Deep DiveThe European Supervisory Authorities have finalized technical standards under the Digital Operational Resilience Act (DORA), mandating 4-hour ICT incident alerts.
OT / SCADAA technical engineering guide on implementing IEC 62443-3-2 Zones and Conduits to isolate critical PLC and SCADA assets against cyberattacks.
Threat IntelA critical CVSS 9.8 remote code execution vulnerability in Code Runner Model Context Protocol servers permits arbitrary host code execution via untrusted AI agent tool calls.