Topic
SCADA Security: news, advisories and analysis
7 articles
CyberSecureToday covers SCADA Security across 7 articles published between 17 Sep 2026 and 17 Oct 2026. The coverage includes 7 vulnerability advisories. 7 advisories are rated critical or high severity.
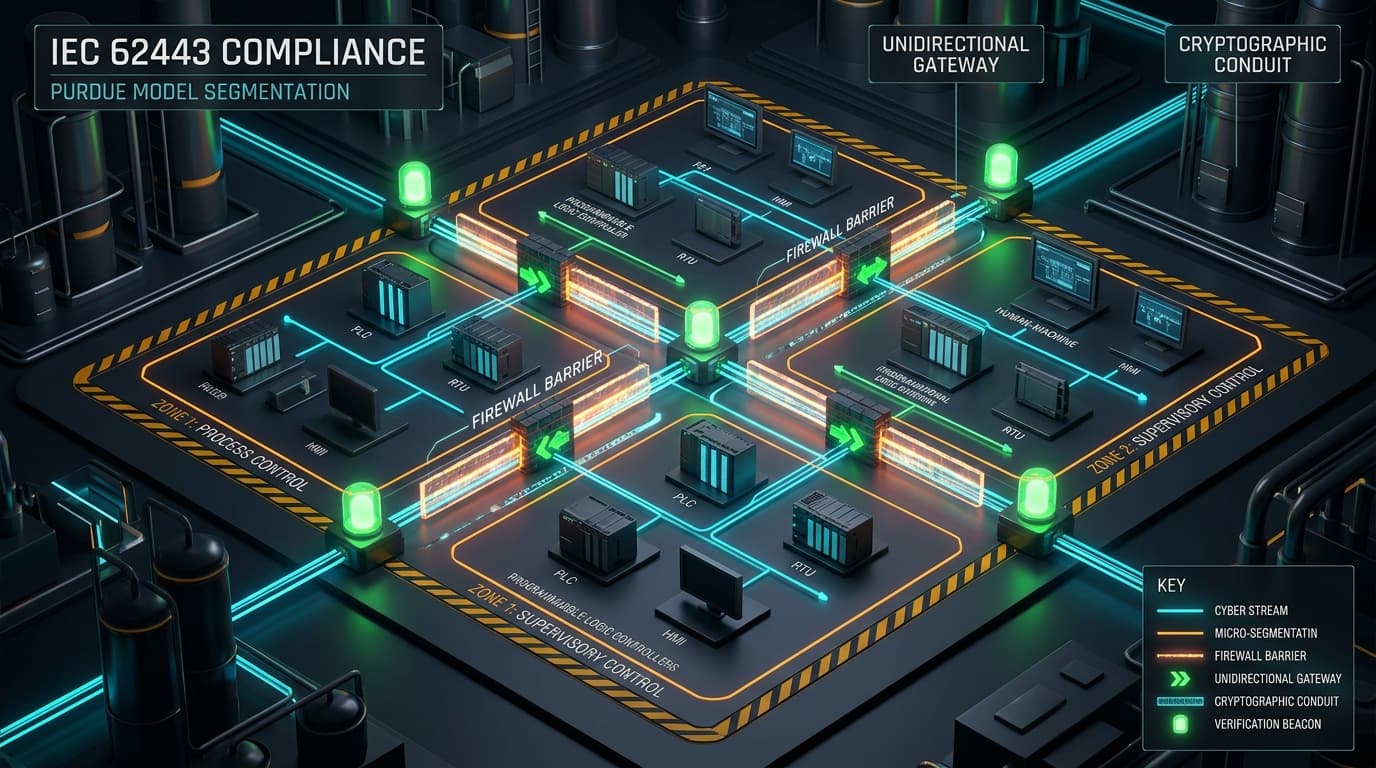
Stories on SCADA Security most often intersect with IEC 62443, Industrial OT and Schneider Electric, with Industrial, OT & IoT the most affected sector. The most recent story, “Eclipse Milo OPC UA Flaws Let Low-Privileged Actors Bypass Method Authorization”, was published 17 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Latest coverage
ThreatsIndustrial & OTCriticalMei-Lin Chen
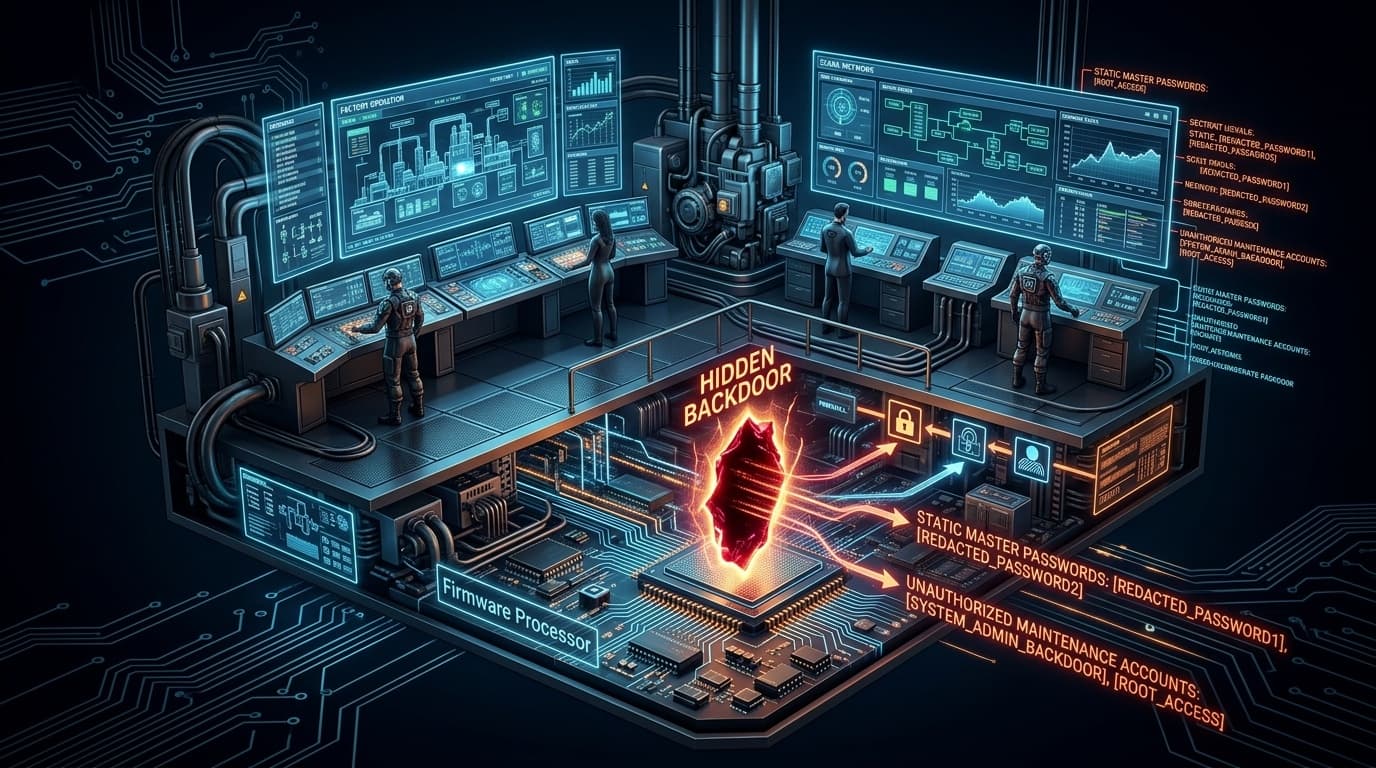
ThreatsIndustrial & OTCriticalHitachi Industrial Systems Undocumented Administrative Backdoor and Static Credentials Exposed in Production (CVE-2026-82829)
CST Editorial Desk
ThreatsIndustrial & OTHighSchneider Electric Modicon M340 FTP Flaw Enables Remote Denial of Service
Daniel Okafor
ThreatsIndustrial & OTHighSiemens SICAM 8 Remote Parameterization Resource Exhaustion Flaw Disables Substation Automation Controllers
CST Editorial Desk
ThreatsIndustrial & OTCriticalSchneider Electric Modicon M580 Authentication Flaw Risks Industrial Process Takeover
CST Editorial Desk
ThreatsIndustrial & OTHighRockwell Automation FactoryTalk Activation Manager Flaw Enables Local SYSTEM Privilege Escalation
CST Editorial Desk
ThreatsIndustrial & OTHighSchneider Electric SCADAPack x70 RTUs Exposed to Remote Credential Extraction Flaws
Aisha Noor