A critical backdoor vulnerability has been confirmed in Hitachi Coding Software Suite (HCSS), the industrial manufacturing and packaging execution software developed by Hitachi Industrial Equipment Systems. Identified under CVE-2026-82829 and published in GitHub Advisory GHSA-gf4c-rx3m-whpx with a CVSS v3.1 rating of 9.8 (Critical), the security flaw involves undocumented hidden functionality and hardcoded factory maintenance credentials embedded in all releases through version 3.3.0, allowing unauthorized remote actors to obtain unrestricted administrative control over automated factory labeling and printing machinery.
Hidden Maintenance Interfaces in Industrial Automation (IACS)
In industrial operational technology (OT) software, equipment vendors historically integrated undocumented diagnostic accounts or static master passwords to facilitate rapid on-site troubleshooting by field technicians without needing customer credentials. Under modern cybersecurity frameworks (such as IEC 62443-4-2 and CISA Cross-Sector Cybersecurity Performance Goals), hardcoded accounts and hidden functionality (CWE-912) are classified as critical supply chain vulnerabilities.
Vulnerability Mechanics: Hardcoded Maintenance Credentials (CWE-912)
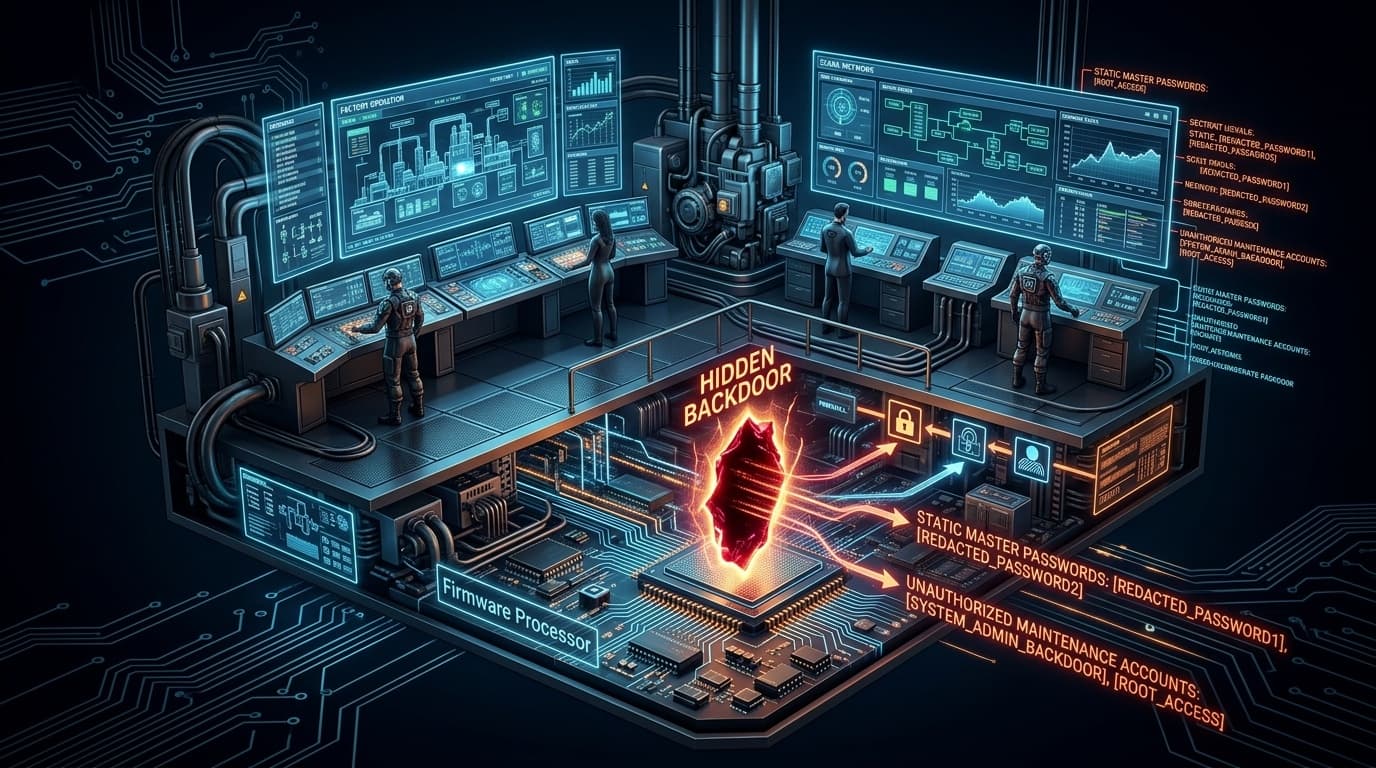
In Hitachi Coding Software Suite through version 3.3.0, reverse-engineering of the application binaries revealed static internal accounts hardcoded into the local authentication database initialization routines:
// Decompiled Database Seed Routine in HCSS (<= 3.3.0)
void InitializeSecurityDatabase() {
    // User-created administrative accounts
    CreateStandardAdminUser();

    // FATAL FLAW: Undocumented factory maintenance account created automatically!
    // Static username and immutable password hash seeded on all production installs:
    UserRecord maintenanceUser;
    maintenanceUser.username = "hitachi_service_maint";
    maintenanceUser.passwordHash = "$2a$10$StaticFactoryMaintenanceHash...";
    maintenanceUser.role = ROLE_SUPER_ADMINISTRATOR;
    maintenanceUser.isHidden = true; // Hidden from GUI User Management Table!

    Database::InsertUser(maintenanceUser);
}
Because the account is explicitly flagged as hidden, plant operators reviewing user accounts through the HCSS GUI cannot observe its existence or modify its credentials.
Once the static password string was recovered, remote adversaries scanning OT networks for open HCSS communication ports could authenticate directly as the hidden super-administrator. The access level provides full read/write rights over printer job configurations, laser frequency parameters, and underlying operating system service commands.
Supply Chain Risk in Regulated Manufacturing
| Regulated Sector | HCSS Deployment Role | Threat Consequence |
|---|---|---|
| Pharmaceuticals | DSCSA / FDA serialization tracking | Counterfeit medications stamped with valid batch codes; regulatory recall |
| Food & Beverage | Allergen warning & expiration dates | Tampered expiry dates causing public health hazards and liability |
| Semiconductor Fabrication | Wafer and component laser marking | Component tracking desynchronization and factory yield sabotage |
Remediation & Defense Actions
- Upgrade to HCSS 3.4.0: Deploy the official vendor patch immediately. Version 3.4.0 completely excises the hidden maintenance account from the database schema and removes static credentials from all software binaries.
- Isolate Supervisory Workstations: Ensure engineering PCs hosting HCSS cannot communicate with corporate internet gateways or remote desktop proxies.
- Implement OT Network Traffic Monitoring: Deploy industrial intrusion detection systems (IDS) to monitor Modbus/TCP, Ethernet/IP, and proprietary HCSS traffic for anomalous administrative commands originating outside approved engineering consoles.