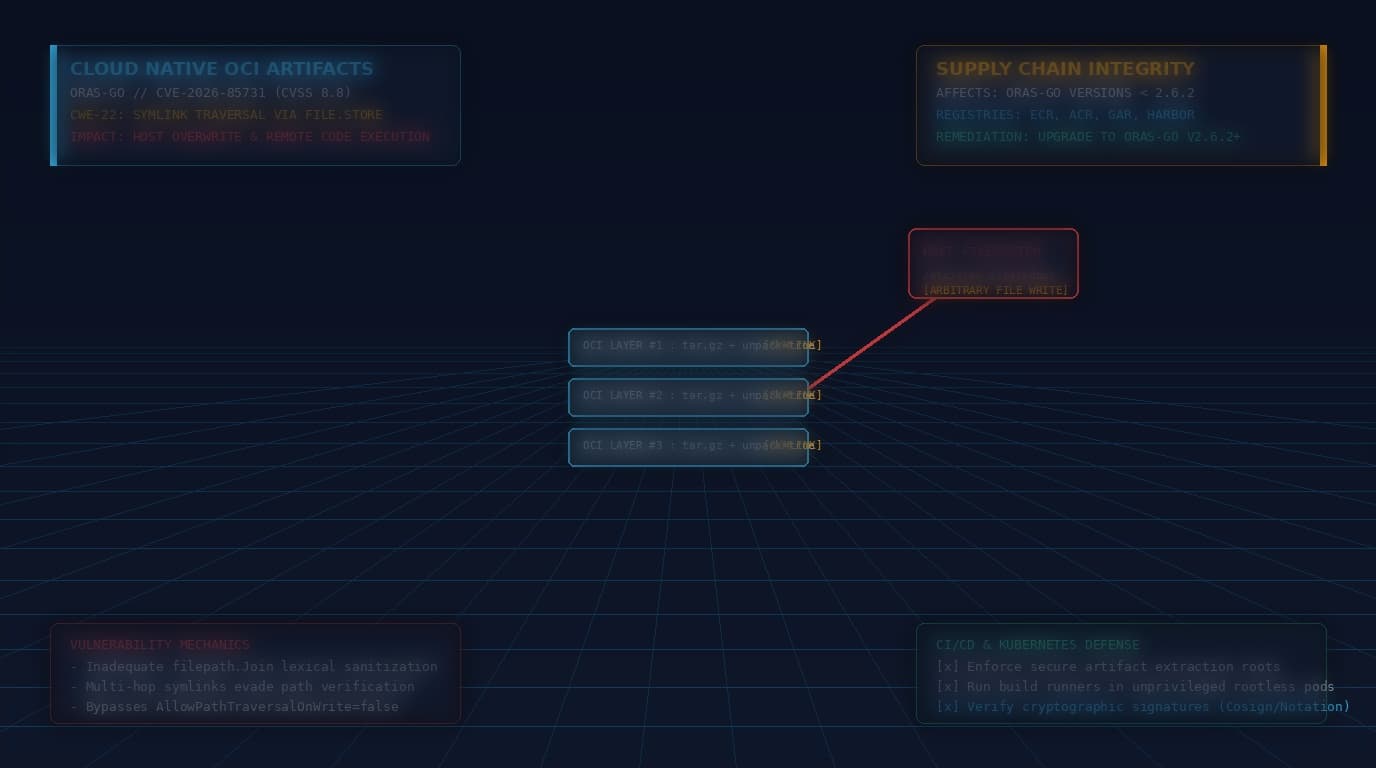
ThreatsCloud & SaaSHighCritical OCI Artifact Library Flaw in ORAS-Go Enables Symlink Path Traversal and Supply Chain Compromise CVE-2026-85731A high-severity CVSS 8.8 path traversal vulnerability in oras-go allows malicious OCI container artifacts to escape extraction roots and execute arbitrary code.CST Newsroom·23 Sep 2026, 08:00 IST·16 min read