 Microsoft
 Windows IKE Protocol Double-Free RCE Flaw Exploited in Active Network Attacks
ThreatsCloud & SaaSCVE-2026-33824ExploitedKEV
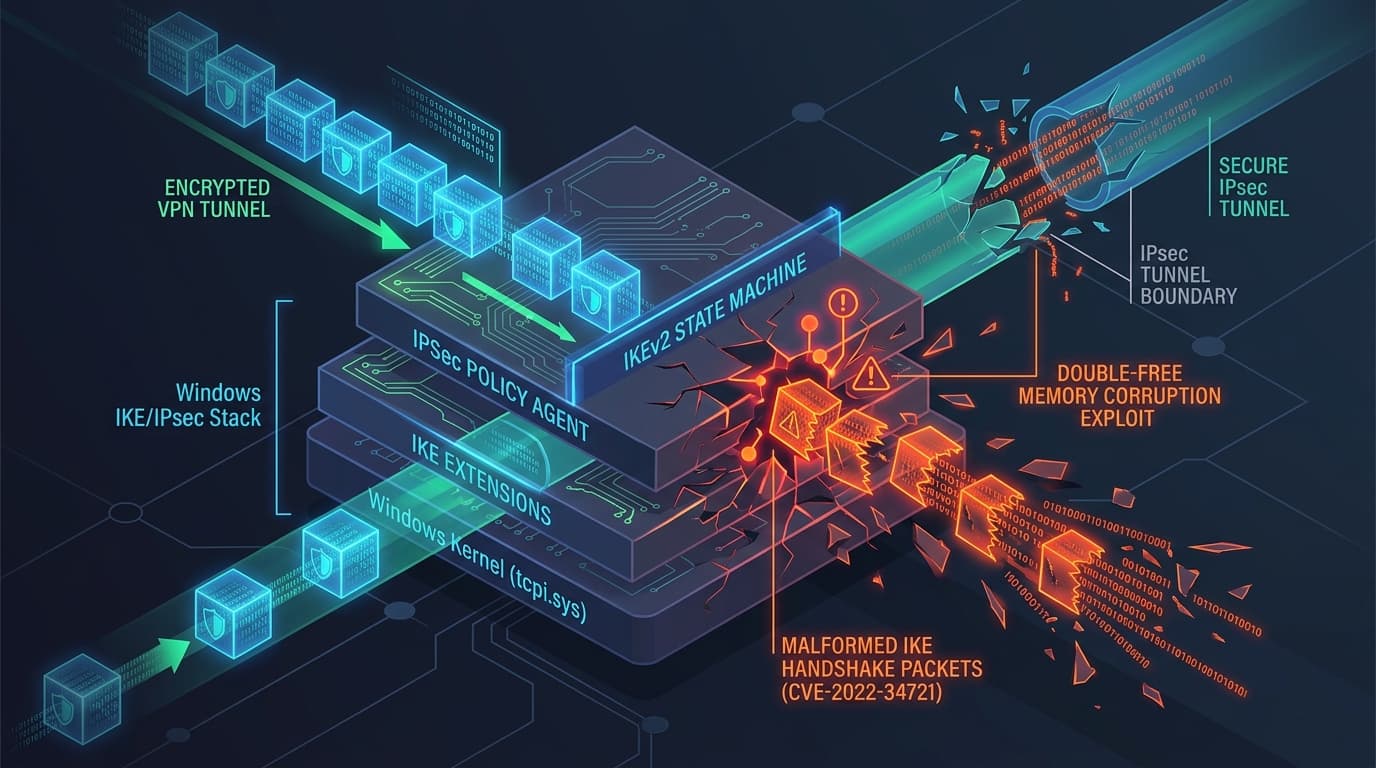
CISA confirms active in-the-wild exploitation of CVE-2026-33824, an unauthenticated double-free memory corruption flaw in Windows IKE enabling remote root code execution over UDP 500.
Mei-Lin Chen8 min read