Agentic AIOpenAI: Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Technical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Topic
54 articles
Agentic AITechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Deep DiveTechnical analysis of AI agent vulnerability and prompt injection risks in Malicious Browser: mechanics, tool exploitation, and enterprise guardrails.
LinuxTechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
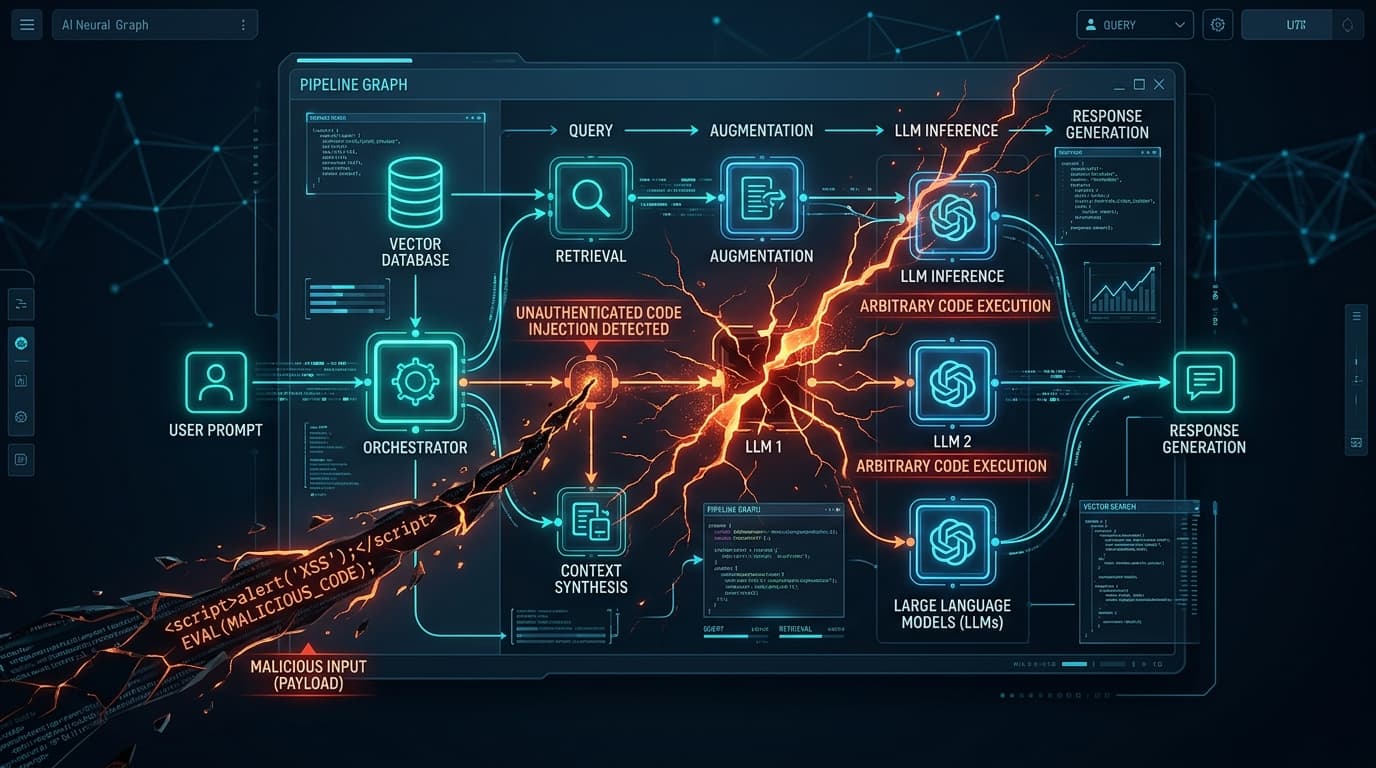
Active ExploitCISA adds CVE-2026-9198 to KEV, warning of active remote code injection attacks weaponizing visual AI workflow builder IBM Langflow in enterprise environments.
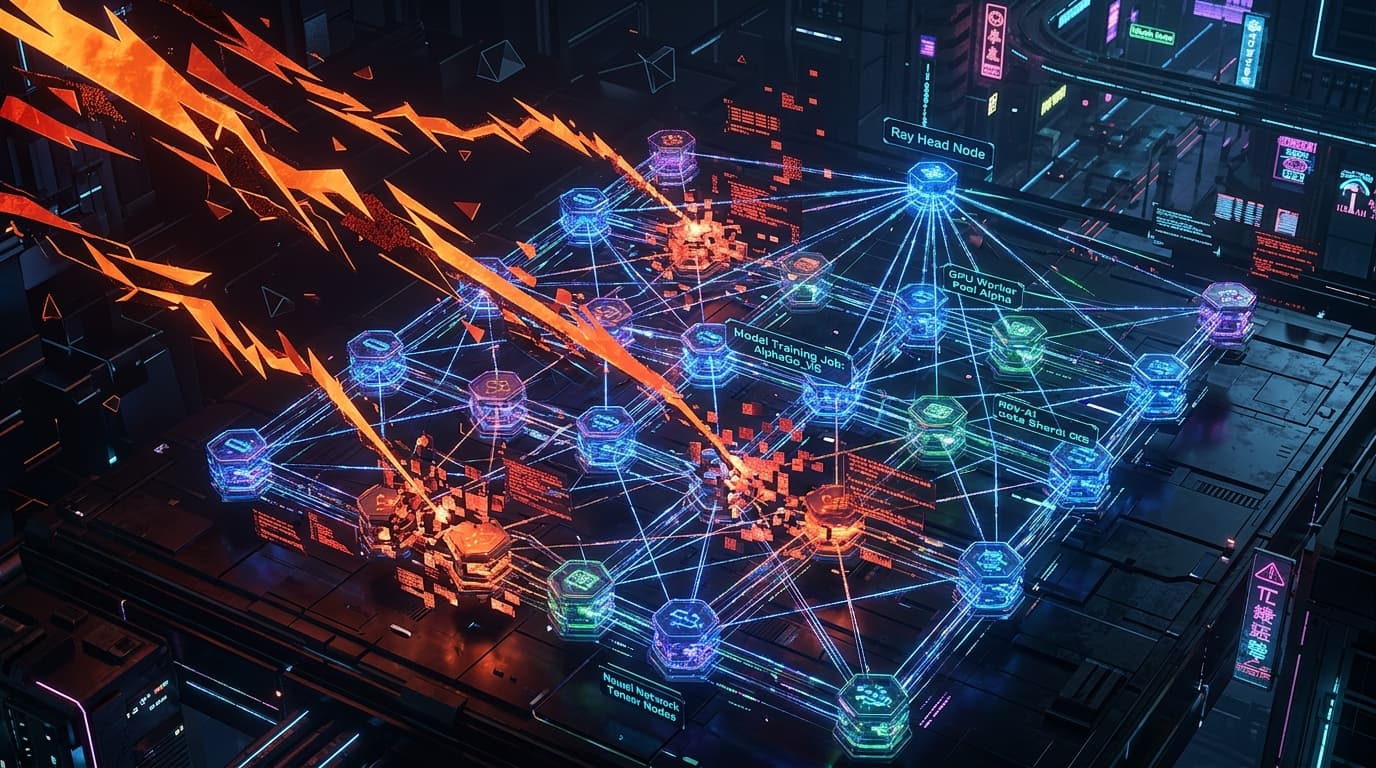
Active ExploitCISA issues an emergency directive on CVE-2025-62593, warning that unauthenticated code injection in Ray AI distributed computing clusters allows adversaries to seize GPU clusters and training models.
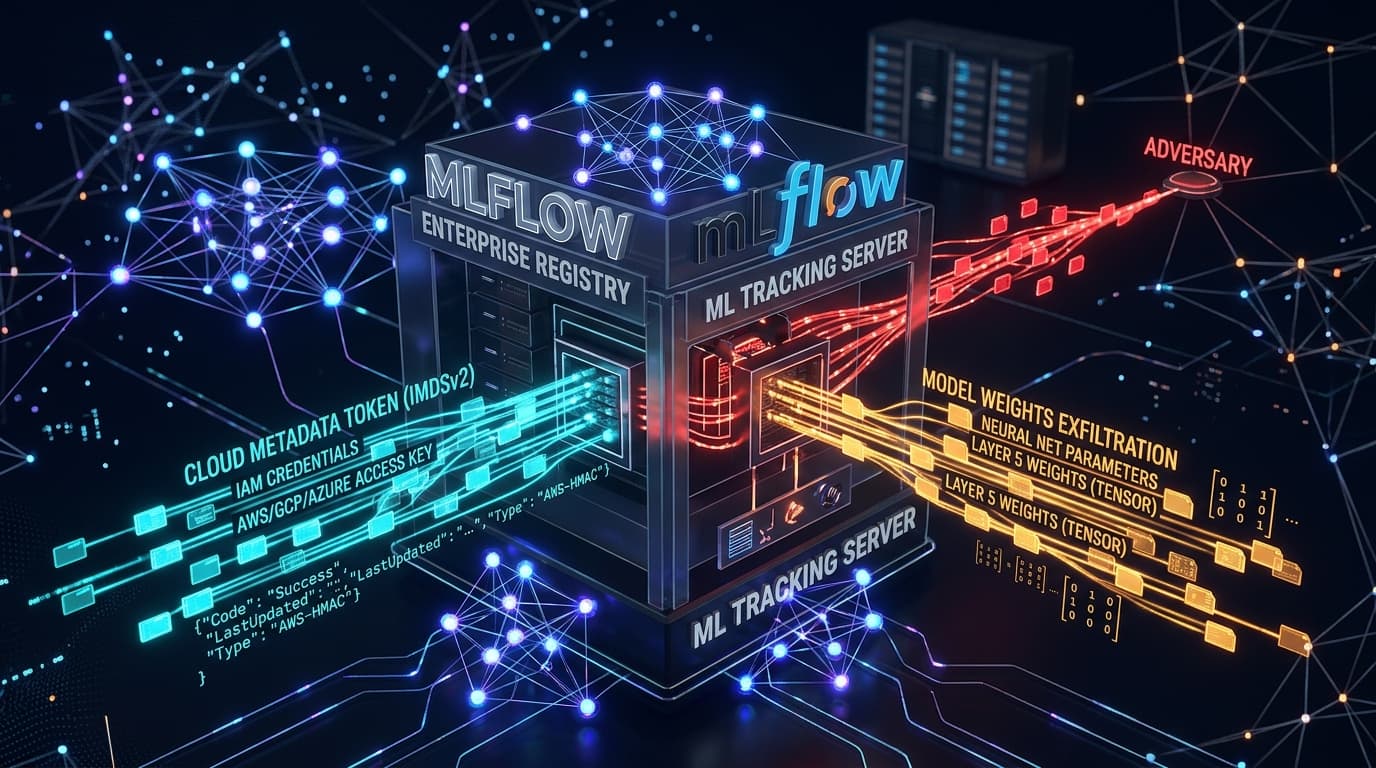
AWS CloudCISA issues urgent warning on CVE-2026-64849, a critical SSRF defect in open-source MLflow model registries allowing attackers to steal cloud IAM metadata and poison AI pipelines.