ThreatsCloud & SaaSHigh
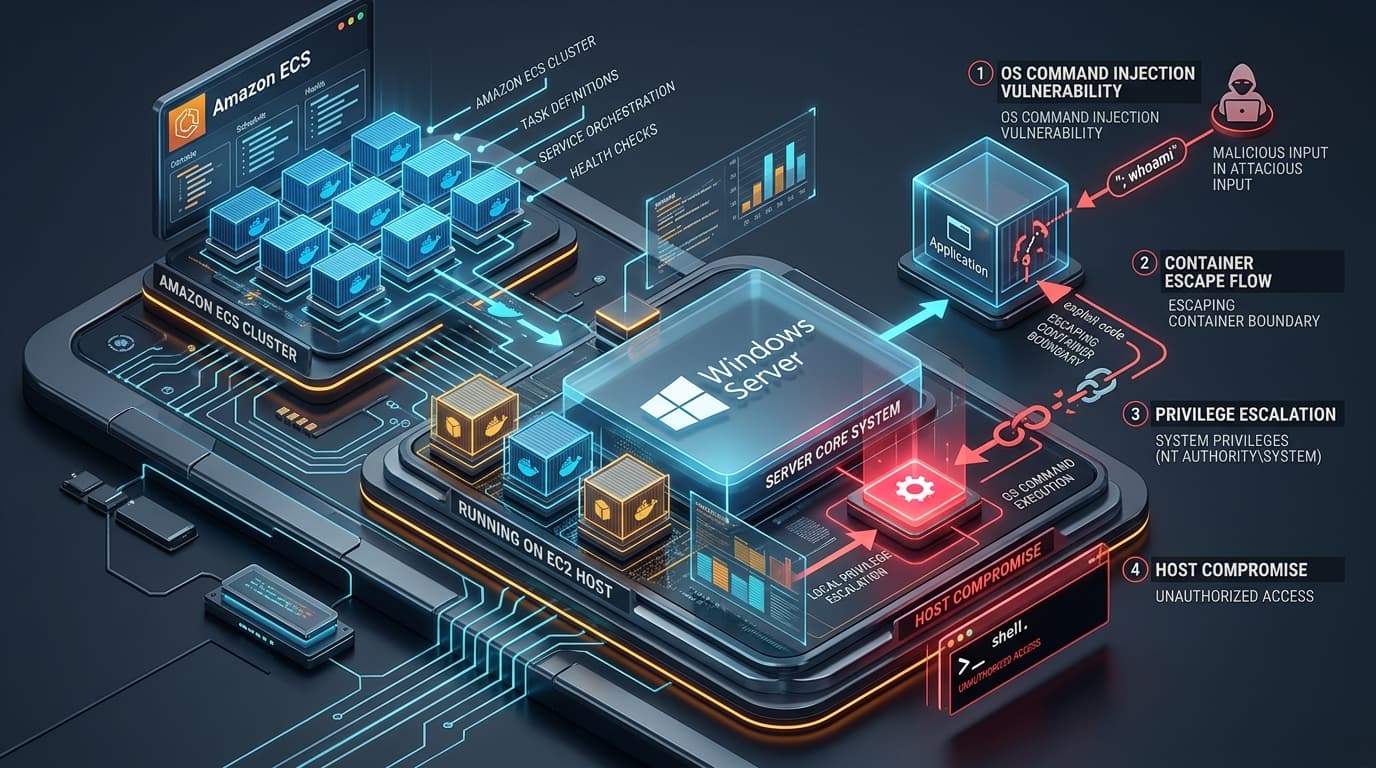
Amazon ECS Container Agent Flaw Enables Task Boundary Breakout and IAM Role Credential Hijacking
Aisha Noor
Topic
2 articles
CyberSecureToday covers Amazon ECS across 2 articles published between 21 Sep 2026 and 25 Sep 2026. The coverage includes 2 vulnerability advisories. 2 advisories are rated critical or high severity.
Stories on Amazon ECS most often intersect with Amazon Web Services, AWS and Container Security, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Amazon ECS Container Agent Flaw Enables Task Boundary Breakout and IAM Role Credential Hijacking”, was published 25 Sep 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.