 Threat Intel
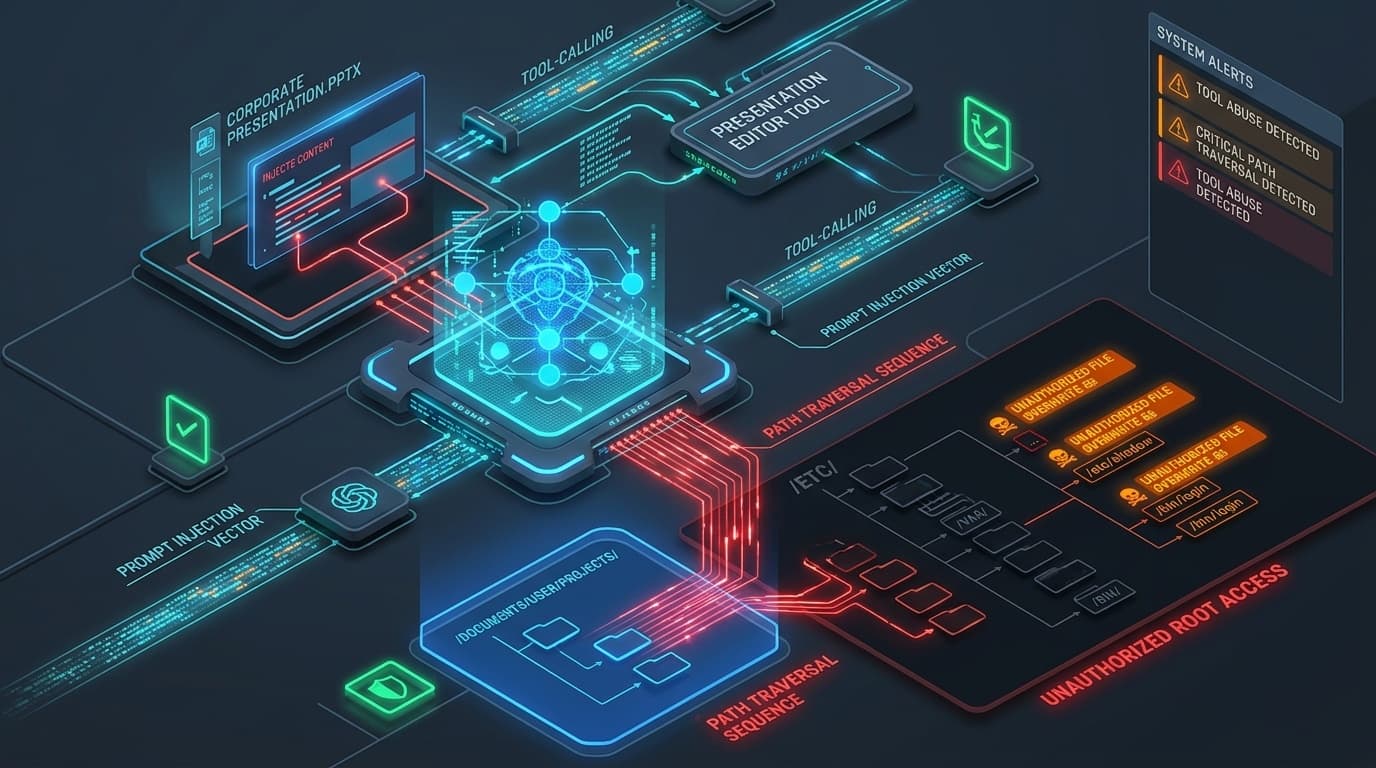
Office PowerPoint MCP Server Path Traversal Enables Indirect Prompt Injection File Overwrite (CVE-2025-71427)
ThreatsCloud & SaaSCVE-2025-71427High
A path traversal vulnerability in the Office-PowerPoint Model Context Protocol server allows AI agents to be manipulated via prompt injection into overwriting host files.
Priya Raman8 min read