A critical pre-authentication memory safety vulnerability has been disclosed in ESnet iperf3, the primary network throughput and bandwidth benchmarking tool utilized across global cloud data centers, carrier transit hubs, and enterprise test labs. Cataloged under CVE-2026-101283 and published in GitHub Security Advisory GHSA-pwcx-5qh6-2pxc with a maximum CVSS v3.1 base score of 9.8 (Critical), the flaw enables unauthenticated remote attackers to trigger a heap buffer overflow in servers configured with RSA client authentication, resulting in process crashes or arbitrary remote code execution.
Cryptographic Authentication in iperf3 Infrastructure
In multi-tenant cloud environments and public speed-test fabrics, administrators secure iperf3 daemons against unauthorized network abuse using cryptographic authentication (--rsa-private-key-path). Under this model, clients must present an encrypted JSON authtoken containing a username, password hash, and timestamp signed with the server's public key before bandwidth measurement streams are allowed to allocate network sockets.
Root Cause Analysis: Flawed Warning-Only Boundary Check (CWE-122)
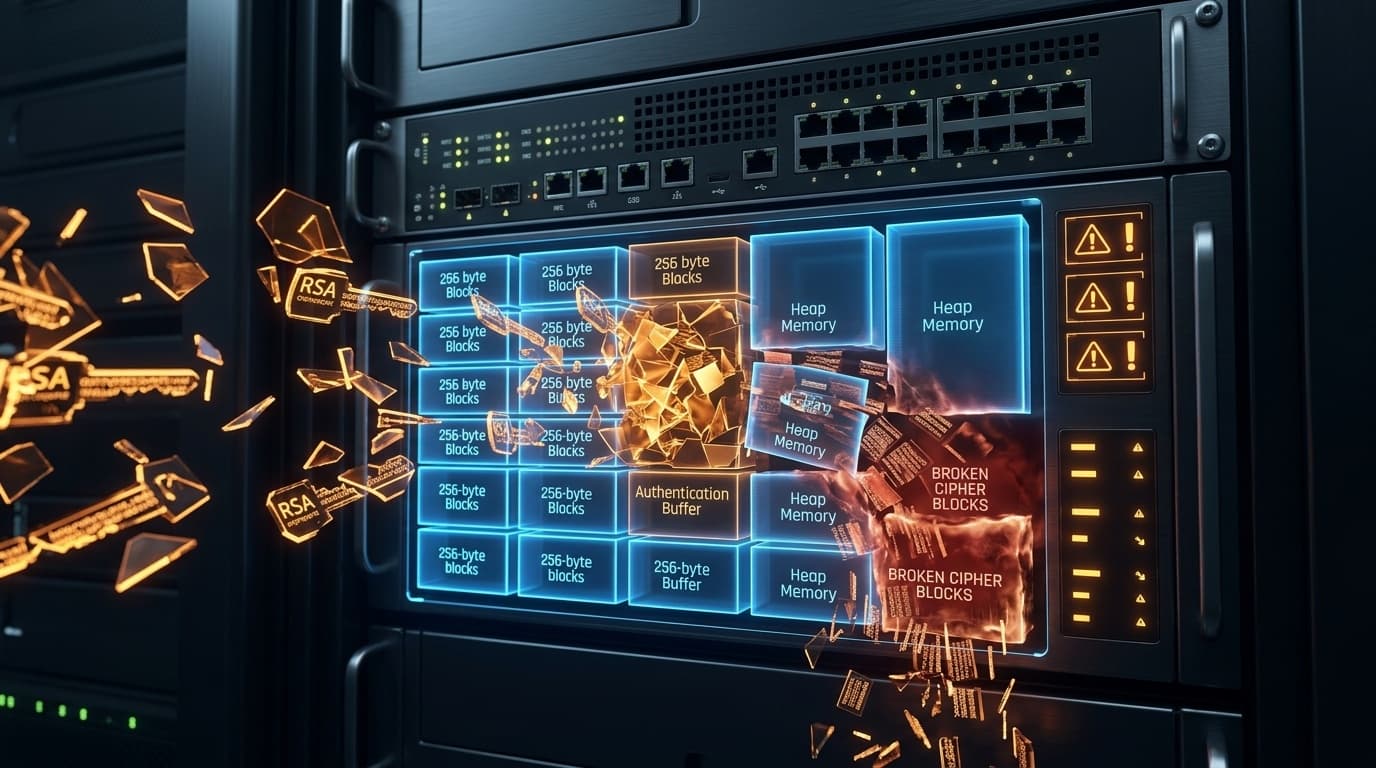
In iperf3 versions 3.20 and 3.21, the incoming authentication token is decrypted in src/iperf_auth.c inside the decrypt_rsa_message() routine. The function allocates a fixed 256-byte buffer on the heap to store the incoming RSA ciphertext:
// Vulnerable Parsing in iperf3 v3.20-3.21 (src/iperf_auth.c)
int decrypt_rsa_message(const char *encrypted_token, int token_len, char **plaintext) {
    char *ciphertext = malloc(256); // Fixed 256-byte allocation

    // Attacker supplies arbitrary token_len in packet header
    if (token_len > 256) {
        warning("token length %d exceeds expected size 256", token_len);
        // FATAL DEFECT: Logs warning but FAILS to return error or abort!
    }

    BIO *bio = BIO_new_mem_buf(encrypted_token, token_len);
    // BIO_read writes attacker-controlled token_len bytes into 256-byte buffer!
    int bytes_read = BIO_read(bio, ciphertext, token_len);

    // Heap overflow occurs directly onto adjacent glibc heap chunks!
}
While the developers recognized that token_len might exceed 256 bytes, the validation block merely logged a diagnostic warning message via warning() and continued execution.
When BIO_read() is invoked with the attacker's oversized length, OpenSSL copies unvalidated ciphertext bytes beyond the bounds of the 256-byte heap chunk. This corrupts adjacent heap chunk metadata, top chunk headers, and neighboring stream pointers.
Heap Layout and Exploit Mechanics
| Heap Offset | Legitimate Data | Attacker Corrupted Payload |
|---|---|---|
+0x000 - +0x0FF |
256-byte RSA Ciphertext Buffer | Shellcode / ROP chain setup data |
+0x100 - +0x108 |
Adjacent Glibc Chunk Size / Flags | Overwritten chunk size with PREV_INUSE cleared |
+0x108 - +0x120 |
Active Stream FD & Function Pointers | Overwritten callback address pointing to injected payload |
Remediation & Defense Actions
- Deploy iperf3 v3.22: Upgrade immediately to version 3.22. The patch enforces strict bounds verification, ensuring any token exceeding 256 bytes immediately terminates the connection with an authentication error code before any reading takes place.
- Disable Unnecessary RSA Authentication if Unused: If the iperf3 server runs in a private, trusted management subnet, disable the
--rsa-private-key-pathparameter until patched binaries are deployed. - Network Layer Firewalls: Restrict TCP port 5201 access to authenticated IP addresses via host firewalls (
nftables/iptables) or AWS Security Groups.