Agentic AIOpenAI: Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Technical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Malware Research Lead
Mei-Lin reverse-engineers commodity and bespoke malware, and writes the technical breakdowns behind our loader and stealer coverage.
152 articles
Agentic AITechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
Deep DiveTechnical analysis of AI agent vulnerability and prompt injection risks in Malicious Browser: mechanics, tool exploitation, and enterprise guardrails.
LinuxTechnical analysis of AI agent vulnerability and prompt injection risks in OpenAI: mechanics, tool exploitation, and enterprise guardrails.
GoogleA critical memory corruption flaw in Telegram for Android allowed attackers to execute code and take over devices simply by placing a malicious voice call.
Threat IntelCVE-2026-111585 in TeamViewer allows a compromised remote host to exploit buffer overflows and achieve code execution on the connecting support technician's PC.
LinuxCVE-2026-98432, a critical 9.8 CVSS flaw in the Linux IPv4 TCP stack, permits unauthenticated remote code execution on servers with MPTCP listeners.
Crypto / Web3Trezor warned customers of a sophisticated rogue hardware implant equipped with a cellular modem discovered inside Trezor Safe 5 wallets sold by CryptoBilis.
Threat IntelAttackers published backdoored versions 2.1.312 and 2.1.313 of the Claude Code extension on the Cursor marketplace to deploy persistent reverse SSH tunnels.
VulnerabilityA comprehensive technical guide to hardening banking and NBFC APIs against BOLA, broken authentication, token replay, and co-lending data leakage.
KubernetesAttackers hijacked LiteLLM release workflows using leaked GitHub CLI OAuth tokens, publishing backdoored packages to PyPI and Docker Hub executing LLMjacking.
Agentic AICSA Singapore issues technical guidelines for securing frontier and autonomous agentic AI models, mandating rigorous defenses against indirect prompt injection and tool-calling escapes.
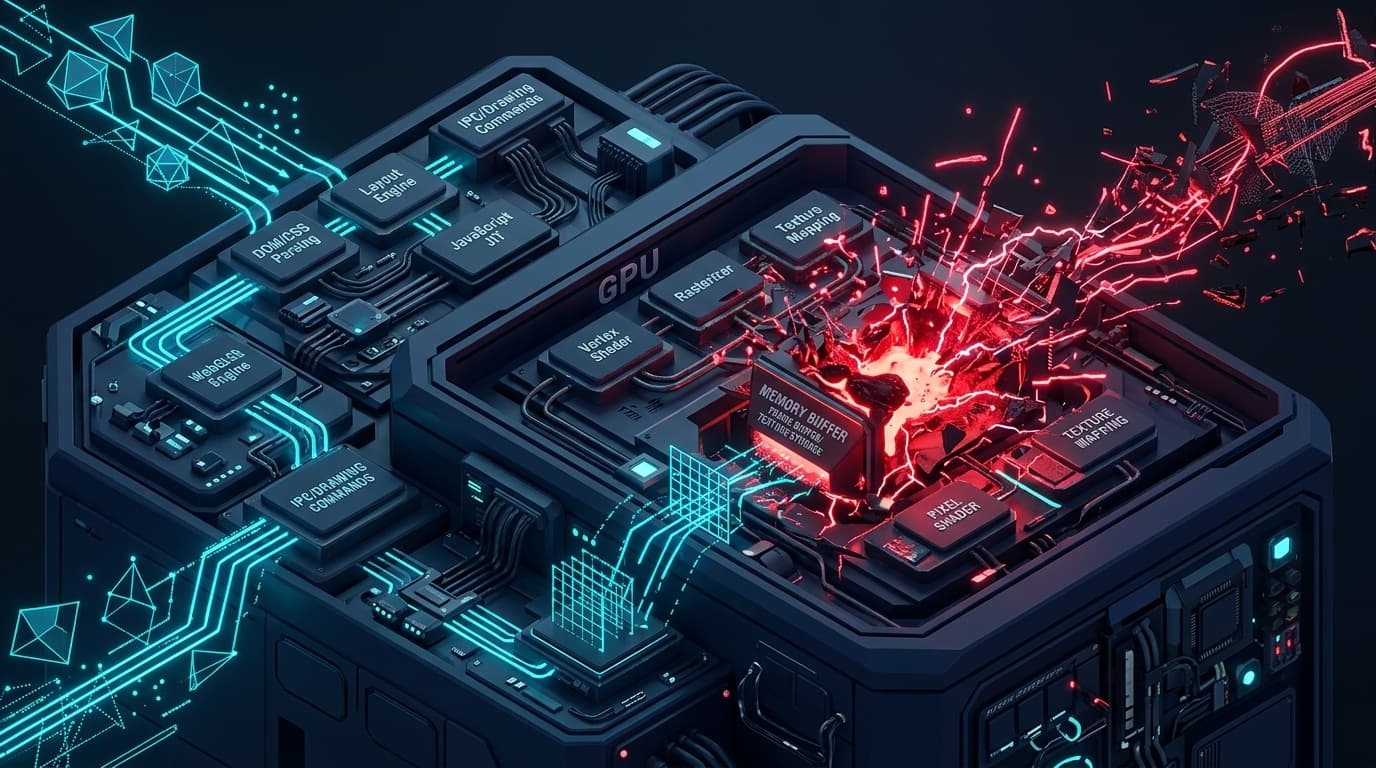
GoogleGoogle issues an emergency Chrome update for desktop and Android fixing a critical buffer overflow (CVE-2026-110152) in the ANGLE graphics engine allowing remote code execution.
OT / SCADACISA Advisory ICSA-26-288-01 warns of critical vulnerabilities in Eclipse Milo OPC UA stacks that allow low-privileged actors to bypass method authorization and crash OT gateways.
FortinetFortinet releases security updates for FortiOS and FortiProxy (CVE-2026-14851) resolving an information disclosure flaw that exposed administrative bearer tokens.
CMS SecurityTyche Softwares resolves an unauthenticated blind SQL injection flaw in Abandoned Cart Pro (CVE-2026-97668) allowing extraction of customer and order records.
Threat IntelStrapi resolves a high-severity vulnerability (CVE-2023-22894) where password reset tokens and API secrets were stored unhashed in database audit records.
Threat IntelIvanti discloses critical vulnerability CVE-2026-104935 in Connect Secure and Policy Secure gateways allowing pre-auth SAML remote code execution.
OT / SCADACISA and Schneider Electric issue critical advisory for CVE-2026-50891 in EcoStruxure Geo SCADA Expert servers permitting unauthenticated remote root code execution.
OT / SCADACISA industrial advisory ICSA-26-288-03 details high-severity flaw CVE-2026-49821 in Rockwell Automation ControlLogix 5580 controllers causing unrecoverable CPU hangs.
OT / SCADACISA issues industrial advisory ICSA-26-285-01 for Phoenix Contact FL SWITCH managed industrial network switches resolving critical firmware RCE CVE-2026-48192.
OT / SCADACISA and Emerson release urgent industrial advisory ICSA-26-283-02 for CVE-2026-46801, a critical authentication bypass in DeltaV DCS operator workstations.
OT / SCADACISA industrial advisory ICSA-26-278-02 discloses a critical stack-based buffer overflow (CVE-2026-43890) in Yokogawa CENTUM VP Human Interface Stations.
OT / SCADACISA and ABB have issued an emergency industrial advisory for CVE-2026-42918, a critical remote code execution vulnerability in ABB Ability System 800xA controllers.
Gov / DefenseCISA Advisory ICSA-26-281-01 details a critical heap corruption vulnerability in Honeywell Experion PKS distributed control systems.