The Cybersecurity and Infrastructure Security Agency (CISA) and industrial automation manufacturer Schneider Electric have published a critical security notification (ICSA-26-289-01) warning of a maximum-severity heap buffer overflow vulnerability (CVE-2026-50891, CVSS 9.8) in Schneider Electric EcoStruxure Geo SCADA Expert (formerly ClearSCADA). The defect allows unauthenticated remote adversaries over the network to execute arbitrary code with highest operating system privileges on central SCADA telemetry servers governing drinking water utilities, municipal wastewater systems, and gas pipelines.
Root Cause: ClearSCADA Database Protocol Heap Corruption (CWE-122)
Schneider Electric EcoStruxure Geo SCADA Expert provides supervisory monitoring across geographically dispersed critical assets. Central database servers synchronize telemetry with remote terminal units (RTUs), flow computers, and operator clients via the proprietary ClearSCADA database communications service listening on TCP port 5481.
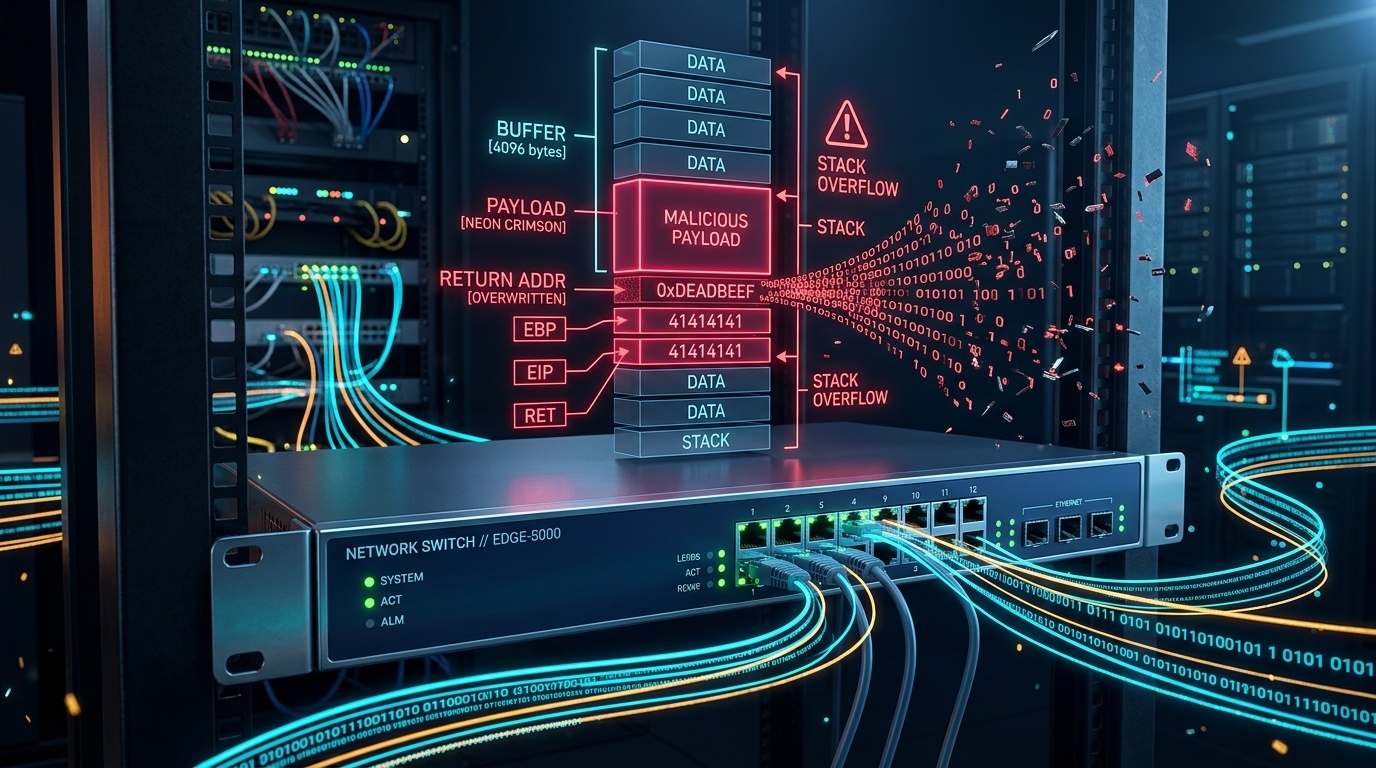
According to Schneider Electric's security bulletin, a flaw exists in the protocol frame parser when unpacking serialized database record modification requests. When a client submits an SQL-like telemetry update containing an oversized field description header, the service miscalculates allocation sizing on the system heap:
// Disassembly representation of vulnerable ClearSCADA frame deserializer
int ProcessDatabaseRecordUpdate(uint8_t* frame_data, size_t frame_len) {
    uint32_t header_len = *(uint32_t*)(frame_data);
    // Integer truncation defect: casting 32-bit length to 16-bit integer
    uint16_t alloc_bytes = (uint16_t)header_len;
    char* heap_buffer = (char*)malloc(alloc_bytes); // Undersized buffer allocated

    // Unbounded copy overflows heap slab into adjacent C++ vtable pointers
    memcpy(heap_buffer, frame_data + 4, header_len);
    return DispatchRecordToDatabase(heap_buffer);
}
By spraying the heap with deterministic memory allocations, an unauthenticated attacker can overwrite C++ virtual method table (vtable) pointers, hijacking control flow to execute arbitrary payload code in the security context of NT AUTHORITY\SYSTEM.
Physical Infrastructure Hazards and Water Sector Exposure
In municipal drinking water and wastewater treatment facilities, compromising the central Geo SCADA server yields unrestricted operational control:
- Chemical Dosing Overrides: Attackers can alter sodium hypochlorite (chlorine) or sodium hydroxide dosing levels, creating toxic chemical conditions in public water distribution networks.
- Pump Station Blackouts: Disabling sewage lift station telemetry causes untracked pipeline overflows and environmental contamination.
- Safety Alarm Suppression: Silencing critical pressure and tank level alarms prevents automated fail-safe valves from tripping during catastrophic pump failures.
Remediation Playbook for Utility Operators
- Install Official Hotfix: Immediately apply Schneider Electric patch package SEVD-2026-281-01 for EcoStruxure Geo SCADA Expert 2021 and 2023 versions.
- Enforce Port 5481 Boundary Filtering: Restrict network ingress to TCP port 5481 strictly to authorized SCADA engineering workstations and client consoles using network firewalls.
- Isolate SCADA Telemetry Conduits: Disconnect Geo SCADA servers from internet-routable IT segments, enforcing strict Purdue Model Level 3 DMZ boundary controls.