Operational Context: Industrial Serial Bridges Under Critical Threat
The Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2025-67038 to its Known Exploited Vulnerabilities (KEV) catalog, ordering critical infrastructure operators to patch high-risk code injection vulnerabilities affecting Lantronix EDS5000 hybrid enterprise device servers.
Lantronix EDS5000 servers serve as mission-critical protocol bridges in operational technology (OT) environments, connecting legacy serial devices (RS-232, RS-422, RS-485) to modern TCP/IP networks. Deployed in electric power transmission substations, automated manufacturing cells, municipal water pump stations, and oil refining facilities, these appliances transport sensitive SCADA protocols including Modbus RTU, DNP3, and IEC 60870-5-101. A compromise of the device server gives adversaries direct control over physical field equipment.
Vulnerability Mechanics & Embedded Code Injection (CWE-94)
The flaw resides in the embedded web management daemon and telnet configuration interface:
- Inadequate Input Boundary Checking: Configuration parameters supplied during unauthenticated administrative requests are parsed without proper length validation or character escaping.
- Firmware Memory Corruption: An attacker transmitting crafted binary strings to the web server triggers a stack-based buffer overwrite that redirects instruction execution to shellcode injected within the payload.
- Interception of Industrial Data Streams: Once compromised, the adversary gains root firmware access, enabling real-time tampering with serial data buffers. Threat actors can alter breaker trip commands, fabricate false sensor readings sent to supervisory SCADA consoles, and inject unauthorized actuator instructions.
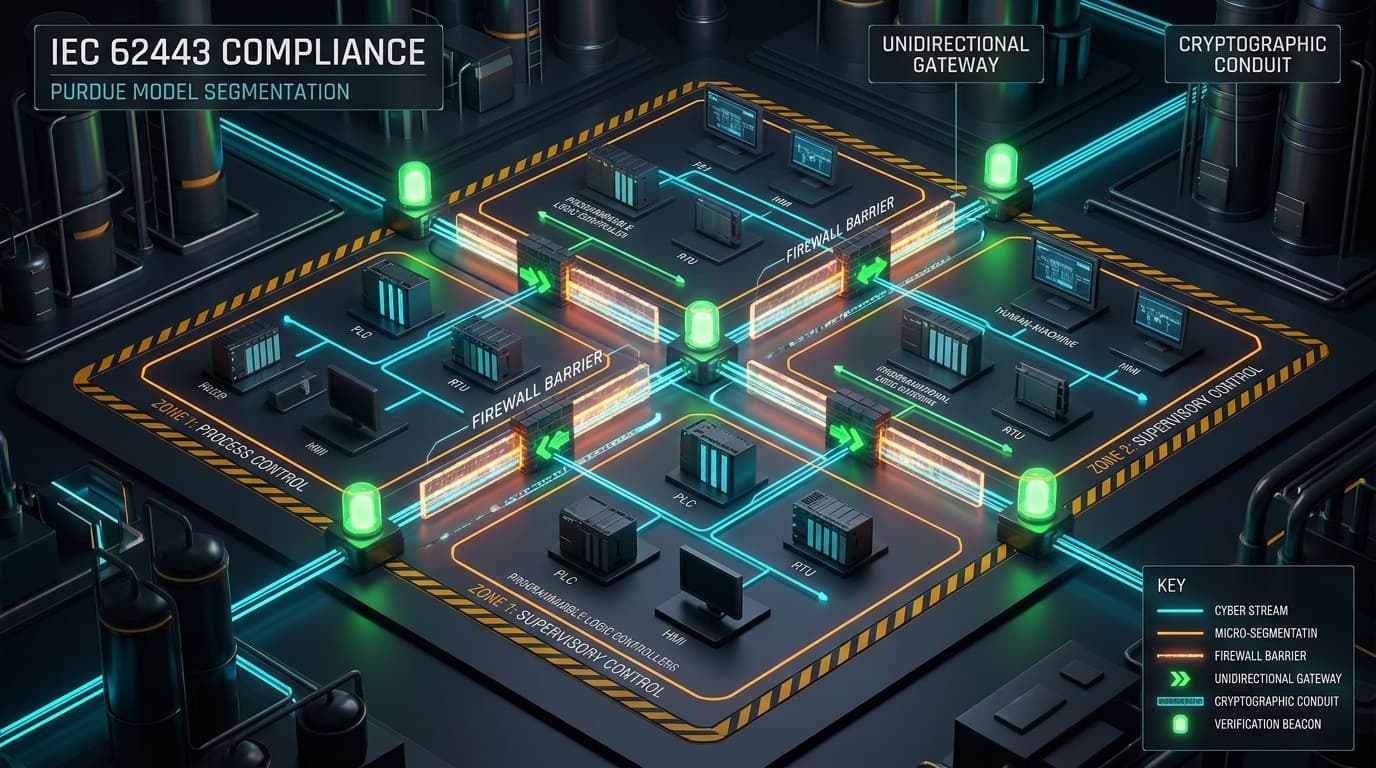
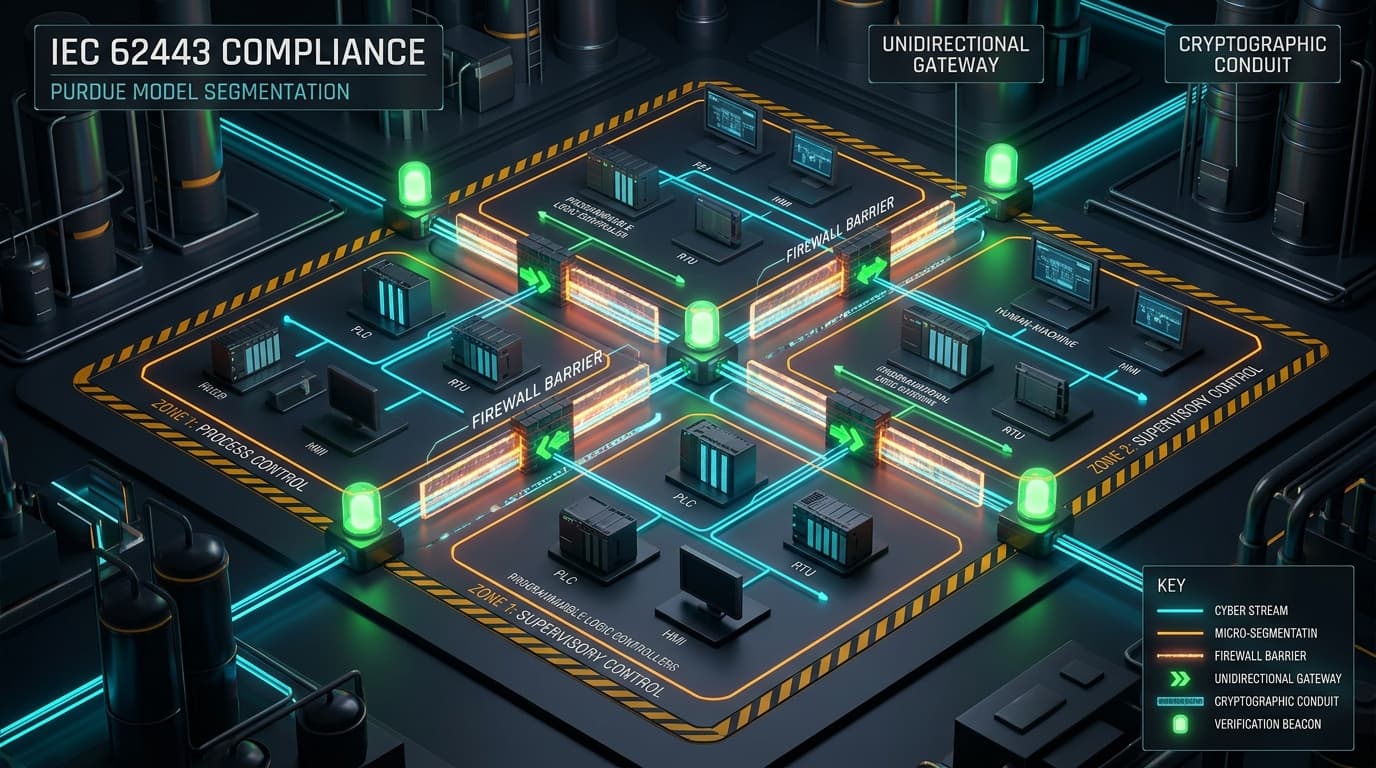
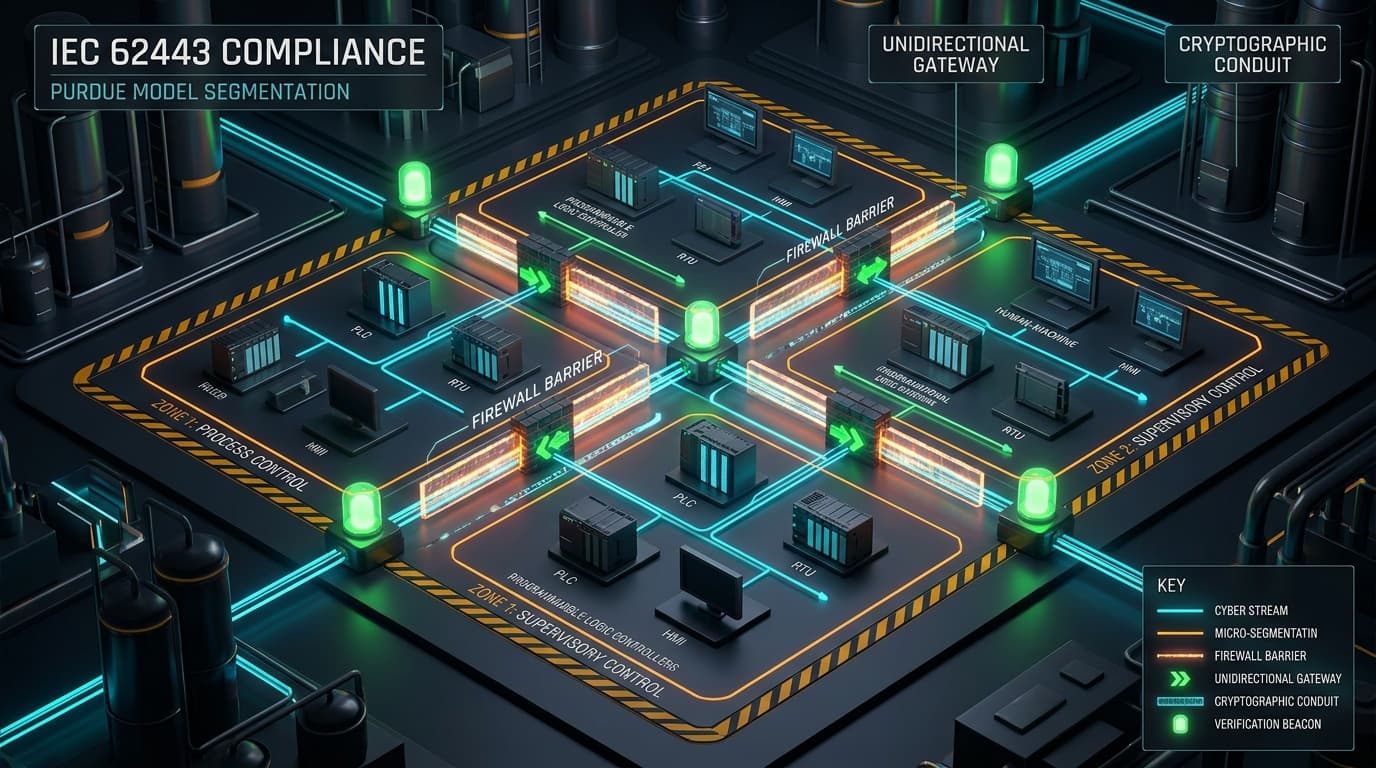
IEC 62443 Industrial Architecture Impact
| Purdue Level | Component Impacted | Operational Consequence |
|---|---|---|
| Level 1 (Field Devices) | RTUs, PLCs, Protective Relays | Injection of unauthorized serial trip signals; potential equipment damage. |
| Conduit (Level 1 to Level 2) | Lantronix EDS5000 Gateway | Loss of communication encryption and packet integrity across zone boundaries. |
| Level 2 (Supervisory SCADA) | Human Machine Interface (HMI) | Telemetry spoofing masking physical infrastructure anomalies. |
Remediation Directives for OT Engineers
- Apply Latest Firmware: Upgrade Lantronix EDS5000 units to vendor-approved firmware builds that implement boundary checks.
- Isolate to Purdue Level 1 VLANs: Ensure device servers are strictly isolated on dedicated OT subnets with no direct routes to enterprise corporate IT or external networks.
- Disable Insecure Protocols: Deactivate cleartext Telnet and HTTP web interfaces; enforce SSHv2 and HTTPS with strong cryptographic keys.