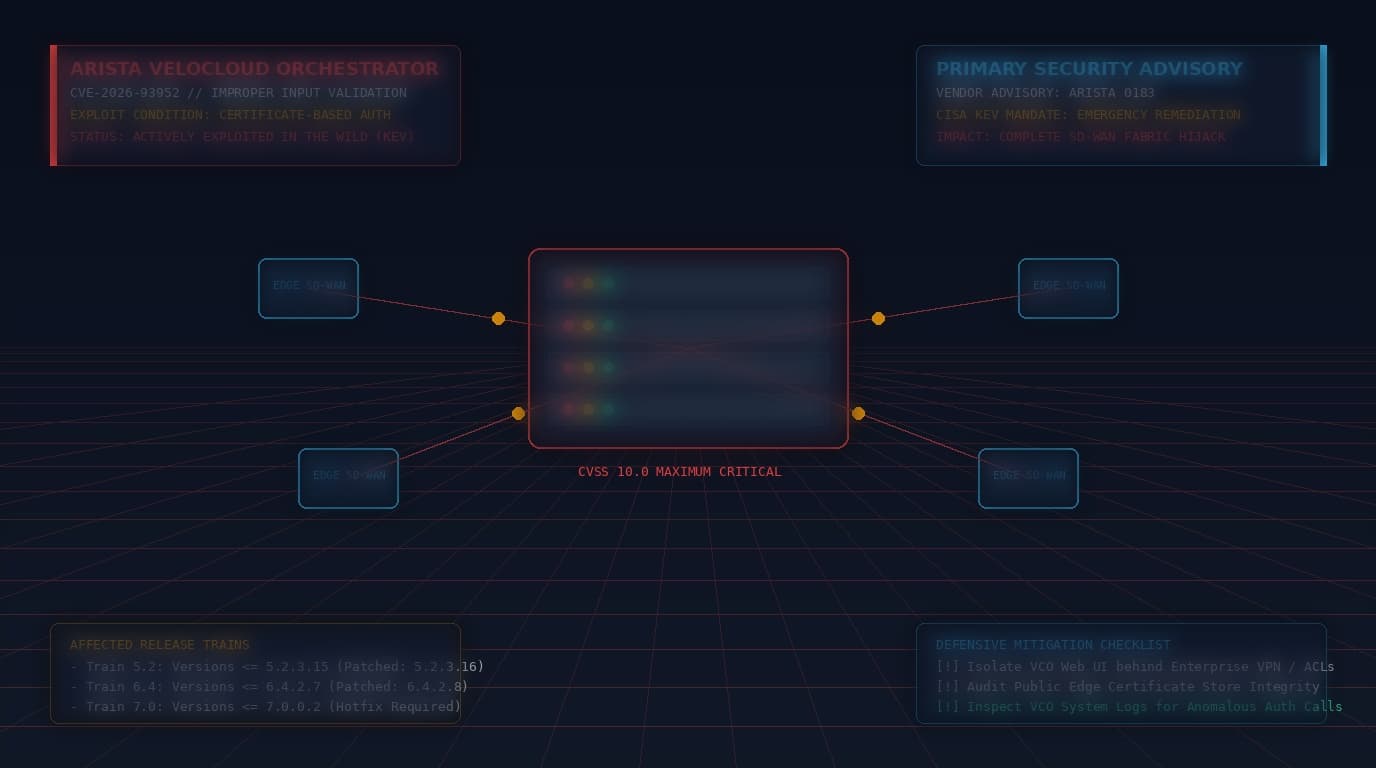
Active ExploitArista VeloCloud Orchestrator Zero-Day Exploited to Hijack SD-WAN Edge Gateways
Arista confirms active in-the-wild exploitation of CVSS 10.0 CVE-2026-93952, allowing unauthenticated attackers to hijack on-prem VeloCloud Orchestrators.
Topic
1 article
CyberSecureToday covers VCO in a story published 23 Sep 2026.
The coverage includes 1 vulnerability advisory. 1 advisory is rated critical or high severity, and 1 involves a flaw listed in CISA's Known Exploited Vulnerabilities catalog.
Stories on VCO most often intersect with Arista, VeloCloud and SD-WAN, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Arista VeloCloud Orchestrator Zero-Day Exploited to Hijack SD-WAN Edge Gateways”, was published 23 Sep 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.
Active ExploitArista confirms active in-the-wild exploitation of CVSS 10.0 CVE-2026-93952, allowing unauthenticated attackers to hijack on-prem VeloCloud Orchestrators.