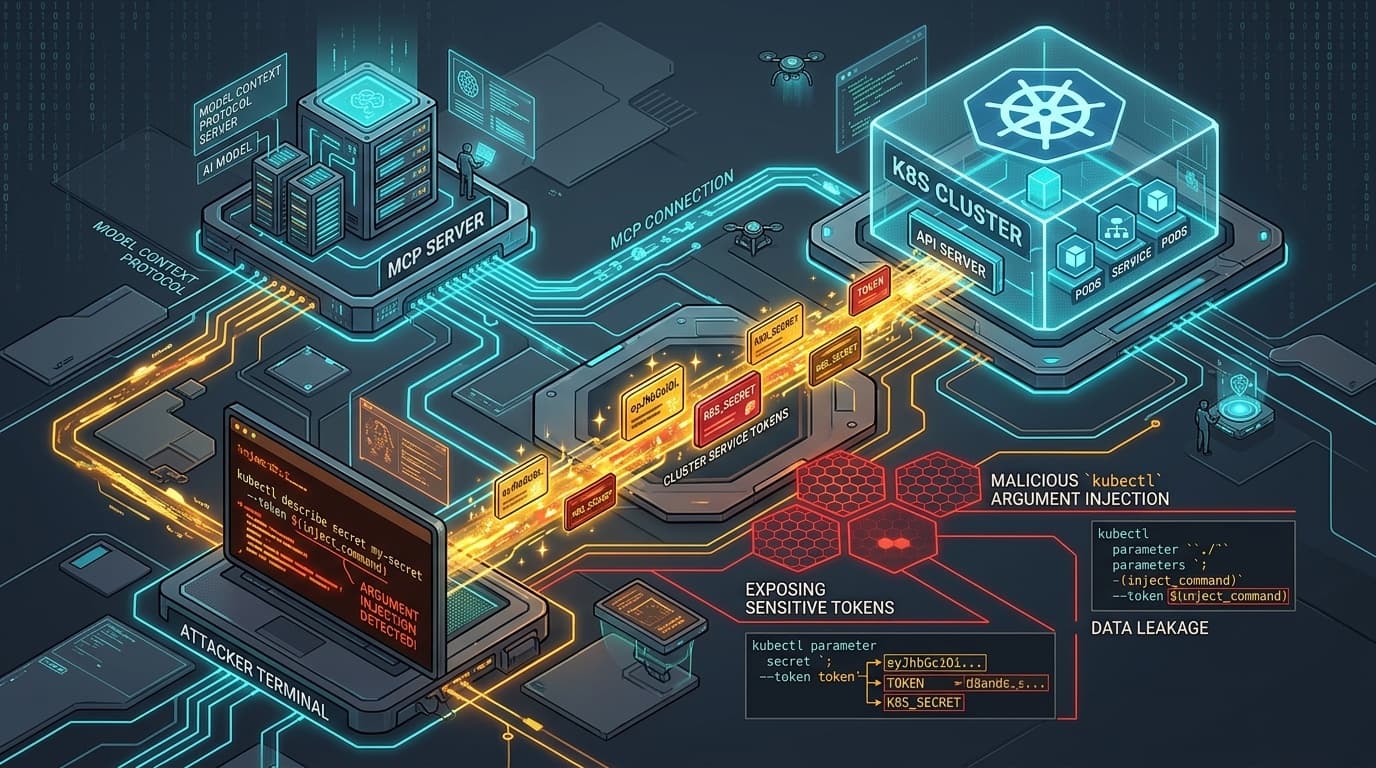
Threats·Cloud & SaaSBreakingKubernetes MCP Server Structured Tool Argument Injection Exposes Cluster Service Credentials (CVE-2026-61459)A critical flaw in Model Context Protocol (MCP) Kubernetes bridge servers allows attackers to inject malicious flags into kubectl tool calls, exposing cluster service tokens.CST Newsroom30 Sep 202611 min read