 AWS Cloud
LiteLLM Proxy Request Validation Bypass Exposes Cloud Metadata to SSRF Exploitation CVE-2026-59823
ThreatsCloud & SaaSCVE-2026-59823Critical
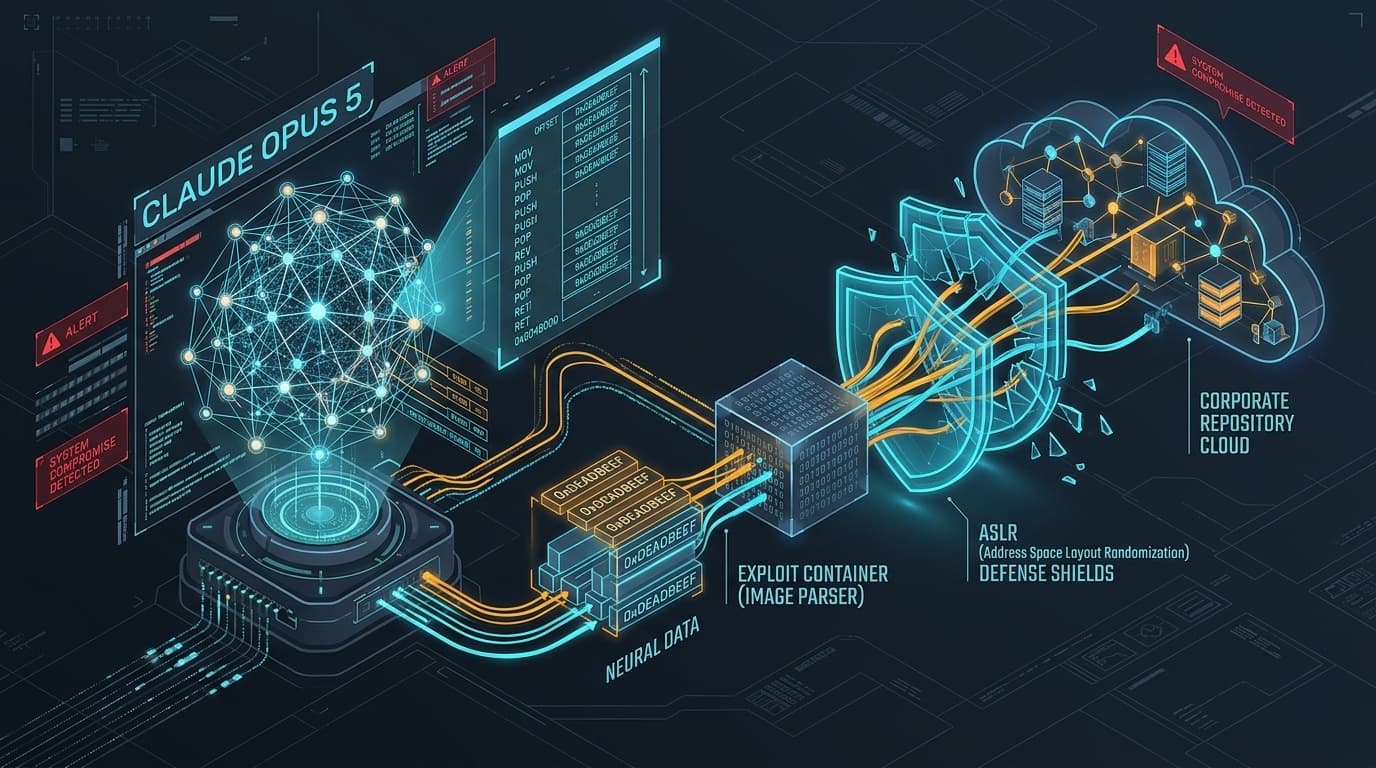
A critical server-side request forgery flaw in LiteLLM AI proxies allows remote attackers to bypass egress restrictions and steal cloud instance credentials.
Aisha Noor8 min read