The Linux kernel development team and major enterprise distributions have mobilized to patch a critical memory safety vulnerability in the core IPv4 networking stack. Designated as CVE-2026-98432 with a CVSS v3.1 base score of 9.8 (Critical), the flaw enables an unauthenticated remote attacker on the network to trigger a use-after-free (UAF) condition during TCP connection establishment, leading to system crashes or arbitrary remote code execution with root kernel privileges.
The disclosure sparked heightened urgency across the cybersecurity landscape after AI safety and frontier research firm Anthropic revealed that an advanced AI model had autonomously synthesized a functioning, weaponized remote code execution exploit targeting the flaw on systems hosting Multipath TCP (MPTCP) sockets.
Root Cause Analysis: Concurrent TCP Option Destruction
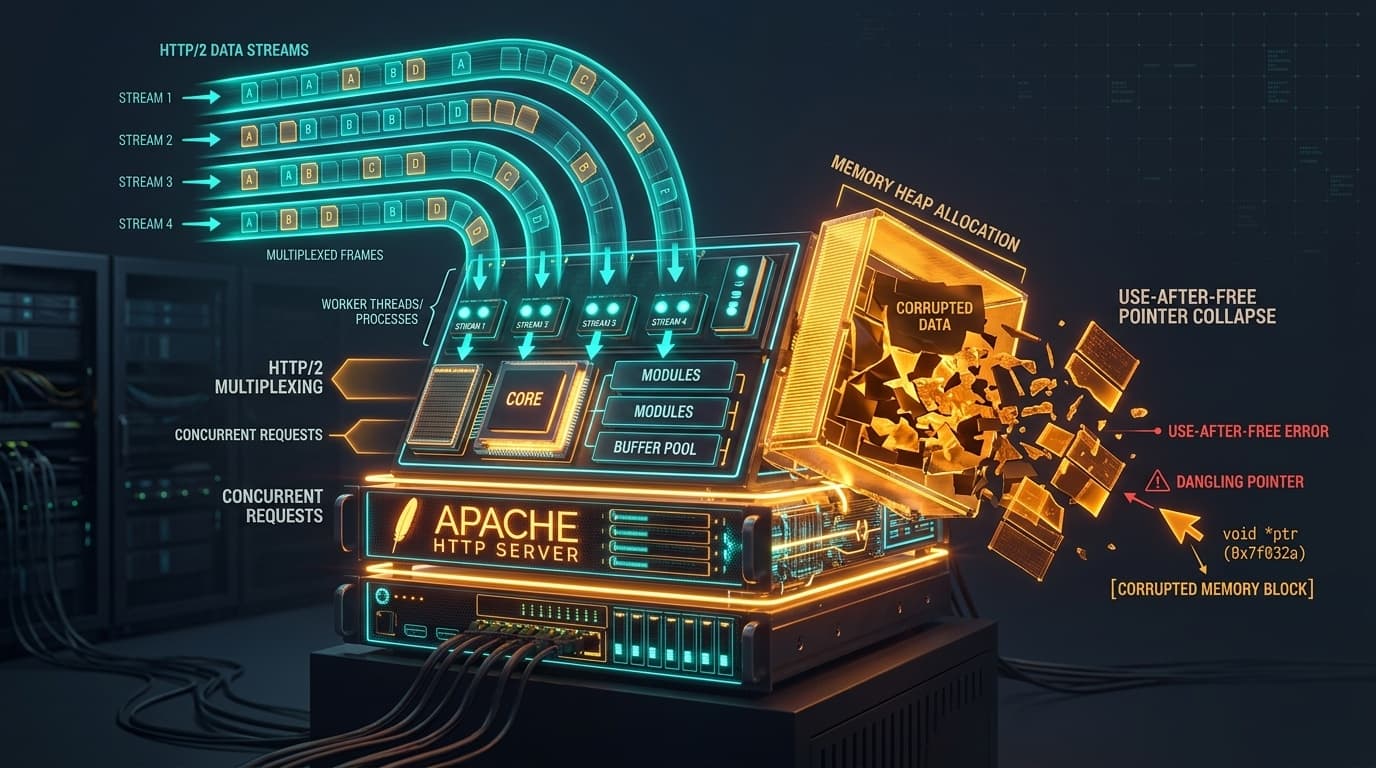
The vulnerability dates back to code patterns introduced in Linux kernel 4.4 in 2016. When an incoming IPv4 TCP connection request (SYN packet) is received with IP options enabled, the networking subsystem allocates memory to hold options structures (inet_opt and ireq_opt) associated with the nascent request socket.
Under specific race conditions—such as rapid retransmissions, socket migration between CPU cores, or simultaneous connection resets—one thread can close and free the socket options while another CPU core is concurrently constructing a response packet (such as a SYN-ACK) using that exact memory buffer.
// Conceptual representation of the race condition in net/ipv4/tcp_input.c:
// Thread A: Processing retransmitted reset / teardown
tcp_v4_destroy_sock(sk) -> kfree(inet_opt); // Memory freed immediately!

// Thread B: Running concurrently on secondary core building SYN-ACK
build_syn_ack_packet(req) {
    memcpy(packet_buffer, ireq_opt->opt, len); // USE-AFTER-FREE READ/WRITE!
}
Because the memory was freed immediately without awaiting an active Read-Copy Update (RCU) grace period, an attacker who deliberately flood-orchestrates precise packet timing can cause the kernel to execute instructions pointing to attacker-controlled memory structures.
Anthropic's Autonomous Exploit Generation
While winning microsecond-scale kernel race conditions over a wide-area network has traditionally presented steep barriers to reliable weaponization, Anthropic demonstrated that autonomous reasoning models can analyze memory allocation maps and network packet timing to produce high-reliability exploit chains.
The demonstrated exploit targeted the Linux kernel's Multipath TCP (MPTCP) implementation. By interleaving MPTCP subflow establishment packets with crafted TCP options, the exploit manipulated the kernel heap (slab allocator) to achieve predictable memory layout positioning, culminating in remote root code execution without requiring local account access or user interaction.
Affected Version Matrix
| Distribution / Kernel Branch | Vulnerable Versions | Remediation / Patched Kernel |
|---|---|---|
| Mainline Linux Kernel | Linux 4.4 through 6.12.x | Patched via kfree_rcu(inet_opt) |
| Ubuntu LTS | 24.04 LTS, 22.04 LTS (unpatched kernels) | linux-image-*-generic updates deployed |
| Red Hat Enterprise Linux (RHEL) | RHEL 8, RHEL 9 (kernel < 5.14.0-503) | RHSA-2026:98432 advisory updates |
| Debian GNU/Linux | Debian 12 (Bookworm), Debian 11 (Bullseye) | DSA-2026-98432 security releases |
| Amazon Linux 2023 | Kernel builds prior to 6.1.115-126 | AL2023 Security Advisory update |
Remediation Playbook
Enterprise infrastructure engineers must prioritize kernel updates across all internet-facing servers, container host nodes, and load balancers:
# Debian / Ubuntu Systems: Update kernel packages and reboot
sudo apt-get update && sudo apt-get dist-upgrade -y
sudo reboot

# RHEL / AlmaLinux / Rocky Linux:
sudo dnf upgrade kernel -y
sudo reboot

# Verify active kernel post-reboot
uname -r
For high-availability clusters where immediate reboots must be staged, administrators can temporarily mitigate the MPTCP remote vector by disabling MPTCP via sysctl if it is not required for application traffic:
# Temporary mitigation: Disable MPTCP subsystem
sudo sysctl -w net.mptcp.enabled=0
echo "net.mptcp.enabled=0" | sudo tee -a /etc/sysctl.d/99-disable-mptcp.conf