Executive Summary: Core Web Server Daemon Vulnerable to HTTP/2 Heap Collapse
The Apache Software Foundation has released an emergency security update addressing a critical memory safety flaw in the Apache HTTP Server (httpd). Cataloged as CVE-2026-57941 and assigned a maximum severity rating of CVSS 9.8 (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H), the vulnerability impacts all releases of the web server from 2.4.0 through 2.4.68 when running the mod_http2 module.
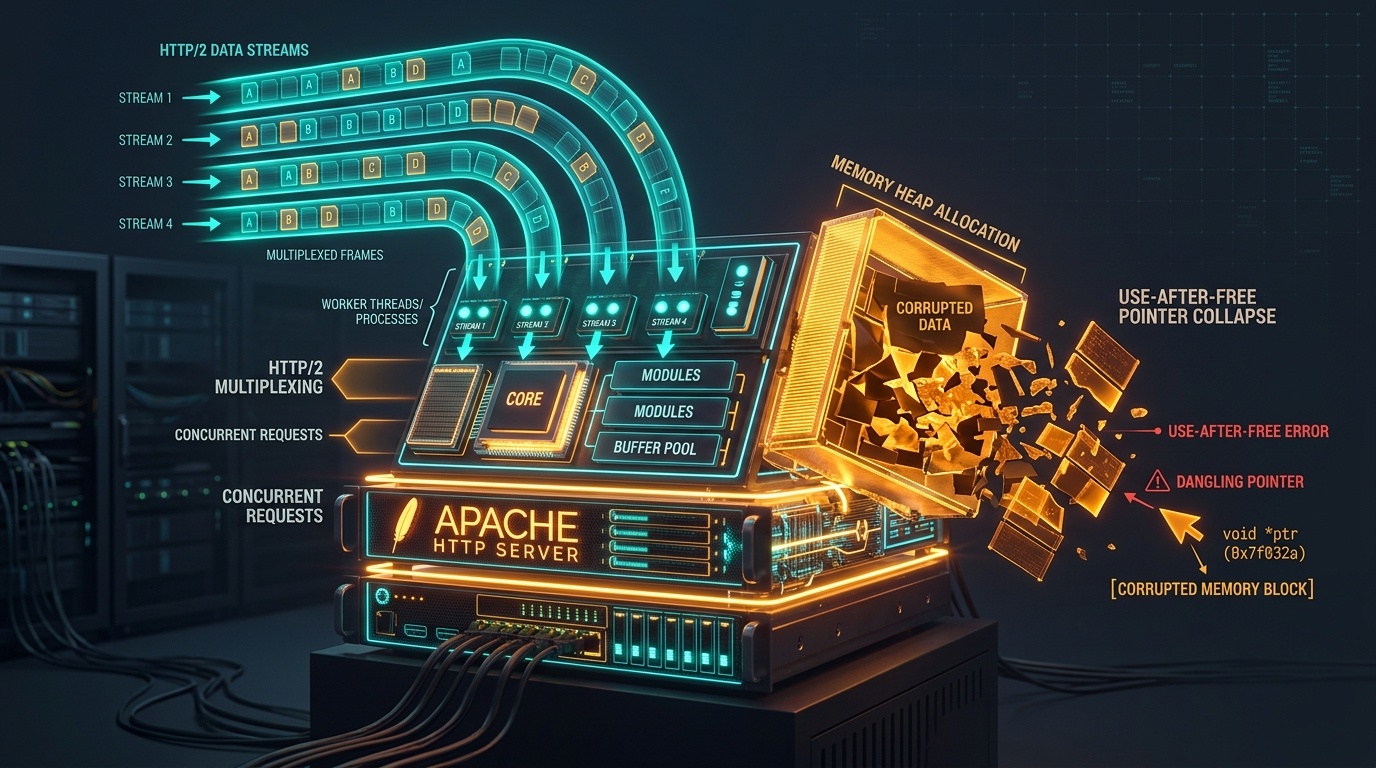
The flaw is categorized as a Use-After-Free (CWE-416) caused by race-condition-induced re-entrancy inside the HTTP/2 session bucket brigade management logic. Unauthenticated network attackers can send interleaved HTTP/2 frames across concurrent multiplexed streams to trigger the destruction of memory pools while active worker threads are referencing bucket descriptors. This enables remote attackers to execute arbitrary code within the privileges of the web server worker process (www-data or apache) or launch continuous denial-of-service (DoS) crashes against high-traffic web properties.
Root Cause Mechanics: Re-entrancy in session->bbtmp
In the Apache HTTP Server architecture, memory and data chunk transfers between network filters and content handlers are abstracted using APR (Apache Portable Runtime) bucket brigades (apr_bucket_brigade). To optimize performance under high HTTP/2 multiplexing concurrency, mod_http2 maintained a shared temporary bucket brigade structure attached to the overarching session: session->bbtmp.
When processing complex streams involving server pushes, early frame chunking, or sudden connection resets, mod_http2 failed to guard against re-entrant calls into the brigade recycling pipeline:
// Vulnerability flow in h2_session.c (prior to 2.4.69):
static apr_status_t h2_session_read(h2_session *session, apr_read_type_e block)
{
    // session->bbtmp is a shared scratch brigade across all active multiplexed streams:
    apr_bucket_brigade *bbtmp = session->bbtmp;

    // Worker thread starts populating bbtmp with incoming DATA frames:
    status = apr_brigade_partition(bbtmp, point, &bucket);

    // Concurrently, an adversarial RST_STREAM or GOAWAY frame triggers cleanup:
    if (session_interrupted(session)) {
        // Stream teardown releases and clears the bucket pool:
        apr_brigade_cleanup(session->bbtmp); // Memory freed!
    }

    // Execution resumes in the worker thread with a dangling pointer:
    APR_BRIGADE_INSERT_TAIL(bbtmp, bucket); // Use-After-Free: write to freed memory block
}
By strategically interleaving rapid RST_STREAM frames immediately following large payload chunks, an attacker can manipulate heap layout so that freed bucket memory is reallocated with attacker-controlled bytes before the dangling write occurs. This grants a reliable write-what-where primitive on 64-bit Linux server architectures.
Vulnerability Scope & Exposure Analysis
The HTTP/2 protocol is enabled by default in modern Apache HTTP Server deployments powering content delivery networks (CDNs), enterprise APIs, and web application hosting environments:
| Configuration State | Vulnerability Exposure | Mitigation Feasibility |
|---|---|---|
| Protocols h2 h2c http/1.1 | Vulnerable (High) | Update to 2.4.69 immediately or disable h2 / h2c protocols. |
| Protocols http/1.1 only | Immune (Safe) | mod_http2 logic is bypassed entirely; no exposure. |
| Reverse Proxy fronted by Nginx / Cloudflare | Protected (Moderate) | If edge proxy terminates HTTP/2 and connects via HTTP/1.1 upstream, backend is protected. |
Defensive Remediation Playbook
- Upgrade to Apache HTTP Server 2.4.69: Deploy version 2.4.69 immediately. The release eliminates the shared
session->bbtmpbucket brigade, replacing it with thread-isolated per-stream allocation contexts that prevent cross-stream lifecycle race conditions. - Emergency Protocol Mitigation: If upgrading cannot be performed immediately, disable HTTP/2 support across virtual hosts by modifying the
Protocolsdirective inhttpd.conf:# In httpd.conf or ssl.conf: # Replace: # Protocols h2 http/1.1 # With: Protocols http/1.1 - Restart the Web Server: Reload the Apache service to ensure active memory structures are purged:
sudo apachectl configtest
sudo systemctl restart apache2 # or httpd