Topic

mod_http2: news, advisories and analysis

1 articleUpdated

CyberSecureToday covers mod_http2 in a story published 2 Oct 2026.

  • 1 advisory
  • 1 critical or high
About this topic

The coverage includes 1 vulnerability advisory. 1 advisory is rated critical or high severity.

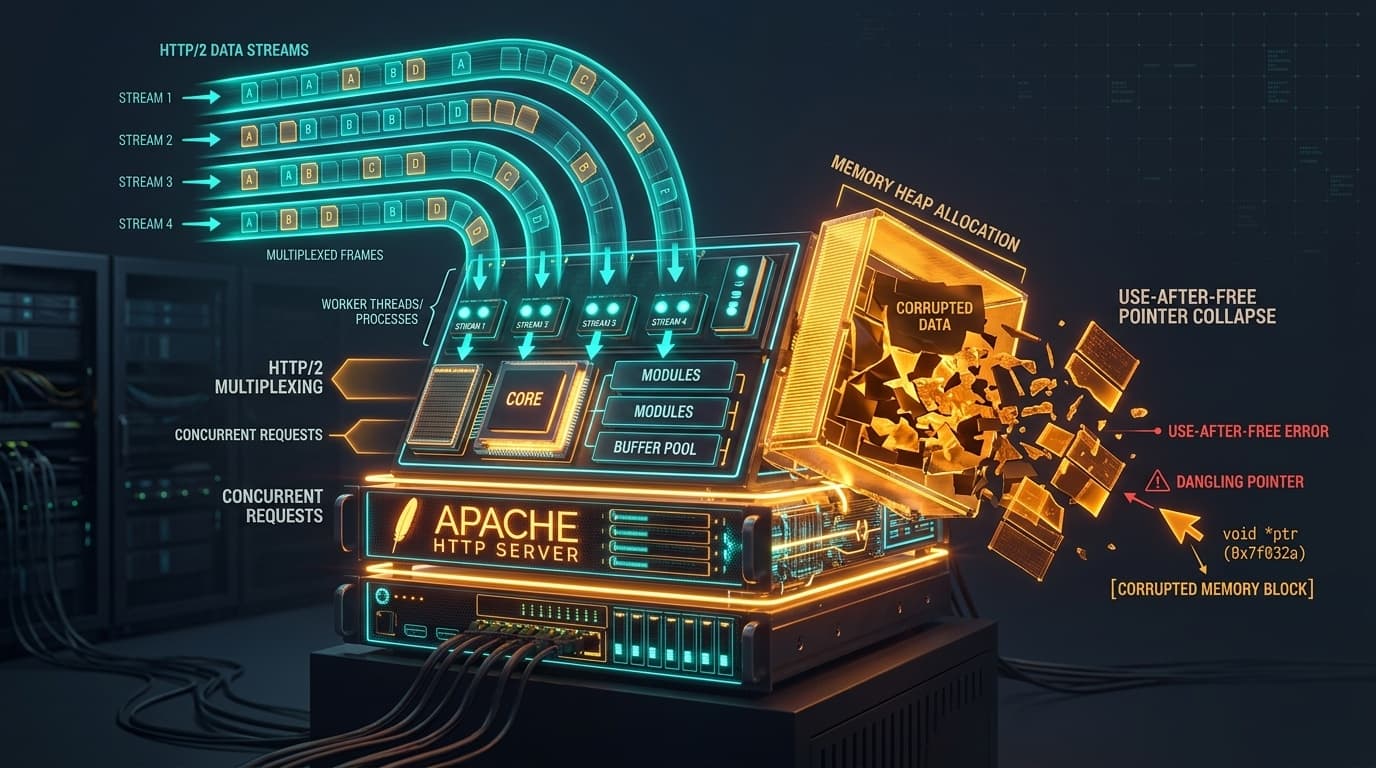
Stories on mod_http2 most often intersect with Apache HTTP Server, HTTP/2 and Use-After-Free, with Technology, Cloud & SaaS the most affected sector. The most recent story, “Apache HTTP Server mod_http2 Use-After-Free Flaw Exposes Web Fleets to Remote Exploitation (CVE-2026-57941)”, was published 2 Oct 2026. Every article is listed below, newest first, with the affected products, severity and remediation guidance in each piece.

Latest coverage