Threat intelligence researchers at Lumen Technologies' Black Lotus Labs and Cisco Talos have pulled back the curtain on one of the most sophisticated cyber espionage operational frameworks ever documented. The adversary—China-nexus state-sponsored actor Volt Typhoon (also tracked as Vanguard Panda or Bronze Silhouette)—has operationalized a covert, multi-hop operational proxy network dubbed "Silent Train."
Replacing the older KV-botnet disrupted by western law enforcement in late 2023, Silent Train functions as a high-speed, disposable operational-security (OPSEC) relay conduit. The adversary weaponized this infrastructure to deliver maximum-severity zero-day exploits directly into centralized management planes, notably compromising Cisco Catalyst SD-WAN control planes (via CVE-2026-20127, rated CVSS 10.0) to implant deep persistence across hundreds of critical infrastructure organizations.
Architecture of the 'Silent Train' Multi-Hop Relay Mesh
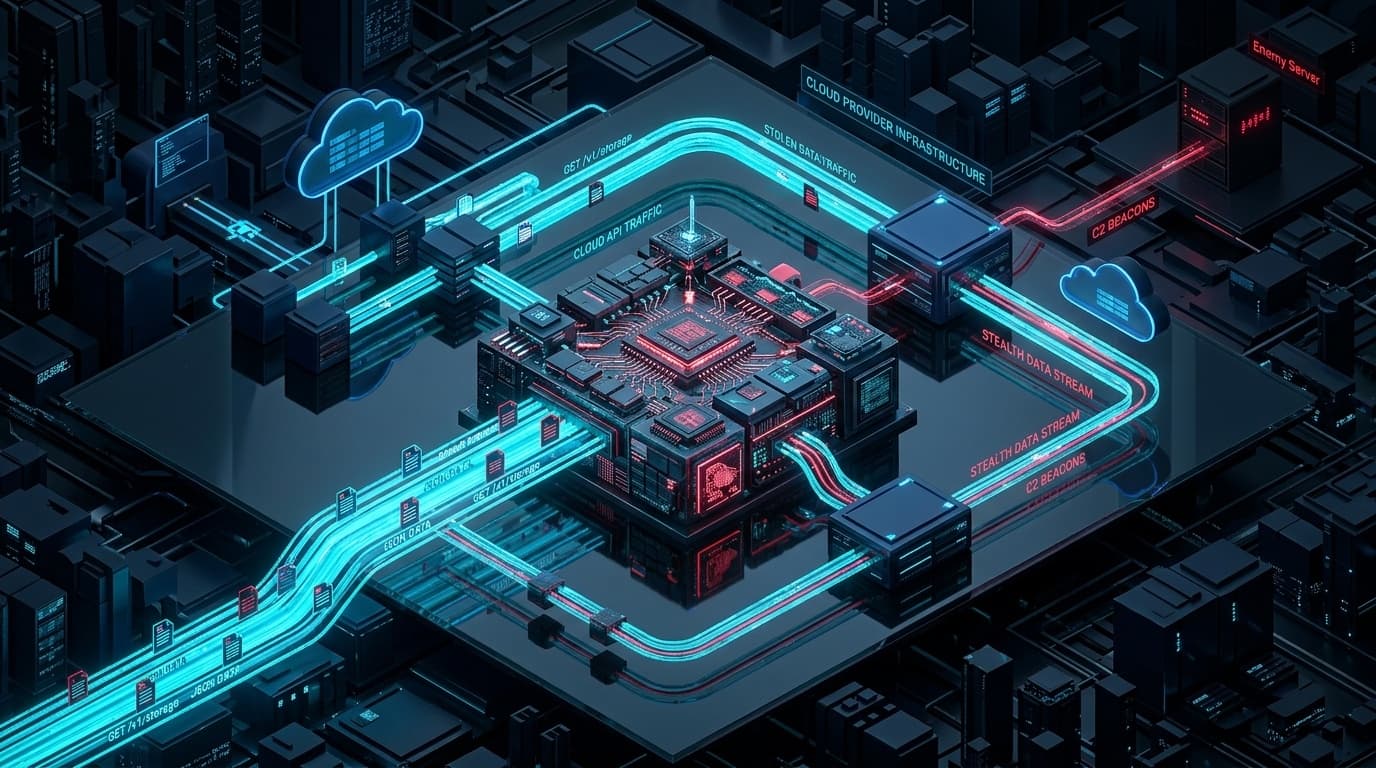
Silent Train is not a traditional DDoS botnet or credential-harvesting cluster. It is an enterprise-grade operational routing pipeline engineered to bypass perimeter geolocation blocking, IP reputation feeds, and threat intelligence blocklists.
The relay network functions via dynamic, multi-tier node chains:
- First-Hop Global Nodes: Exploited consumer and small-office/home-office (SOHO) routers (TP-Link, Netgear, ASUS) distributed across Europe and Asia.
- Mid-Tier Transits: Intermediate relays hosted on compromised cloud VPS instances that dynamically rotate cryptographic forwarding tunnels.
- Egress Terminal Nodes: A compromised IoT device or edge router located physically within the same geographical jurisdiction or telecommunications ASN as the target victim.
When Volt Typhoon executes an exploit against an electric utility or defense contractor in North America, the attack traffic emerges not from a foreign IP, but from a residential cable modem located five miles from the target facility. The entire relay train can be assembled, utilized for a targeted exploit delivery, and wiped clean within two minutes.
Exploitation of Cisco Catalyst SD-WAN (CVE-2026-20127)
Volt Typhoon's primary tactical goal is control-plane decapitation: by compromising centralized network controllers rather than individual endpoints, the adversary gains pervasive access across all connected corporate branches without generating lateral movement alerts.
The group leveraged CVE-2026-20127, a catastrophic authentication bypass flaw in the peering protocol of Cisco Catalyst SD-WAN Controller software. By transmitting a crafted peering handshake packet over TCP port 12346, the attacker bypassed cryptographic identity checks, establishing an unauthorized administrative peering channel with the SD-WAN controller.
Deployment of KeyDrift Malware
Upon securing administrative control-plane access, the operators deployed KeyDrift, a bespoke ELF binary engineered to execute silently within the controller's underlying Linux environment. KeyDrift performed three critical functions:
- IPsec Session Key Extraction: Read active cryptographic key material from memory, allowing the adversary to passively decrypt private inter-branch SD-WAN communications traversing public fiber lines.
- Dynamic Routing Injection: Injected BGP routing table modifications to selectively mirror classified network segments back to adversary-controlled nodes.
- Firmware Tamper Persistence: Wrote backdoor hooks into the appliance's non-volatile boot configuration, ensuring persistence across firmware upgrades.
Targeted Critical Infrastructure Sectors
Telemetry recorded across the Silent Train campaign indicates extensive pre-positioning across vital economic and security pillars:
| Critical Sector | Observed Targeting Focus | Strategic Impact |
|---|---|---|
| Electric Utilities & Grid Operators | Substation SCADA gateways and management trunks | Disruptive kinetic capability during geopolitical conflict |
| Commercial Aviation & Rail | Signaling network relays and maintenance scheduling | Logistical interdiction and operational disruption |
| Telecommunications Carriers | Core routing fabric and lawful intercept interfaces | Strategic intelligence collection and communication tap |
| Maritime Ports & Logistics | Container tracking terminals and crane telemetry | Supply chain stoppage across major commercial shipping lanes |
Defensive Action Checklist
Critical infrastructure security teams must execute immediate containment and verification steps:
# 1. Patch Cisco Catalyst SD-WAN appliances immediately
# Verify running software version against Cisco Advisory cisco-sa-sdwan-auth-bypass
# Upgrade to patched release builds (20.12.3+, 20.15.1+)

# 2. Restrict SD-WAN Control Plane Ports
# Ensure ports 12346 and 12446 are accessible strictly over private, authenticated
# management VLANs and NEVER exposed to public WAN interfaces.

# 3. Hunt for KeyDrift indicators and anomalous peering
netstat -an | grep 12346
find /var/run -name "*.keydrift*" -o -name "*sysrelay*"