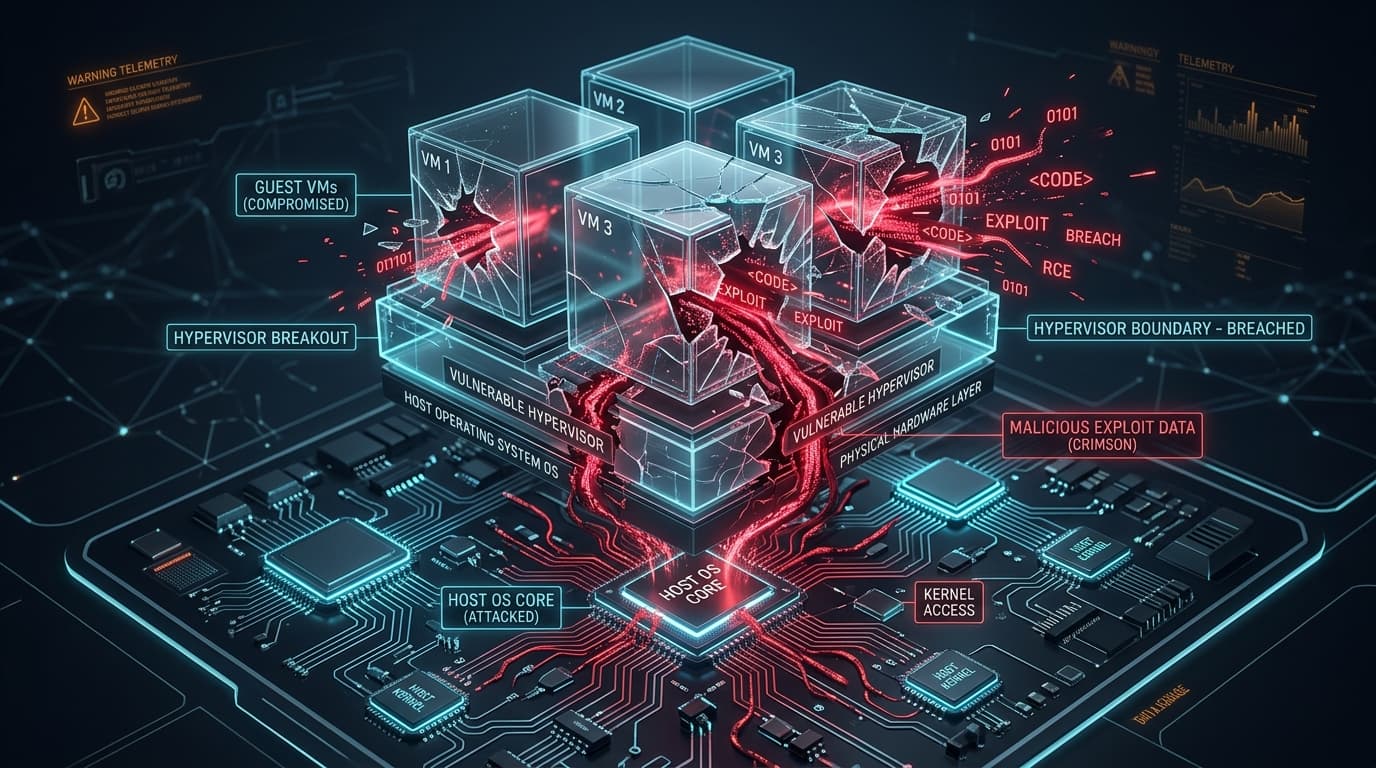
Enterprise virtualization giant Broadcom has released an urgent security advisory, VMSA-2026-0007, remediating multiple critical vulnerabilities in VMware Workstation and VMware Fusion. The most severe flaw allows an attacker possessing administrative control inside a guest virtual machine (VM) to completely break out of the hypervisor boundary and execute arbitrary code on the host operating system.
The primary vulnerability, designated CVE-2026-59346, carries a CVSS v3.1 base score of 9.3 (CVSS:3.1/AV:L/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H). Categorized under CWE-787: Out-of-bounds Write, the defect affects the VMXNET3 virtual network adapter emulation module used across high-performance virtualization setups.
Hypervisor Escape Anatomy: VMXNET3 Emulation Breakdown
Hypervisor boundaries are designed to enforce strict isolation between virtual machines and the host hardware. Virtual devices, such as virtual network interface cards (NICs), emulate physical hardware behaviors through software drivers in the hypervisor process (vmware-vmx.exe on Windows or vmware-vmx on Linux/macOS).
During analysis of the VMXNET3 device driver emulation, security researchers identified that malformed packet descriptor rings transmitted by the guest operating system trigger an out-of-bounds heap write in the host process:
- Descriptor Manipulation: The attacker, operating as root or administrator within the guest VM, crafts a series of DMA (Direct Memory Access) descriptor queues specifying out-of-range packet length offsets.
- Host Heap Corruption: When the host-side VMXNET3 emulation code iterates through the receive/transmit queues, it fails to clamp the calculated memory pointer, writing guest-controlled bytes beyond the allocated buffer boundaries.
- Host Code Execution: By strategically overwriting function pointers within the
vmware-vmxheap, the adversary achieves execution on the host machine, inheriting the user permissions under which the VMware application was launched.
For security researchers, developers, and red teams who run untrusted malware samples or testing containers inside local VMs, a hypervisor breakout exposes their physical workstation and local network directly to compromise.
Affected Products & Patch Availability
| Product | Platform | Vulnerable Versions | Remediated Version |
|---|---|---|---|
| VMware Workstation Pro / Player | Windows & Linux | 17.x prior to 17.5.3 | 17.5.3 |
| VMware Fusion Pro / Player | macOS (Intel & Apple Silicon) | 13.x prior to 13.5.3 | 13.5.3 |
| VMware ESXi Enterprise Hypervisor | Bare-metal server | Not Affected | N/A (Architecture Isolated) |
Interim Workarounds & Verification Steps
Broadcom strongly recommends applying the updated software releases immediately. For organizations unable to patch workstations instantaneously, administrators can implement the following interim workarounds:
- Switch Virtual Network Adapters: Change the virtual network adapter type in the VM configuration (
.vmxfile) fromvmxnet3to the standarde1000eore1000emulation:# Edit VM configuration file (.vmx) ethernet0.virtualDev = "e1000e" - Disable 3D Graphics Acceleration: While the primary breakout involves VMXNET3, secondary vulnerability CVE-2026-59347 involves the 3D acceleration graphics shader. Disabling 3D acceleration mitigates secondary attack surfaces:
mks.enable3d = "FALSE" - Principle of Least Privilege: Ensure VMware Workstation is never executed under elevated Administrator or root privileges on host workstations. Running the virtualization engine as a standard unprivileged user limits an attacker’s breakout blast radius.