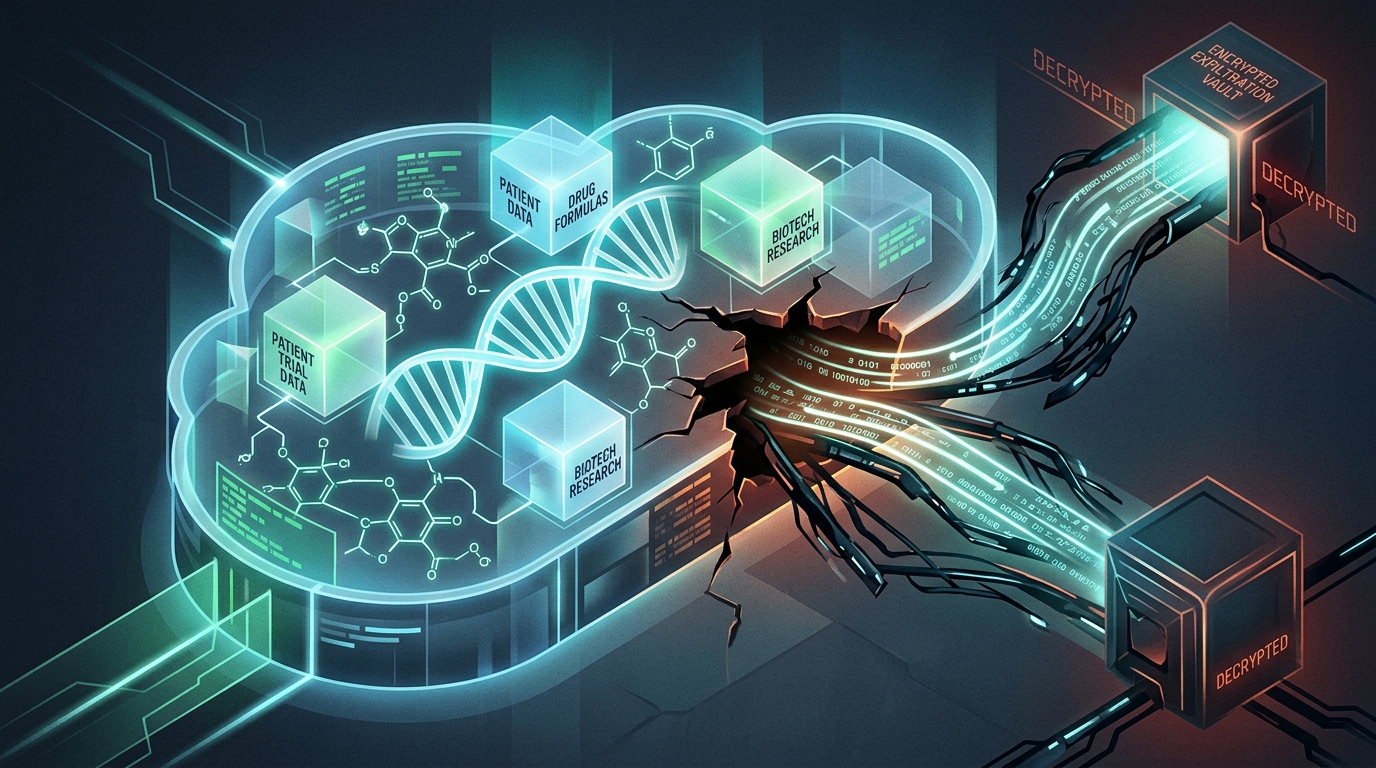
A multinational biotechnology and pharmaceutical manufacturing enterprise has filed an official regulatory disclosure under Item 1.05 of SEC Form 8-K revealing a material cybersecurity incident. The disclosure documents an advanced persistent threat (APT) intrusion that compromised a secure cloud clinical data repository, resulting in the unauthorized exfiltration of proprietary Phase 3 clinical trial oncology datasets, genomic sequencing analysis, and regulatory submission dossiers intended for the U.S. FDA and European Medicines Agency (EMA).
Forensic Timeline: Contractor Credential Leak to Cloud Exfiltration
According to the regulatory disclosure and incident response documentation filed with regulatory authorities, the breach originated from a compromised third-party contract research organization (CRO):
- Initial Credential Compromise: Attackers obtained valid AWS IAM service account credentials belonging to an outsourced bioinformatics data analytics firm. The credentials had been committed to an improperly configured private code repository.
- Cloud Database Pivot: The stolen IAM role held
rds:CreateDBClusterSnapshotandrds:CopyDBClusterSnapshotpermissions on an Amazon Aurora PostgreSQL production cluster housing electronic data capture (EDC) study records. - Silent Exfiltration via Snapshot Sharing: The adversary created an unencrypted snapshot of the clinical trial database, modified snapshot sharing attributes to allow access from an external adversary-owned AWS account, and extracted 680 gigabytes of clinical patient trial records over encrypted cloud interconnects.
Materiality Assessment & Regulatory Blast Radius
The pharmaceutical company's board of directors determined the incident to be material under SEC rules due to the immense market valuation of proprietary clinical study intellectual property:
| Operational Domain | Status Reported in Form 8-K | Regulatory & Market Exposure |
|---|---|---|
| Manufacturing Operations | Unaffected / Operational | Active pharmaceutical ingredient (API) synthesis plants remained segregated. |
| Clinical Trial Integrity | Intact / No Data Tampering | Forensic hashing verified trial records were copied but not altered; patient dosing protocols continue uninterrupted. |
| Regulatory Filings | Under Assessment | Notifications initiated under HIPAA, EU GDPR, and SEC Item 1.05; estimated legal and forensic investigation costs exceed $26M. |
Life Sciences Defense & Cloud Hardening Playbook
- Block Cross-Account Snapshot Sharing: Deploy AWS Organizations Service Control Policies (SCPs) that strictly deny
rds:ModifyDBClusterSnapshotAttributeactions that share snapshots outside the corporate AWS Organization ID. - Enforce Ephemeral IAM Credentials: Eliminate static, long-lived AWS IAM access keys for third-party contractors in favor of temporary IAM roles assumed via AWS IAM Identity Center and short-duration STS tokens.
- Implement Column-Level Encryption for Clinical Records: Enforce application-layer envelope encryption using customer-managed AWS KMS keys for sensitive patient clinical fields, ensuring exfiltrated database snapshots remain unreadable ciphertext.