The Cybersecurity and Infrastructure Security Agency (CISA), alongside Rockwell Automation, has released industrial security advisory ICSA-26-242-01 disclosing a critical remote code execution vulnerability (CVE-2026-51290, CVSS 9.8) in FactoryTalk View Site Edition (SE). The flaw allows unauthenticated remote threat actors to execute arbitrary code with NT AUTHORITY\SYSTEM privileges on industrial Human-Machine Interface (HMI) and supervisory SCADA servers.
Vulnerability Deep-Dive: Insecure .NET Object Deserialization (CWE-502)
FactoryTalk View SE serves as the primary supervisory automation layer across automotive, chemical, and pharmaceutical manufacturing facilities globally, providing graphic operator displays, alarm management, and trending for Allen-Bradley ControlLogix and CompactLogix PLCs.
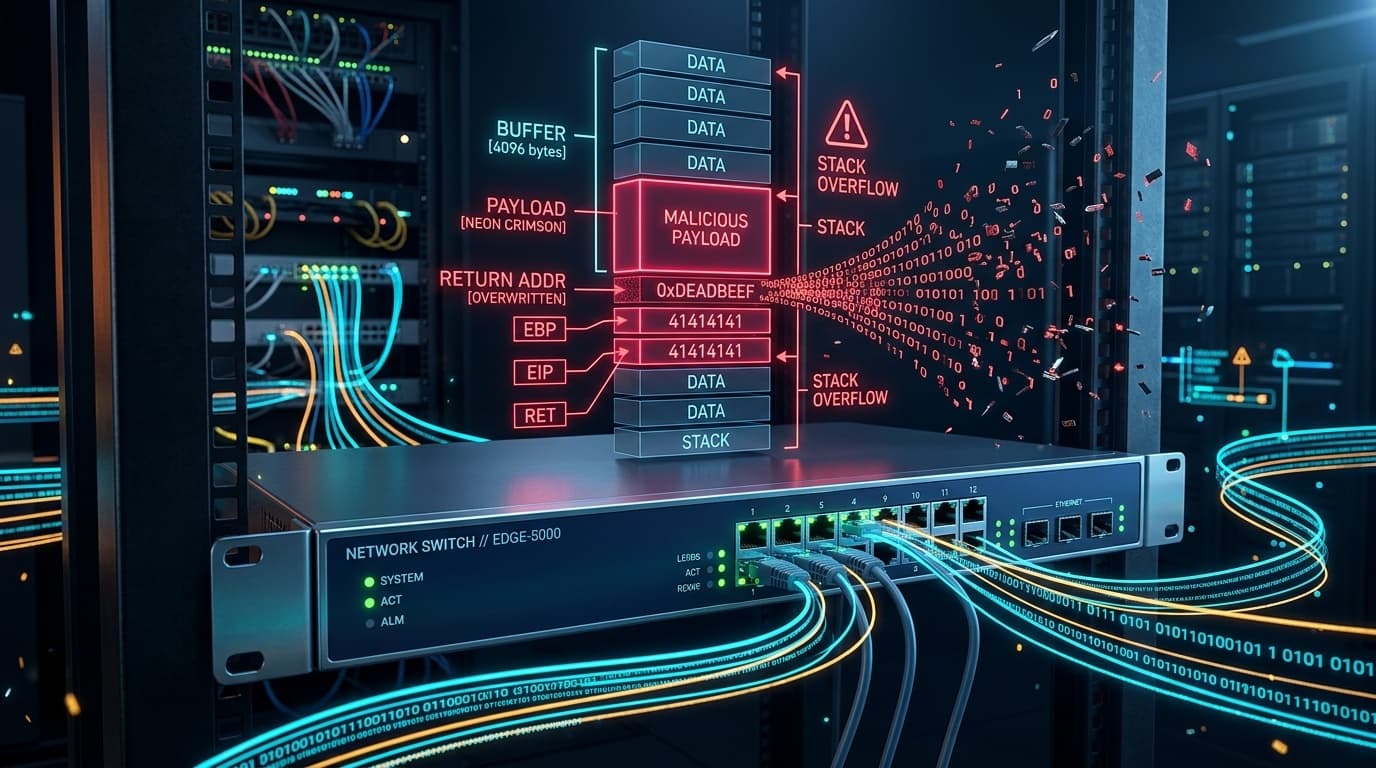
According to technical disclosures by Rockwell Automation PSIRT, the vulnerability resides within the RNAutomation background service listening on TCP port 4241. The service utilizes the legacy .NET BinaryFormatter serializer to process incoming data packets from distributed client consoles without type filtering or cryptographic payload validation.
// Insecure .NET deserialization pattern in RNAutomation service listener
BinaryFormatter formatter = new BinaryFormatter();
// Missing Binder validation allows gadget chain injection
object clientPayload = formatter.Deserialize(networkStream);
By transmitting crafted serialized byte sequences containing known .NET gadget chains (such as TypeConfuseDelegate or WindowsIdentity proxies), an attacker forces the service to instantiate arbitrary processes (e.g., cmd.exe or PowerShell scripts) within the root operating system context.
Defensive Remediation Checklist for Industrial Operators
- Deploy Rockwell Security Update: Install FactoryTalk View SE patch v14.00.01 or apply security roll-up update CPR9-SR14.1.
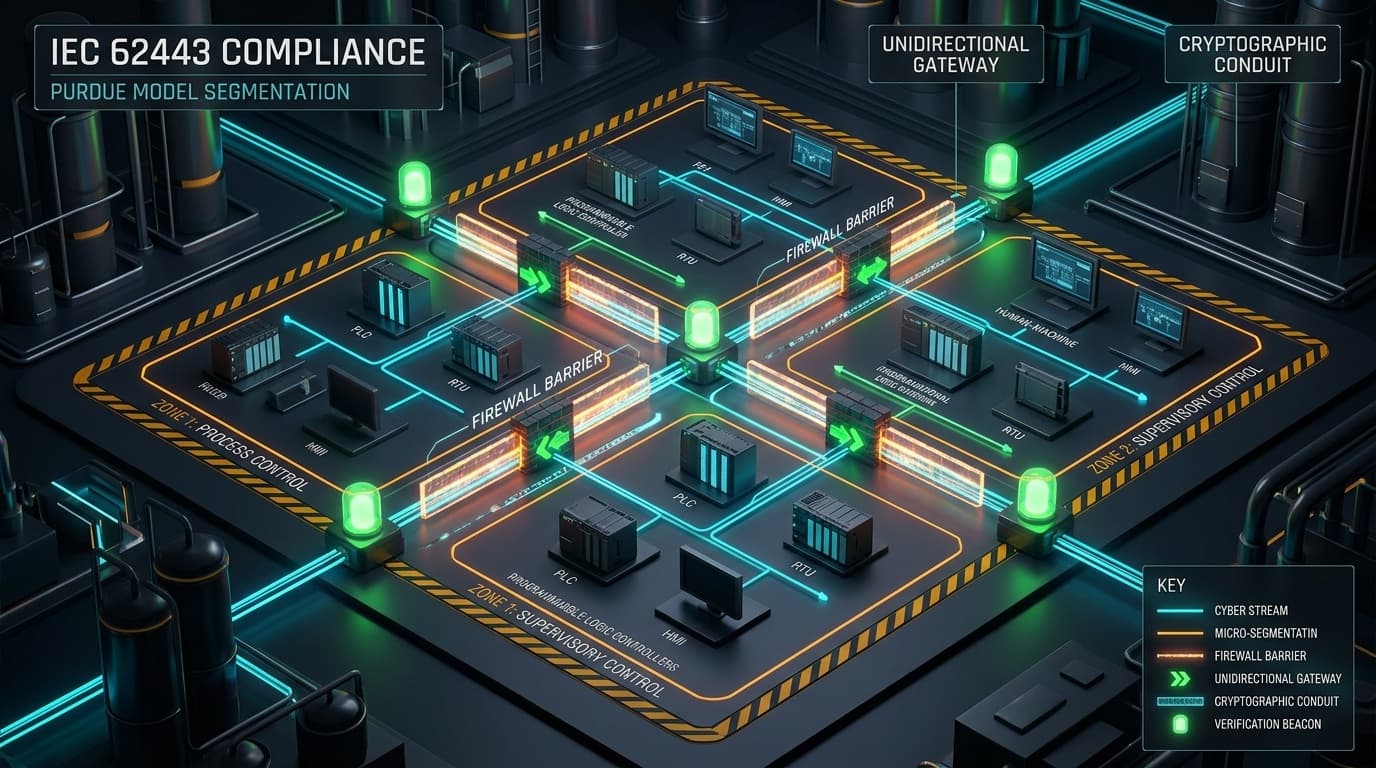
- Firewall Inbound Port 4241: Restrict network access to TCP port 4241 exclusively to verified FactoryTalk client IPs located within Purdue Model Level 2/3 supervisory networks.
- Enable FactoryTalk Security (FTSEC): Enforce mutual certificate authentication and Windows user group authorization across all FactoryTalk directory communications.