Regulatory Mandate Overview
The Reserve Bank of India (RBI) has published an updated regulatory circular under its Master Direction on Information Technology Governance, Risk, Controls and Assurance Practices, placing unprecedented requirements on regulated financial institutions regarding cloud concentration risk and cyber operational resilience.
The directive applies to all Scheduled Commercial Banks (SCBs), Small Finance Banks, Payment System Operators (PSOs), and Non-Banking Financial Companies (NBFC-Top and Upper Layers). Under the new guidelines, financial institutions must eliminate systemic dependency on any single cloud service provider (CSP) for Core Banking Solutions (CBS) and UPI transaction routing engines.
Mandatory Cloud Architecture & Concentration Controls
The RBI's Department of Supervision noted that increasing cloud adoption has created dangerous macro-prudential concentration risks across a small number of global hyperscalers (AWS, Microsoft Azure, Google Cloud). To safeguard financial stability, regulated entities must enforce the following architectural mandates:
| Regulatory Domain | Mandatory Baseline Standard | Verification Mechanism |
|---|---|---|
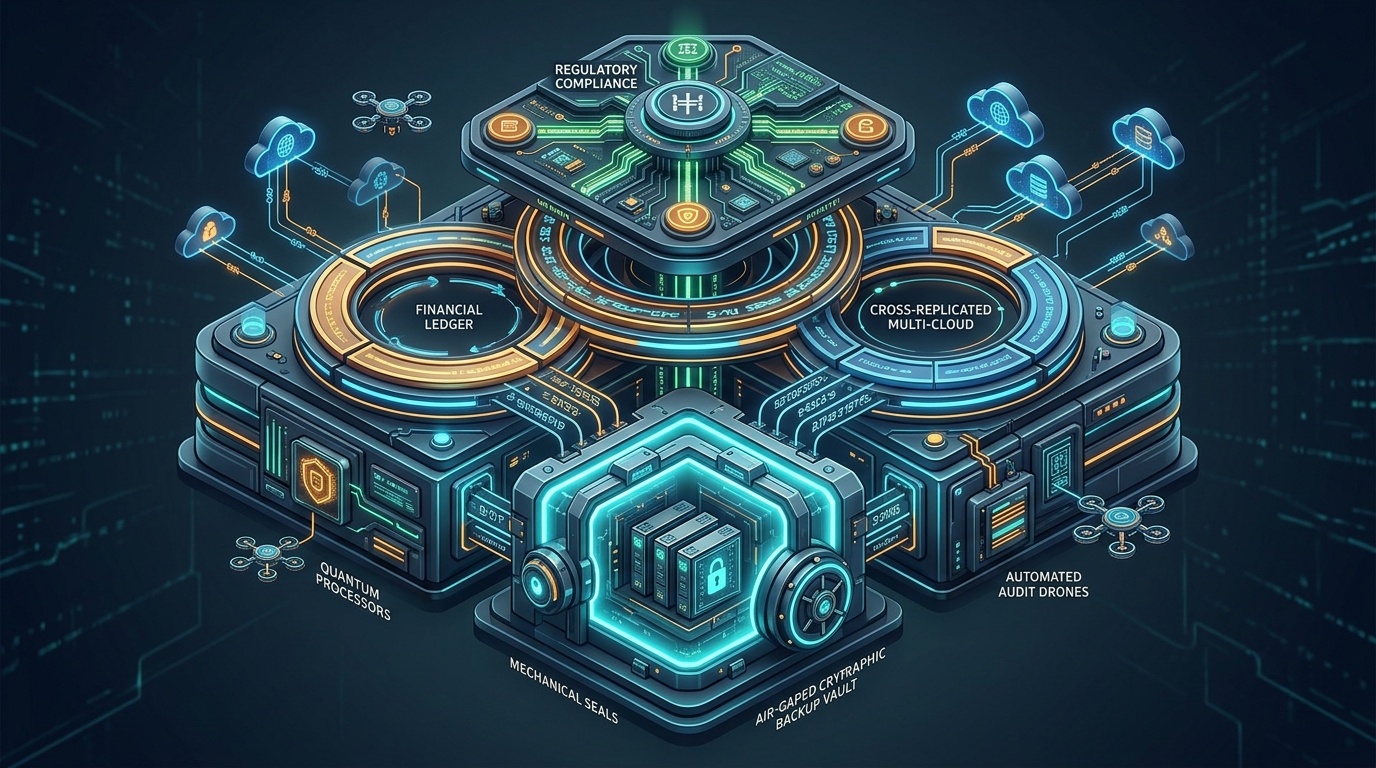
| Cloud Portability & Multi-Cloud | Core payment workloads must run on portable containerized runtimes across at least two independent hyperscalers | Bi-annual live traffic failover drill across primary and secondary CSPs |
| Immutable Air-Gapped Vaults | WORM (Write-Once-Read-Many) encrypted storage isolated from standard corporate and cloud IAM controls | Independent cryptographic audit and simulated ransomware recovery within 120 minutes |
| Incident Reporting Timeline | Mandatory preliminary notification of cloud degradation or breach to RBI/CERT-In within 6 hours | Supervisory log submission via dedicated CSITE portal |
Zero-Trust Immutable Vault Architecture
A key focus of the Master Direction is the creation of a Clean Room Immutable Recovery Vault. Traditional cloud snapshots stored within the same cloud tenancy have repeatedly proven vulnerable to credential compromise, ransomware extortion, and IAM policy destruction. Under the RBI framework:
- Air-Gapped Cryptographic Isolation: Backup copies of transactional databases, customer balances, and ledger logs must be pushed to an air-gapped immutable storage vault governed by separate, hardware-token-based dual-custody authorization.
- Data Localization Invariant: In accordance with existing RBI data localization directives, all immutable replicas and encryption keys (HSM appliances) must reside physically within the borders of India.
- Continuous Disaster Recovery Validation: Regulated entities must conduct unannounced live disaster recovery failover exercises at least once every six months, proving that transaction logs can be rehydrated and reconciled within the mandated 2-hour Recovery Time Objective (RTO).
Compliance Timeline & Supervisory Enforcement
Regulated entities have been granted a six-month implementation window to align their IT governance frameworks with the updated Master Direction. Chief Information Security Officers (CISOs) and Board-level Risk Committees must submit their compliance certification to the RBI Department of Supervision by Q3 2026. Non-compliance exposes institutions to penal enforcement under Section 47A of the Banking Regulation Act, 1949, including business restrictions and financial penalties.