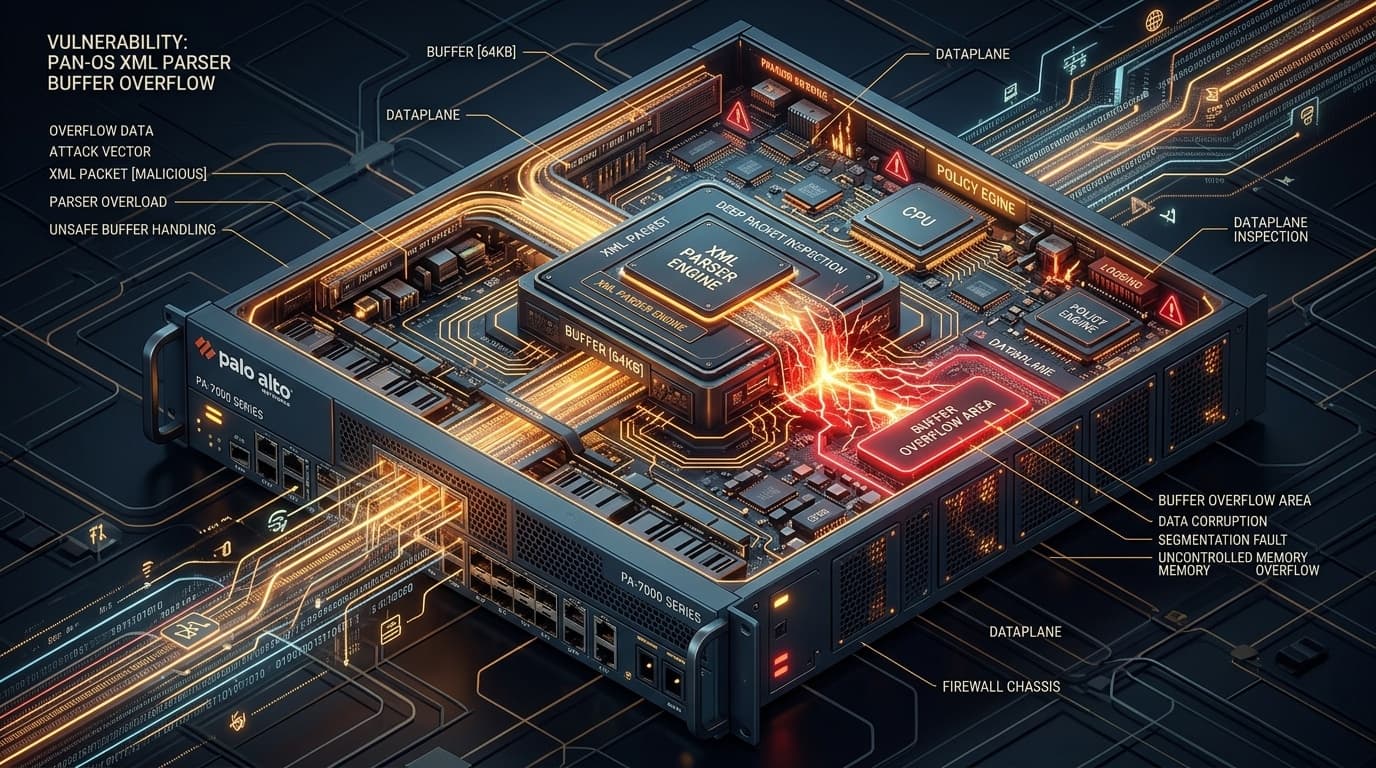
Palo Alto Networks has published a major security advisory (PAN-SA-2026-0012) disclosing a high-severity buffer overflow vulnerability (CVE-2026-0310, CVSS 7.2 / CVSS v4.0 8.4) embedded within the XML processing engine of PAN-OS. The flaw affects both the dedicated management interface and select dataplane processing ports across Next-Generation Firewalls (NGFW), Panorama centralized management appliances, and Prisma Access cloud deployments, enabling unauthenticated remote attackers to trigger system crashes or execute arbitrary code with root privileges on physical PA-Series appliances.
Vulnerability Mechanics: Classic Buffer Overflow in XML Parser (CWE-120)
PAN-OS relies heavily on XML document structures for internal configuration storage, REST API transactions, and inter-process communication between the management plane (MP) and dataplane (DP).
The defect occurs during the parsing of oversized XML attribute strings and deeply nested tag declarations transmitted to the web management daemon. The C-based parser copies XML node contents into a fixed-size stack buffer without verifying boundary bounds:
// Insecure XML string extraction logic in PAN-OS management handler
void parse_xml_attribute(xmlNodePtr node, char *attr_name) {
    char stack_buf[256];
    char *val = (char *)xmlGetProp(node, (xmlChar *)attr_name);
    if (val) {
        // INSECURE: strcpy without length check triggers buffer overflow
        strcpy(stack_buf, val);
        process_attribute(stack_buf);
    }
}
When an attacker transmits a maliciously crafted XML payload containing an attribute string exceeding 256 bytes, the stack memory frame is corrupted. On physical PA-Series hardware lacking hardened compiler canaries, this condition allows control of the instruction pointer (EIP/RIP), providing direct root shell execution.
Affected Architectures & Remediation Targets
| Product Line | Vulnerable PAN-OS Branch | Remediated Release |
|---|---|---|
| PAN-OS 12.2 | Versions < 12.2.3 | PAN-OS 12.2.3 |
| PAN-OS 12.1 | Versions < 12.1.10 | PAN-OS 12.1.10 (and 12.1.4-h10) |
| PAN-OS 11.2 | Versions < 11.2.5 | PAN-OS 11.2.5 |
| Panorama Appliance | Panorama M-Series < 12.1.10 | Panorama 12.1.10 |
Remediation & Defense-in-Depth Directives
- Apply Cumulative Maintenance Patches: Immediately schedule emergency maintenance windows to upgrade PAN-OS and Panorama appliances to the respective fixed builds.
- Isolate Management Interfaces: Follow Palo Alto Networks security baselines by removing administrative web interfaces from public internet exposure. Restrict port 443 access strictly to dedicated, out-of-band management subnets.
- Monitor System Logs: Inspect
mp-log pan_comm.loganddevsrvr.logfor abnormal segmentation fault crashes or memory allocation errors.