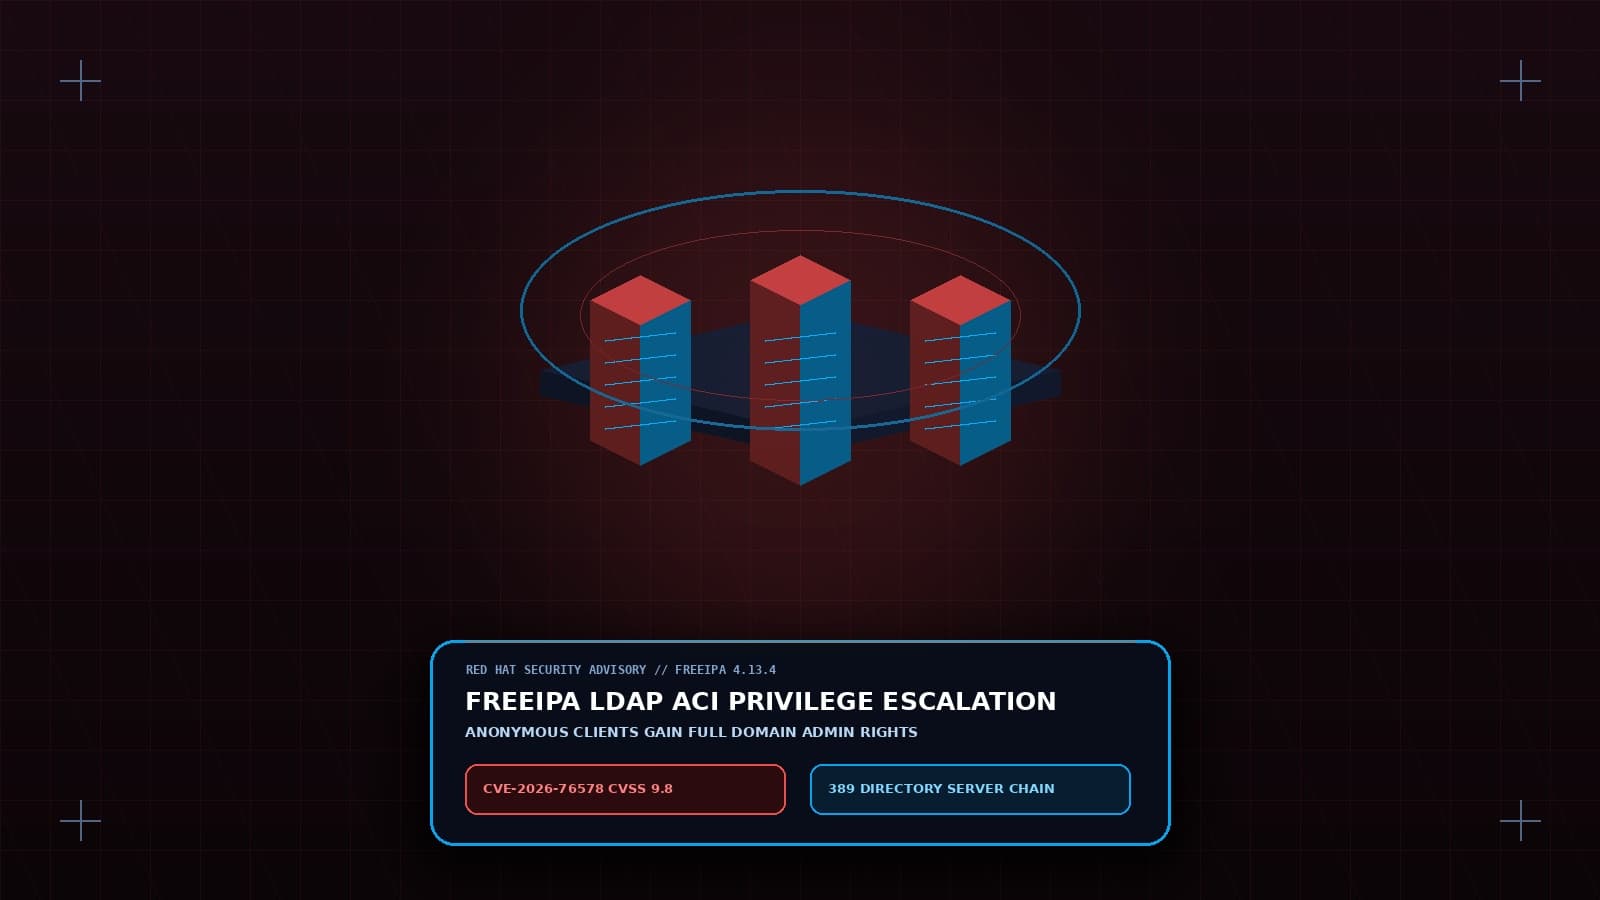
Red Hat has issued a critical security advisory addressing a severe privilege escalation vulnerability chain impacting FreeIPA, the open-source identity and domain controller management suite that powers Red Hat Enterprise Linux (RHEL) Identity Management (IdM). Tracked as CVE-2026-76578 with a CVSS 4.0 score of 9.8, the vulnerability enables an anonymous network attacker who has never authenticated to the domain to create an arbitrary Kerberos principal and grant it permanent administrative membership within the domain.
FreeIPA serves as the central authentication, authorization, and cryptographic key authority for extensive Linux server fleets across government departments, cloud service providers, and defense contractors. A compromise of the FreeIPA master server grants full root control across all enrolled enterprise Linux servers.
The Flaw Chain: ACI Misconfiguration and Directory Object Injection
The vulnerability arises from a semantic flaw inside a default Access Control Instruction (ACI) shipped with FreeIPA's underlying directory database, 389 Directory Server. The specific ACI was intended to allow authenticated domain users to manage their own hardware and software One-Time Password (OTP) tokens without requiring helpdesk intervention.
Due to a parsing defect in the ACI's target filter, the directory server failed to enforce bound user verification when evaluating newly submitted object creation requests. An anonymous LDAP bind (which requires no username or password) could exploit this gap to perform an object injection sequence:
# Logical representation of the unauthorized LDAP injection sequence
dn: uid=backdoor_admin,cn=users,cn=accounts,dc=example,dc=com
changetype: add
objectClass: top
objectClass: person
objectClass: ipaUser
objectClass: krbPrincipalAux
uid: backdoor_admin
userPassword: NewSecurePassword123!
ipaProtectedOperation: otpTokenAdd

# Chained modify operation adding the principal to the Domain Admins group
dn: cn=admins,cn=groups,cn=accounts,dc=example,dc=com
changetype: modify
add: member
member: uid=backdoor_admin,cn=users,cn=accounts,dc=example,dc=com
Once injected, the adversary acquires a fully functional Kerberos Ticket Granting Ticket (TGT) carrying the administrative group SID, achieving full domain takeover.
Required Mitigation and Integrity Audit
- Update FreeIPA Packages: Upgrade RHEL IdM and upstream FreeIPA installations immediately to version
4.13.4or apply the vendor errata (RHSA-2026-7657). - Audit Directory Memberships: Run the command
ipa group-show adminsand review all members of privileged groups (admins,trust admins) to ensure no unrecognized principals exist. - Restrict LDAP/LDAPS Network Ingress: Block unauthenticated network access to ports 389 (LDAP) and 636 (LDAPS) from untrusted subnets and workstation networks.