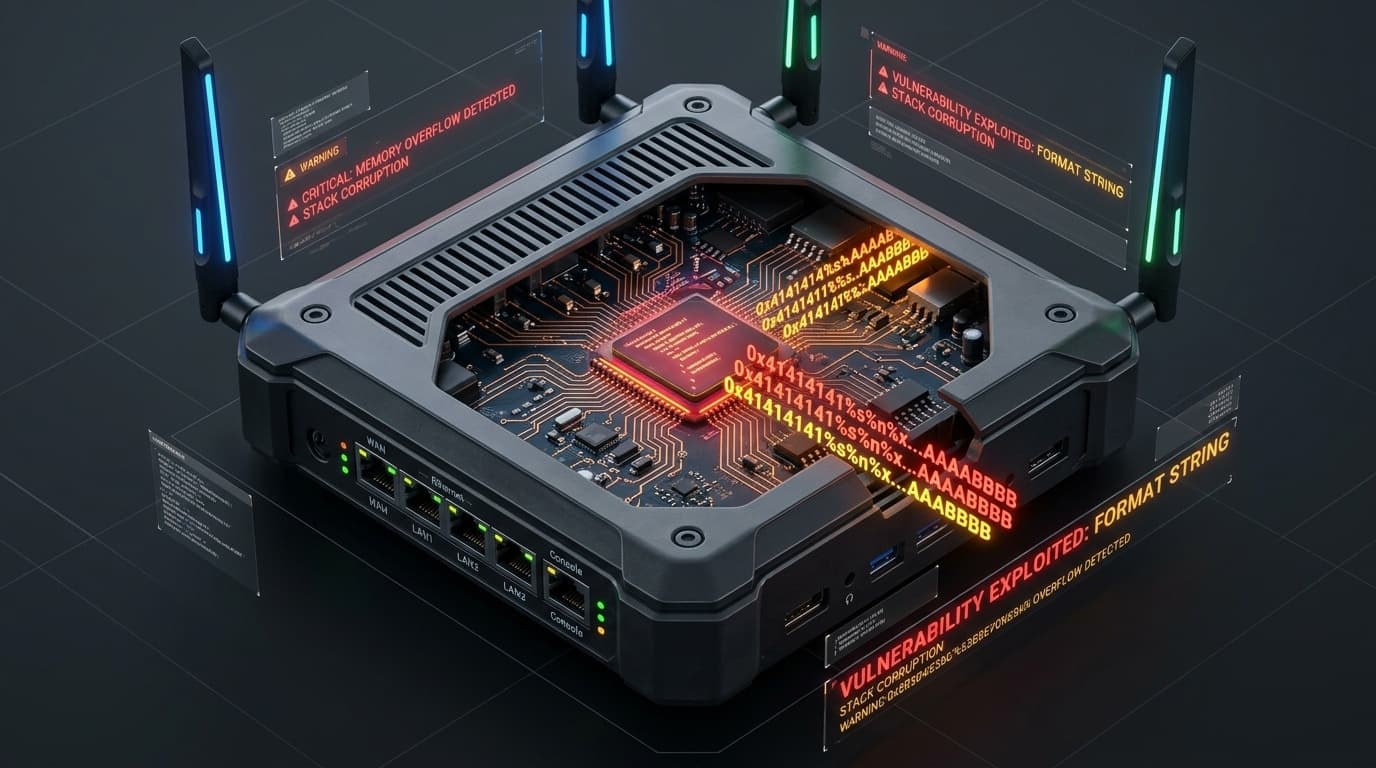
A critical memory corruption vulnerability has been uncovered in ASUS gateway and enterprise router firmware, affecting multiple high-performance networking devices deployed across branch offices, corporate remote workforces, and industrial edge topologies. Designated as CVE-2026-14157 and cataloged in GitHub Advisory GHSA-j8q5-whhx-5847 with a CVSS v3.1 base score of 9.8 (Critical), the flaw enables attackers to execute arbitrary system commands with root privileges via crafted file uploads processed by the web management service.
Edge Routing Hardware as Initial Access Vectors
Gateway routers serve as the demarcation boundary between enterprise local networks and the public internet. Because these devices terminate IPsec/WireGuard VPN tunnels, perform DHCP assignment, and handle network address translation (NAT), compromising the router grants adversaries immediate visibility into all internal corporate traffic, lateral movement conduits, and DNS redirection capabilities.
Root Cause Analysis: Externally Controlled Format String (CWE-134)
The vulnerability exists within the firmware's internal web management daemon (httpd). During configuration restoration, firmware validation, or custom certificate installation, the web service handles multipart file uploads.
In affected firmware builds, the module responsible for logging uploaded file metadata passes the attacker-controlled original filename directly into a syslog() or snprintf() call without a static format specifier:
// Vulnerable Parsing Logic in ASUS httpd Upload Handler
void handle_file_upload(char *boundary, int content_length) {
    char filename[256];
    extract_multipart_filename(boundary, filename);

    // FATAL FLAW: filename passed directly as format argument!
    syslog(LOG_INFO, filename); // Format String Vulnerability (CWE-134)
}
By naming an uploaded file with format string tokens—such as %x.%x.%x.%n—an attacker instructs the C runtime format parser to read arguments from the stack. The %n specifier writes the number of characters formatted so far to an address supplied on the stack.
Because the router firmware runs without modern Address Space Layout Randomization (ASLR) or stack canaries on embedded MIPS/ARM architectures, an adversary can calculate predictable stack offsets, overwrite saved instruction pointers (EIP/RIP), and pivot execution to shellcode located in the upload buffer.
Firmware Security State Comparison
| Security Parameter | Vulnerable Firmware | Remediated Firmware |
|---|---|---|
| Format Specifier Safety | Variable passed as direct format string: syslog(lvl, str) |
Explicit static format string: syslog(lvl, "%s", str) |
| Memory Write Protection | Stack overwritten via %n specifier |
Input sanitization strips format tokens from multipart headers |
| Post-Exploit Exposure | Root shell execution; persistent backdoor in flash memory | Firmware validation rejects malformed file structures cleanly |
Remediation & Defense Actions
- Install ASUS Firmware Updates: Download and apply the latest security firmware from the official ASUS Support Portal for your specific router hardware revision.
- Disable Remote Management from WAN: Ensure that the router's web administration interface is accessible strictly from local LAN subnets and never exposed to the public internet:
Administration > System > Remote Access Config > Enable Web Access from WAN: NO - Rotate Gateway Credentials: Change default administrative passwords and regenerate all internal SSL/TLS certificates and VPN preshared keys.