Executive Summary
ABB and the Cybersecurity and Infrastructure Security Agency (CISA) have released coordinated cybersecurity notifications detailing CVE-2026-71880, a critical remote recipe parameter injection vulnerability in ABB Ability System 800xA Batch Management. The flaw, which has been evaluated with a CVSS v3.1 base score of 9.6 (Critical), allows an unauthenticated network adversary on the control network to alter active batch recipe parameters, phase logic, and chemical dispensation setpoints without operator authorization.
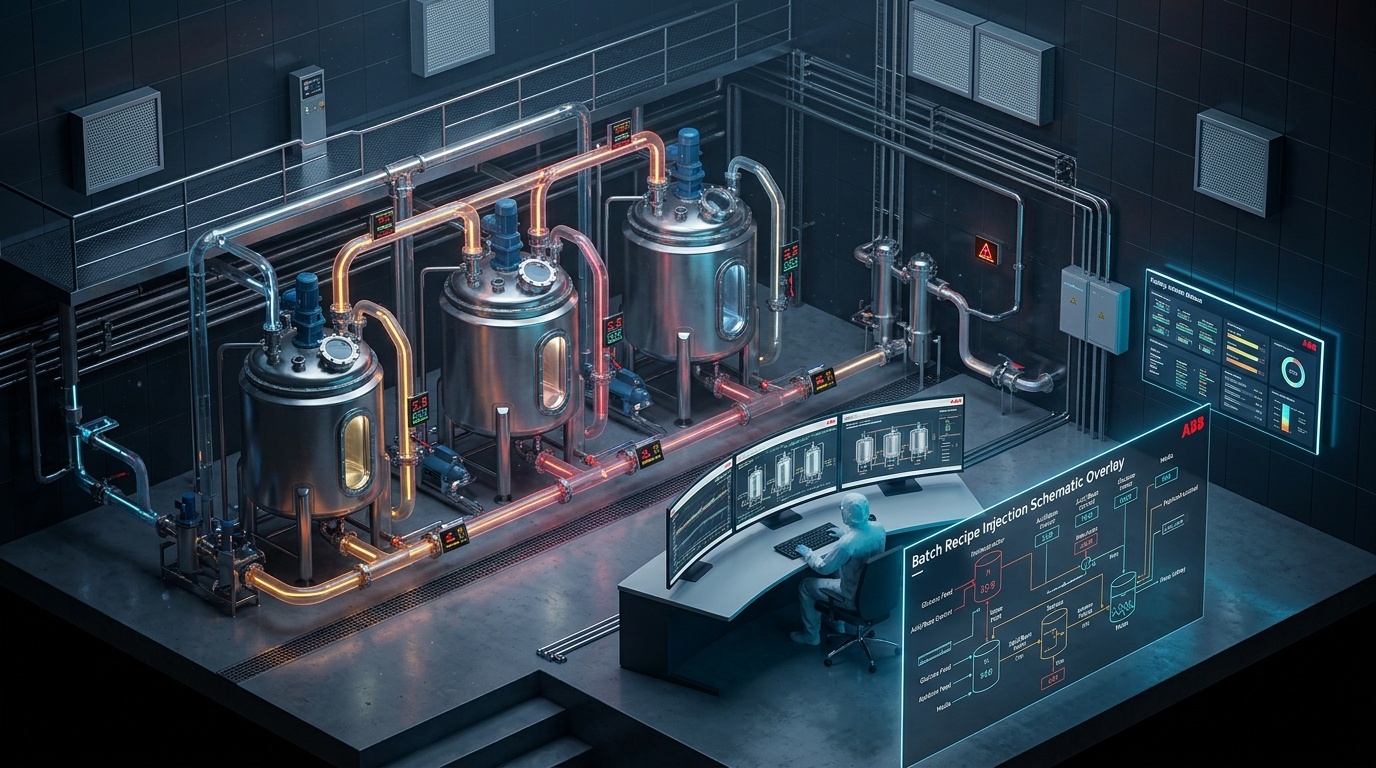
The System 800xA Batch Management package is the operational centerpiece for major pharmaceutical manufacturing facilities, biopharmaceutical bioreactors, vaccine production plants, and specialty chemical processing complexes. Manipulation of recipe parameters directly threatens product quality, regulatory compliance (FDA 21 CFR Part 11), and patient safety.
Vulnerability Deep Dive: Unauthenticated RPC Service Command Handler
The vulnerability exists within the Batch Execution Service (BES) daemon listening on TCP port 28540. The BES service coordinates recipe phases (e.g., heating, agitation, acid titration, sterilization) and sends execution commands down to AC 800M controller units.
Security analysis revealed that the remote procedure call (RPC) endpoint responsible for dynamic recipe adjustment failed to require authentication or cryptographic session binding. By sending structured XML-RPC packets with crafted phase parameter tags, an attacker can overwrite active process parameters—such as target pH, reaction temperature, or ingredient feed quantities—while the batch is executing:
<!-- Malicious BES RPC payload altering chemical titration setpoint -->
<BatchCommand action="UpdateActivePhaseParameter">
  <BatchID>B-2026-PHARMA-0914</BatchID>
  <UnitID>BIOREACTOR_UNIT_04</UnitID>
  <Parameter Name="AcidTitrationSetpoint" Type="Float">
    <Value>8.45</Value> <!-- Subtly altered from approved recipe value 7.20 -->
  </Parameter>
  <AuditOverride BypassSignoff="True" />
</BatchCommand>
Operational and Regulatory Repercussions in Biopharma
In life sciences and pharmaceutical manufacturing, compliance with Good Manufacturing Practice (GMP) and FDA 21 CFR Part 11 requires that any parameter adjustment be accompanied by electronic signatures, cryptographic timestamps, and justification entries in an immutable audit trail.
CVE-2026-71880 circumvents the built-in audit logging mechanism by accepting commands directly at the network layer before they pass through the operator interface signoff workflow. This creates grave operational hazards:
- Batch Spoilage: Subtly altering temperature or pH profiles during active cell culture growth in a bioreactor can ruin million-dollar batches of monoclonal antibodies or vaccines.
- Adulterated Finished Goods: If parameter modifications go undetected by secondary analytical quality controls, tainted pharmaceutical batches could theoretically pass into commercial distribution.
- Mass Product Recalls: Unverified modifications invalidate electronic batch records (EBRs), forcing regulatory authorities to mandate plant shutdowns and total product recalls.
Remediation & Defense-in-Depth Roadmap
ABB has released software maintenance packages to eliminate the flaw. Asset owners and automation engineers should implement the following defense-in-depth protections:
- Deploy Software Maintenance Packs: Upgrade ABB System 800xA Batch Management to version
6.1.1.3or6.2.0.1containing authenticated RPC handler enhancements. - Block Port 28540 at Cell Firewalls: Restrict communication to TCP port 28540 strictly to authorized engineering client workstations; block all access from corporate IT or untrusted subnets.
- Enforce Dual-Signoff Workflows: Re-enable physical key interlocks and hardware-enforced parameter verification loops on AC 800M controllers.
- Continuous OT Network Anomaly Detection: Deploy passive industrial network monitoring sensors configured to flag unexpected RPC packets communicating with the Batch Execution Service.