Advisory Overview
ABB has issued an urgent cybersecurity advisory alerting asset owners in the chemical, life sciences, and pharmaceutical manufacturing sectors to CVE-2026-79350 (CVSS score 9.4), a high-severity flaw in ABB Ability System 800xA Batch Management.
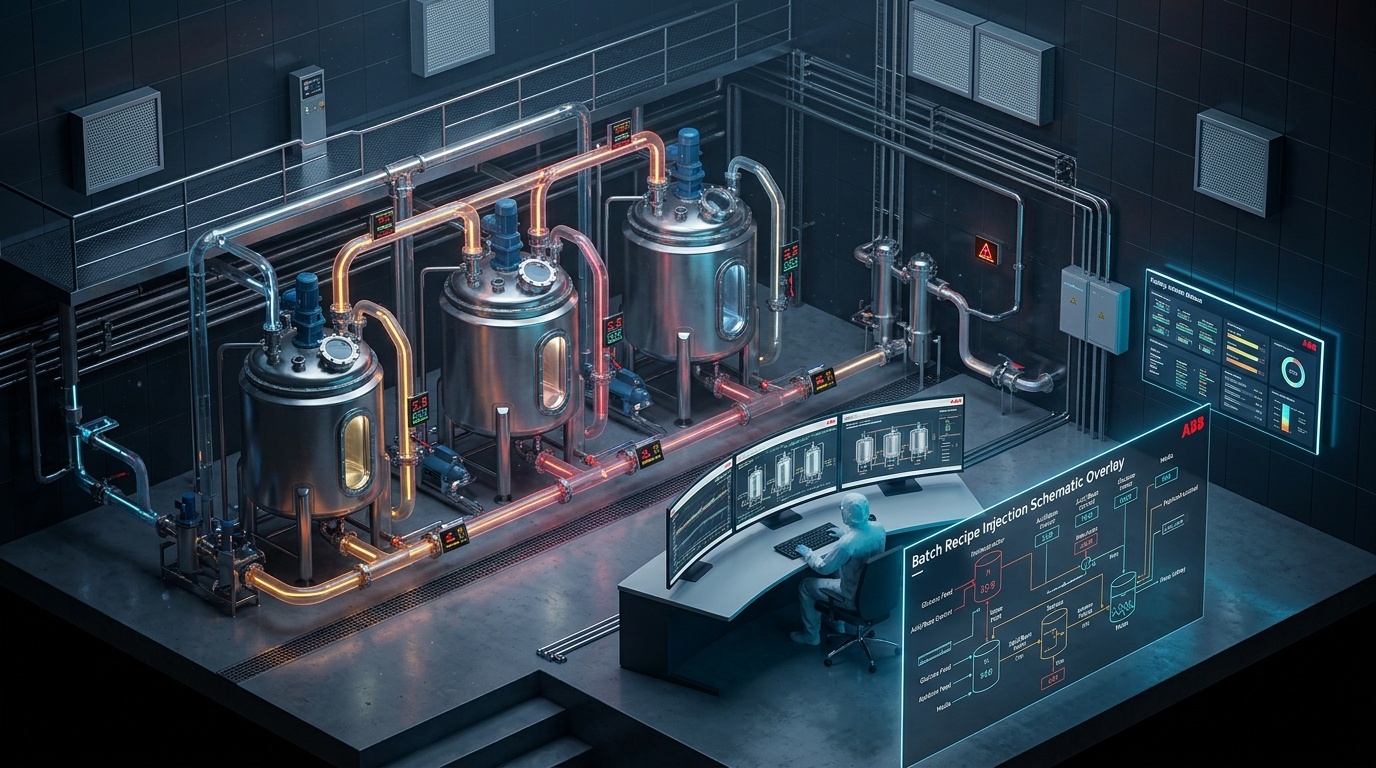
System 800xA Batch Management orchestrates complex recipe execution according to ISA-88 standards across distributed control system (DCS) architectures. Successful exploitation allows an attacker to tamper with batch parameters, alter chemical ingredient mixing ratios, or initiate unauthorized production cycles.
Technical Root Cause & Protocol Breakdown
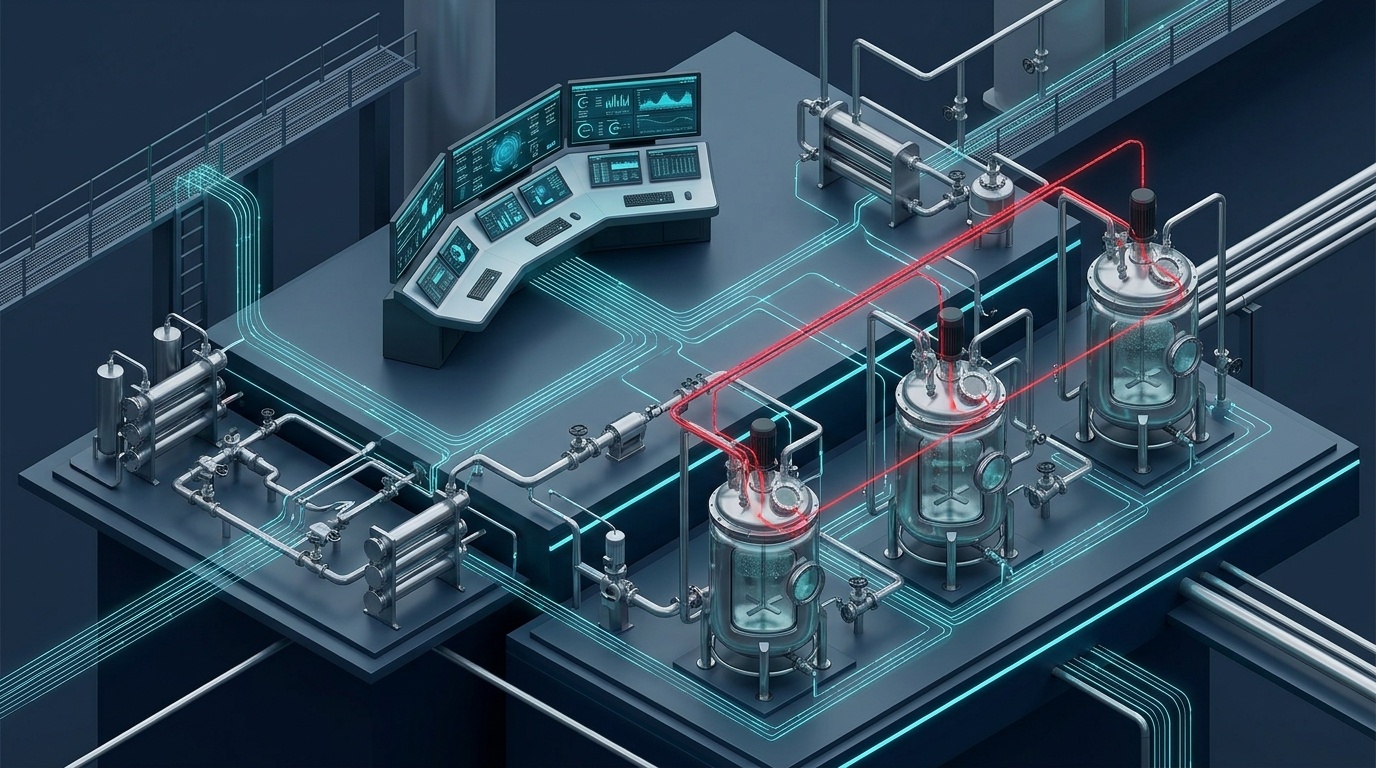
The flaw is located in the Batch Communication Service (BCS) daemon listening on dedicated TCP ports across the supervisory control network (Purdue Level 3). The service failed to enforce cryptographic authentication on incoming proprietary inter-process control messages.
| Vulnerability Parameter | Specification |
|---|---|
| Vulnerability Identifier | CVE-2026-79350 |
| CWE Classification | CWE-306 (Missing Authentication for Critical Function) |
| CVSS v3.1 Base Score | 9.4 (Critical) - CVSS:3.1/AV:A/AC:L/PR:N/UI:N/S:C/C:N/I:H/A:H |
| Impacted Releases | ABB Ability System 800xA 5.1, 6.0, 6.1 through 6.1.1 |
| Remediation Patch | ABB Hotfix Batch Management Rollup 6.1.1-HF3 / 6.2.0 |
An attacker positioned on the plant control LAN can send unauthenticated structured XML packets directly to the BCS listener. These packets can rewrite temperature profiles, reaction hold times, and ingredient dispensing tolerances in active master recipes without triggering operator alarm banners.
Operational Impact in Critical Manufacturing
In continuous and batch manufacturing environments, subtle deviations in recipe execution can cause severe physical and regulatory consequences:
- Contamination and Quality Failures: In pharmaceutical synthesis, altered stoichiometric ratios result in inactive or toxic compound production, requiring entire multi-million-dollar lots to be scrapped.
- Physical Safety Risks: In exothermic chemical synthesis, overriding reactor cooling phases or agitation speeds can lead to runaway thermal reactions and physical vessel ruptures.
- Regulatory Non-Compliance: Alterations break 21 CFR Part 11 electronic batch record integrity, halting facility certification and distribution pipelines.
Industrial Defensive Playbook (IEC 62443 Compliance)
Plant automation engineers and OT cybersecurity teams must execute the following remediation measures:
- Apply Official Vendor Hotfixes: Install ABB Hotfix Rollup 6.1.1-HF3 or upgrade to System 800xA 6.2.0, which enforces mutual TLS authentication across all Batch Management RPC endpoints.
- Zone & Conduit Segmentation (IEC 62443-3-2): Restrict access to the Batch Communication Service ports to authorized engineering workstations and Batch Servers using stateful industrial firewalls.
- Implement Deep Packet Inspection: Deploy OT intrusion detection sensors capable of decoding ABB proprietary RPC traffic to identify anomalous parameter rewrite requests.
- Enforce Dual-Authorization Controls: Configure safety-instrumented systems (SIS) to independently enforce hard physical process boundaries regardless of DCS recipe commands.