 Kubernetes
ORAS-Go Symlink Path Traversal Flaw Opens OCI Artifact Supply Chain to Compromise
ThreatsCloud & SaaSCVE-2026-85731High
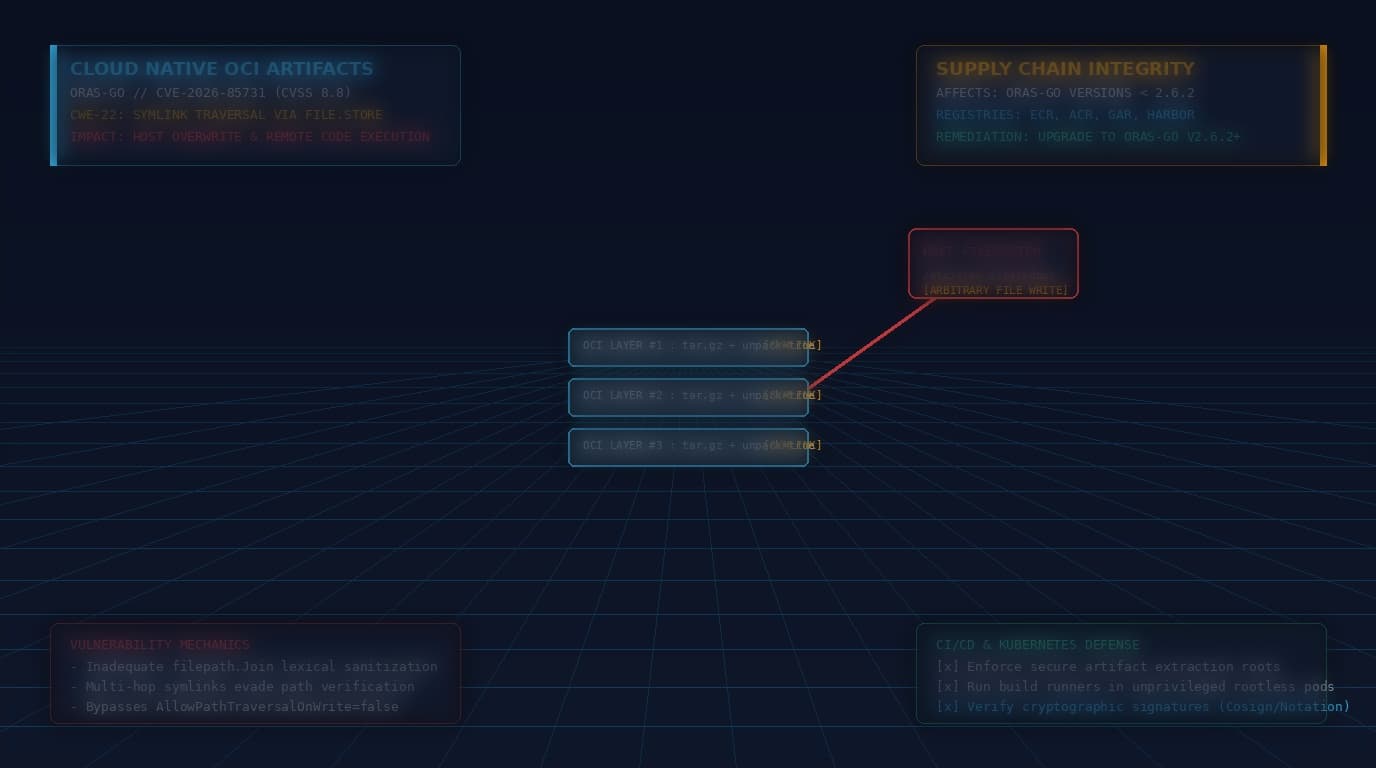
A high-severity CVSS 8.8 path traversal vulnerability in oras-go allows malicious OCI container artifacts to escape extraction roots and execute arbitrary code.
CST Editorial Desk16 min read